MTC: When Your Staff Leaves, Does Their Access Leave Too? 🔐 A SaaS Access Governance Checklist for Lawyers and Law Firms ⚖️

Law firms should Approve access deliberately and revoke risky permissions to protect client confidentiality.

Every law firm has a departure story. A paralegal moves on. A contract attorney finishes a document review. An associate shifts from litigation to transactional work. 👋 The farewell lunch happens. The laptop comes back. The email account gets shut off. Most firms call that "offboarding" and move on.

A recent 1Password* article, "SaaS access governance: Does access end when employees leave?," explains why that confidence is often misplaced. The piece is written for corporate IT teams. Its lessons apply with even greater force to lawyers. Our clients' confidential information lives in dozens of cloud tools, and our ethics rules do not accept "we thought IT handled it" as a defense.

The Problem: Access Outlives the Role 🚪
lawyers should Close the door on lingering SaaS access to protect every law-firm client.

The 1Password article makes a simple point. Disabling a person's main account does not remove every path back to your data. Many firms use a central login, often called single sign-on (SSO). Not every application connects to it. A former employee may still hold a working account in your e-signature platform, your file-sharing service, your project tracker, or an AI tool someone signed up for on a free trial.

Then there are the less visible doors. Shared credentials, personal accounts used for work, and OAuth connections can all survive a departure. OAuth is the "Sign in with Google" or "Allow this app to access your files" permission we click without much thought. Those permissions can persist until someone actively revokes them. 🔑

The article cites 1Password's 2025 Access-Trust Gap Report, which found that 38% of employees have successfully accessed a former employer's account. Read that number again. If it holds anywhere near true for law firms, client files may be one forgotten login away from exposure. 😬

Role changes create a quieter version of the same risk. The associate who moves practice groups keeps permissions from the old one. The contract lawyer keeps access to the shared workspace long after the engagement ends. Nobody acted improperly. Nobody looked at the full picture, either.

Why This Is an Ethics Issue, Not Just an IT Issue ⚖️
Track SaaS access activity to support law-firm audits and client-data protection.

The ABA Model Rules turn this operational gap into a professional responsibility question.

Rule 1.1 (Competence) and its Comment 8 require lawyers to keep abreast of the benefits and risks of relevant technology. Understanding who can reach your client data is part of that duty. 🧠

Rule 1.6(c) (Confidentiality) requires reasonable efforts to prevent unauthorized access to, or disclosure of, client information. A former staff member's live account in your document platform is precisely the kind of unauthorized access the rule contemplates. ABA Formal Opinion 477R reinforces that lawyers must understand how client information is transmitted and stored and must apply reasonable safeguards.

Rules 5.1 and 5.3 (Supervision) require firm managers to have measures in place that give reasonable assurance that lawyers and nonlawyers comply with professional obligations. An offboarding process that relies on memory is not a "measure." It is a hope. 📋

These supervisory duties now extend to AI tools. I discussed this in "My Two Cents: Lessons from ABA's Formal Opinion 512 - A Follow-Up!." If a staff member connected an AI application to your matter files, you need to know it exists. You also need to know when that connection ends.

The Five-Step Checklist, Translated for Law Firms ✅

The 1Password article offers five best practices. Here is how each one translates to a solo or small-to-midsize practice.
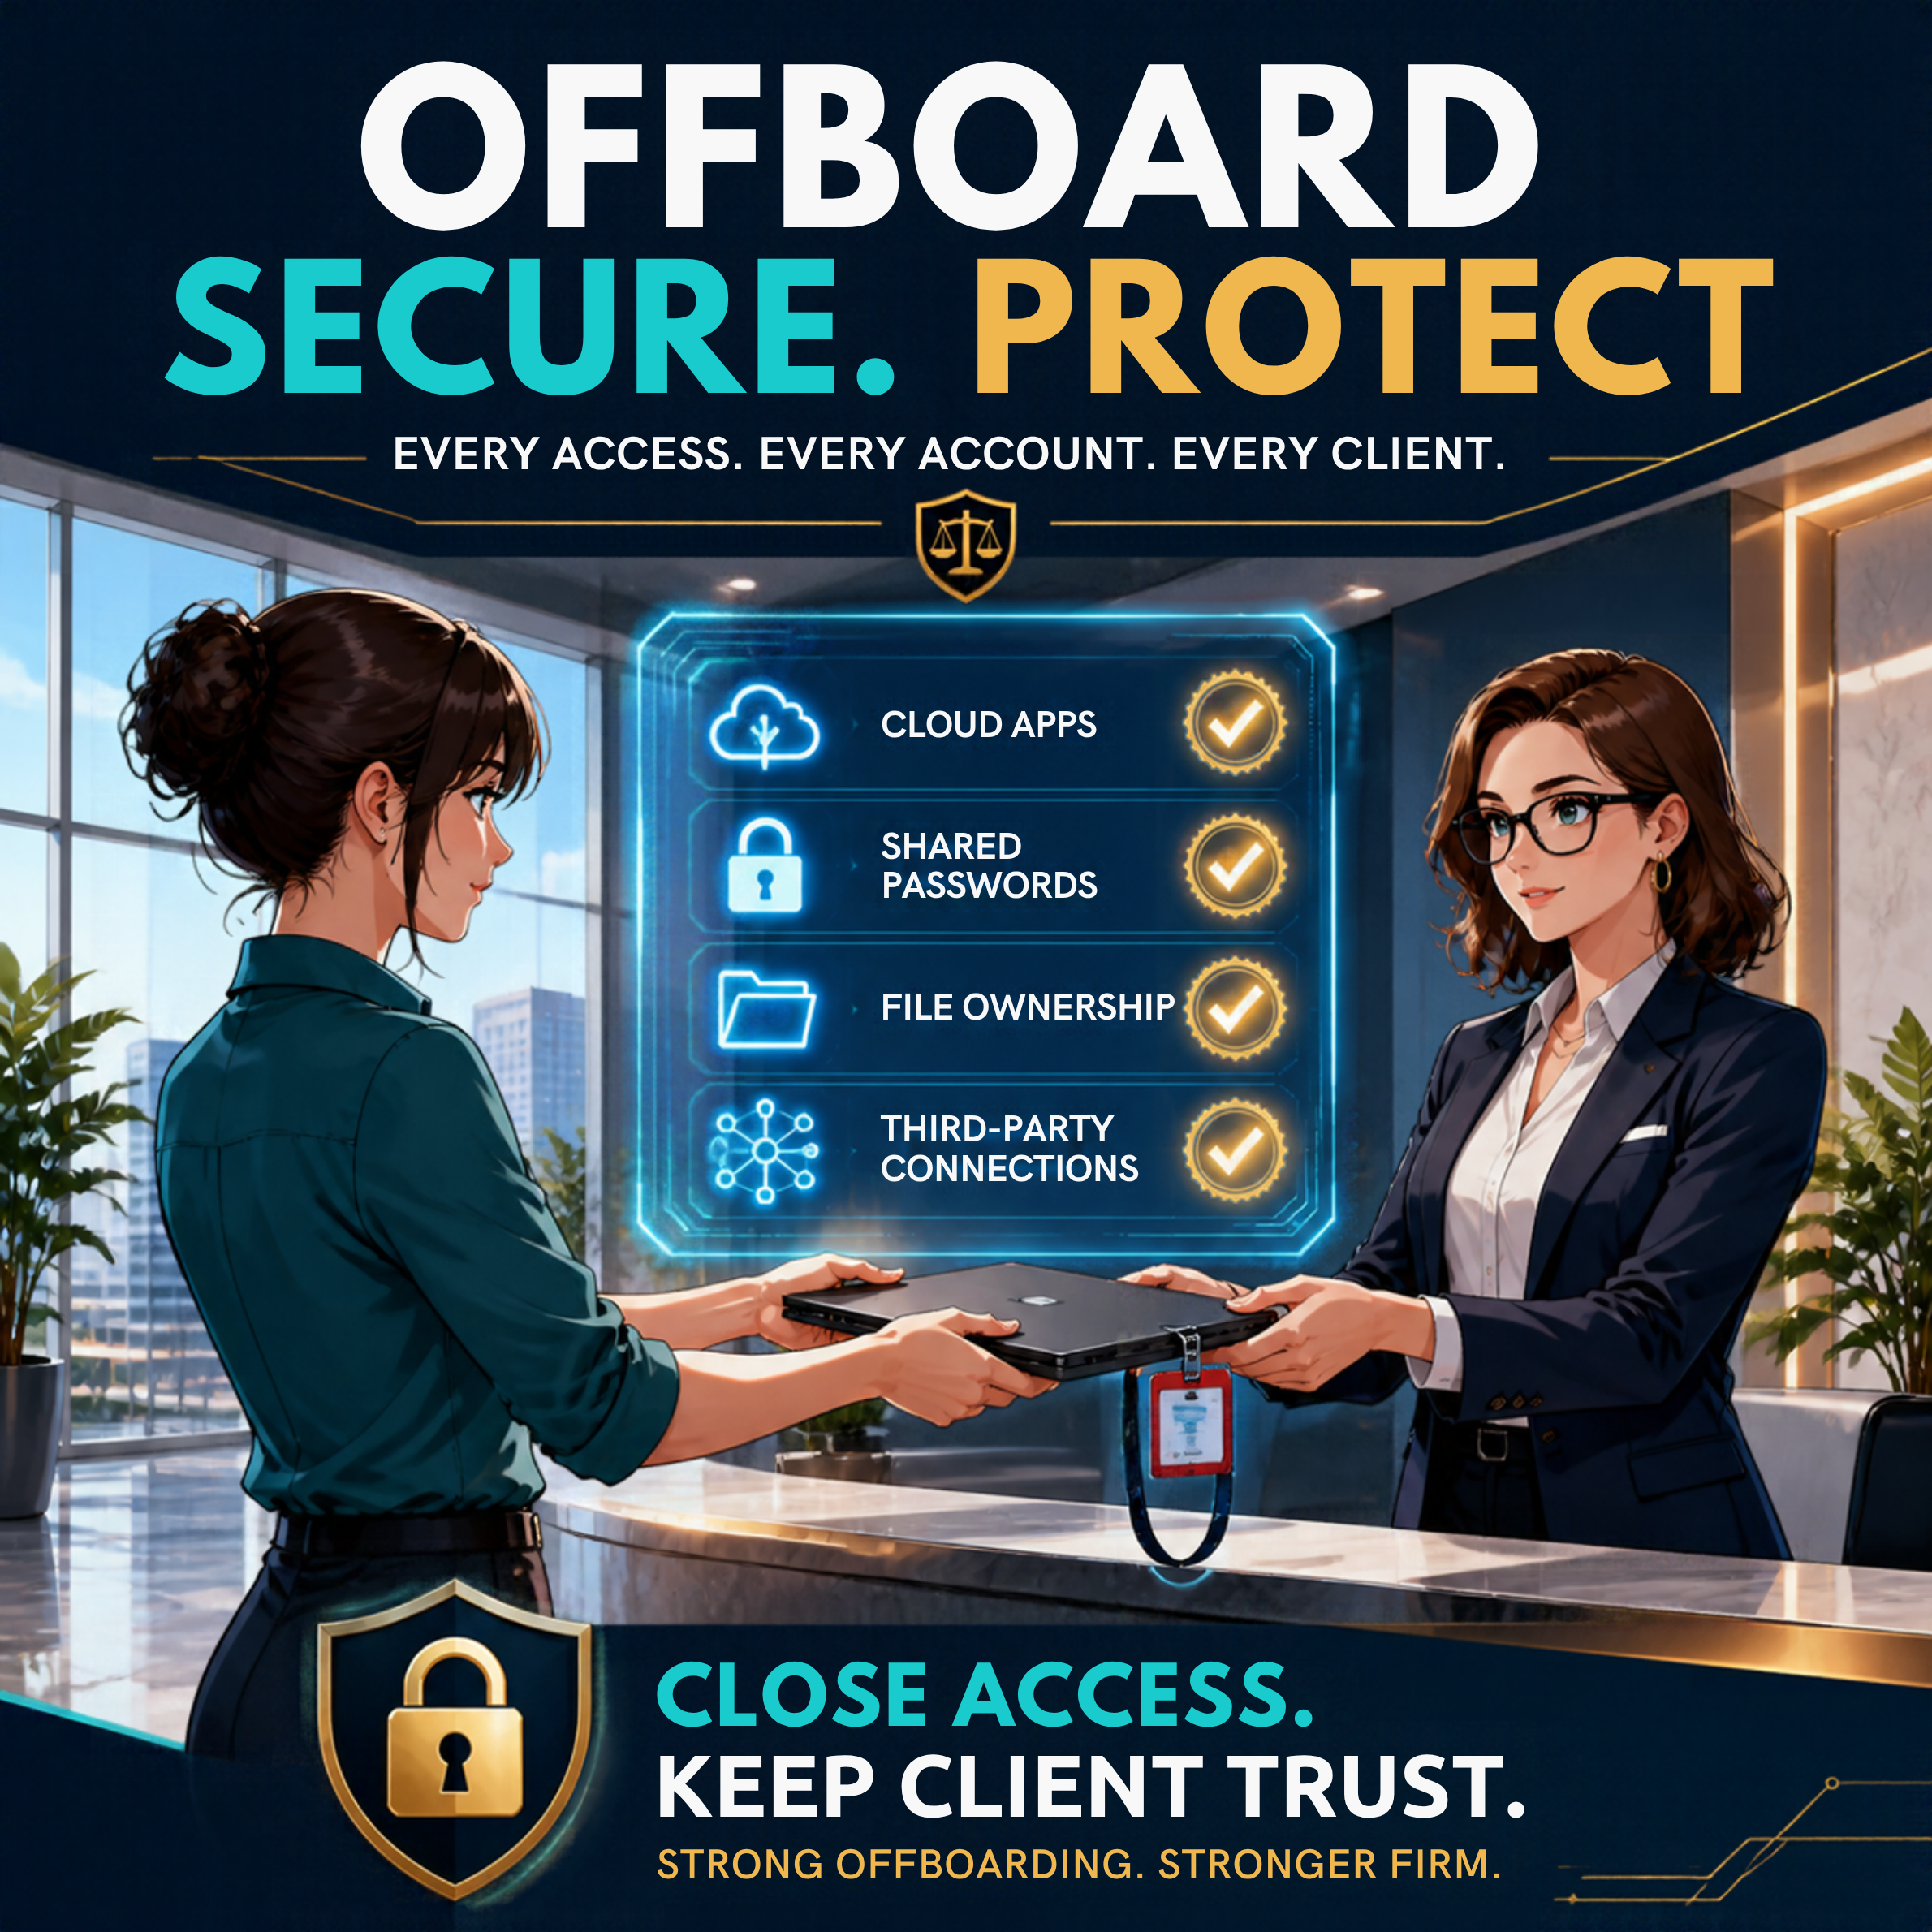
law firms should have A clear offboarding workflow to revoke SaaS access and protect law-firm clients.

1. Discover what your people actually use. 🔍 Build a simple inventory. List every application, shared login, and connected integration your firm relies on. Include tools adopted without formal approval. Ask your team directly. You will likely be surprised.

2. Tie access to lifecycle events. 🔄 Hiring, role changes, contract end dates, and departures should each trigger a written checklist. Assign an owner to every step. In a small firm, that owner may be you. Write it down anyway.

3. Apply least privilege when roles change. 🎯 Access should reflect current duties, not history. When someone moves from one practice area to another, remove the old permissions. I covered this principle in "📖 WORD OF THE WEEK (WoW): Zero Trust Architecture ⚖️🔐." The motto still applies: never trust, always verify.

4. Govern new SaaS and AI tools. 🤖 Create a clear way for staff to request new tools. Review what data each tool can reach before approving it. Assign an owner to every approved application. The 1Password article makes a point I strongly endorse: AI tools belong inside your broader software governance, not in a separate silo.

5. Verify removal and keep proof. 🧾 Offboarding is complete only when you can show access is gone from every relevant system. That means outside-SSO apps, OAuth connections, shared passwords, file ownership, and paid seats. Keep a short record of who closed each item and when. Use a second reviewer for departures involving privileged access. Then test the process periodically before a real departure tests it for you.

Practical Steps You Can Take This Week 🛠️
SaaS access governance helps law firms securely offboard users and protect client confidentiality.

You do not need an enterprise platform to start. A password manager with shared vaults lets you rotate credentials quickly when someone leaves. Most cloud platforms, including Microsoft 365 and Google Workspace, let administrators review and revoke third-party app connections. A one-page offboarding checklist, saved in your firm's policy folder, is a meaningful first step.

Larger firms may benefit from dedicated tools. 1Password promotes its SaaS Manager for discovery, automated provisioning, and OAuth revocation. As with any vendor, evaluate it under Rule 5.3 and your own risk profile. My earlier post, "My Two Cents: Essential Security and Privacy Reminder for Lawyers Using Cloud Software," offers a foundation for that review. 💡

My Two Cents 💭

MTC
*
Product used by this blogger! This is not an endorsement per se, nor is this a guarantee of any kind. You still have an independent duty to review software before implementing it into your practice.
🔒 Word (Phrase) of the Week: “Zero Data Retention” Agreements: Why Every Lawyer Must Pay Attention Now!

Understanding Zero Data Retention in Legal Practice

🚨 Lawyers Must Know Zero Data Retention Now!

Zero Data Retention (ZDR) agreements represent a fundamental shift in how law firms protect client confidentiality when using third-party technology services. These agreements ensure that sensitive client information is processed but never stored by vendors after immediate use. For attorneys navigating an increasingly digital practice environment, understanding ZDR agreements has become essential to maintaining ethical compliance.

ZDR works through a simple but powerful principle: access, process, and discard. When lawyers use services with ZDR agreements, the vendor connects to data only when needed, performs the requested task, and immediately discards all information without creating persistent copies. This architectural approach dramatically reduces the risk of data breaches and unauthorized access.

The Legal Ethics Crisis Hidden in Your Vendor Contracts

Recent court orders have exposed a critical vulnerability in how lawyers use technology. A federal court ordered OpenAI to preserve all ChatGPT conversation logs indefinitely, including deleted content—even for paying subscribers. This ruling affects millions of users and demonstrates how quickly data retention policies can change through litigation.

The implications for legal practice are severe. Attorneys using consumer-grade AI tools, standard cloud storage, or free collaboration platforms may unknowingly expose client confidences to indefinite retention. This creates potential violations of fundamental ethical obligations, regardless of the lawyer's intent or the vendor's original promises.

ABA Model Rules Create Mandatory Obligations

Three interconnected ABA Model Rules establish clear ethical requirements for lawyers using technology vendors.

Rule 1.1 and its Comment [8] requires technological competence. Attorneys must understand "the benefits and risks associated with relevant technology". This means lawyers cannot simply trust vendor marketing claims about data security. They must conduct meaningful due diligence before entrusting client information to any third party.

Rule 1.6 mandates confidentiality protection. Lawyers must "make reasonable efforts to prevent the inadvertent or unauthorized disclosure of, or unauthorized access to, information relating to the representation of a client". This obligation extends to all digital communications and cloud-based storage. When vendors retain data beyond the immediate need, attorneys face heightened risks of unauthorized disclosure.

Rule 5.3 governs supervision of nonlawyer assistants. This rule applies equally to technology vendors who handle client information. Lawyers with managerial authority must ensure their firms implement measures that provide reasonable assurance that vendors comply with the attorney's professional obligations.

Practical Steps for Ethical Compliance

Attorneys must implement specific practices to satisfy their ethical obligations when selecting technology vendors.

1. Demand written confirmation of zero data retention policies from all vendors handling client information. Ask whether the vendor uses client data for training AI models. Determine how long any data remains accessible after processing. These questions must be answered clearly before using any service.

Lawyers Need Zero Data Retention Agreements!

Review vendor agreements carefully. Standard terms of service often fail to provide adequate confidentiality protections. Attorneys should negotiate explicit contractual provisions that prohibit data retention beyond immediate processing needs. These agreements must specify encryption standards, access controls, and breach notification procedures.

Obtain client consent when using third-party services that may access confidential information. While not always legally required, informed consent demonstrates respect for client autonomy and provides an additional layer of protection.

Conduct ongoing monitoring of vendor practices. Initial due diligence is insufficient. Technology changes rapidly, and vendors may alter their data handling practices. Regular reviews ensure continued compliance with ethical obligations.

Restrict employee use of unauthorized tools. Many data breaches stem from "shadow IT"—employees using personal accounts or unapproved services for work purposes. Clear policies and training can prevent inadvertent ethical violations.

The Distinction Between Consumer and Enterprise Services

Not all AI and cloud services create equal ethical risks. Consumer versions of popular tools often lack the security features required for legal practice. Enterprise subscriptions typically provide enhanced protections, including zero data retention options.

For example, OpenAI offers different service tiers with dramatically different data handling practices. ChatGPT Free, Plus, Pro, and Team subscriptions now face indefinite data retention due to court orders. However, ChatGPT Enterprise and API customers with ZDR agreements remain unaffected. This distinction matters enormously for attorney compliance.

Industry-Specific Legal AI Offers Additional Safeguards

Legal-specific AI platforms build confidentiality protections into their core architecture. These tools understand attorney-client privilege requirements and design their systems accordingly. They typically offer encryption, access controls, SOC 2 compliance, and explicit commitments not to use client data for training.

When evaluating legal technology vendors, attorneys should prioritize those offering private AI environments, end-to-end encryption, and contractual guarantees about data retention. These features align with the ethical obligations imposed by the Model Rules.

Zero Data Retention as Competitive Advantage

Beyond ethical compliance, ZDR agreements offer practical benefits. They reduce storage costs, simplify regulatory compliance, and minimize the attack surface for cybersecurity threats. In an era of increasing data breaches, the ability to tell clients that their information is never stored by third parties provides meaningful competitive differentiation.

Final Thoughts: Action Required Now

Lawyers must Protect Client Data with ZDR!

The landscape of legal technology changes constantly. Court orders can suddenly transform data retention policies. Vendors can modify their terms of service. New ethical opinions can shift compliance expectations.

Attorneys cannot afford passive approaches to vendor management. They must actively investigate, negotiate, and monitor the data handling practices of every technology provider accessing client information. Zero data retention agreements represent one powerful tool for maintaining ethical compliance in an increasingly complex technological environment.

The duty of confidentiality remains absolute, regardless of the tools lawyers choose. By demanding ZDR agreements and implementing comprehensive vendor management practices, attorneys can embrace technological innovation while protecting the fundamental trust that defines the attorney-client relationship.

MTC: Judicial Warnings - Courts Intensify AI Verification Standards for Legal Practice ⚖️

Lawyers always need to check their work - AI is not infalable!

The legal profession faces an unprecedented challenge as federal courts nationwide impose increasingly harsh sanctions on attorneys who submit AI-generated hallucinated case law without proper verification. Recent court decisions demonstrate that judicial patience for unchecked artificial intelligence use has reached a breaking point, with sanctions extending far beyond monetary penalties to include professional disbarment recommendations and public censure. The August 2025 Mavy v. Commissioner of SSA case exemplifies this trend, where an Arizona federal judge imposed comprehensive sanctions including revocation of pro hac vice status and mandatory notification to state bar authorities for fabricated case citations.

The Growing Pattern of AI-Related Sanctions

Courts across the United States have documented a troubling pattern of attorneys submitting briefs containing non-existent case citations generated by artificial intelligence tools. The landmark Mata v. Avianca case established the foundation with a $5,000 fine, but subsequent decisions reveal escalating consequences. Recent sanctions include a Wyoming federal court's revocation of an attorney's pro hac vice admission after discovering eight of nine cited cases were AI hallucinations, and an Alabama federal court's decision to disqualify three Butler Snow attorneys from representation while referring them to state bar disciplinary proceedings.

The Mavy case demonstrates how systematic citation failures can trigger comprehensive judicial response. Judge Alison S. Bachus found that of 19 case citations in attorney Maren Bam's opening brief, only 5 to 7 cases existed and supported their stated propositions. The court identified three completely fabricated cases attributed to actual Arizona federal judges, including Hobbs v. Comm'r of Soc. Sec. Admin., Brown v. Colvin, and Wofford v. Berryhill—none of which existed in legal databases.

Essential Verification Protocols

Lawyers if you fail to check your work when using AI, your professional career could be in jeopardy!

Legal professionals must recognize that Federal Rule of Civil Procedure 11 requires attorneys to certify the accuracy of all court filings, regardless of their preparation method. This obligation extends to AI-assisted research and document preparation. Courts consistently emphasize that while AI use is acceptable, verification remains mandatory and non-negotiable.

The professional responsibility framework requires lawyers to independently verify every AI-suggested citation using official legal databases before submission. This includes cross-referencing case numbers, reviewing actual case holdings, and confirming that quoted material appears in the referenced decisions. The Alaska Bar Association's recent Ethics Opinion 2025-1 reinforces that confidentiality concerns also arise when specific prompts to AI tools reveal client information.

Best Practices for Technology Integration 📱

Technology-enabled practice enhancement requires structured verification protocols. Successful integration involves implementing retrieval-based legal AI systems that cite original sources alongside their outputs, maintaining human oversight for all AI-generated content, and establishing peer review processes for critical filings. Legal professionals should favor platforms that provide transparent citation practices and security compliance standards.

The North Carolina State Bar's 2024 Formal Ethics Opinion emphasizes that lawyers employing AI tools must educate themselves on associated benefits and risks while ensuring client information security. This competency standard requires ongoing education about AI capabilities, limitations, and proper implementation within ethical guidelines.

Consequences of Non-Compliance ⚠️

Recent sanctions demonstrate that monetary penalties represent only the beginning of potential consequences. Courts now impose comprehensive remedial measures including striking deficient briefs, removing attorneys from cases, requiring individual apology letters to falsely attributed judges, and forwarding sanction orders to state bar associations for disciplinary review. The Arizona court's requirement that attorney Bam notify every judge presiding over her active cases illustrates how sanctions can impact entire legal practices.

Professional discipline referrals create lasting reputational consequences that extend beyond individual cases. The Second Circuit's decision in Park v. Kim established that Rule 11 duties require attorneys to "read, and thereby confirm the existence and validity of, the legal authorities on which they rely". Failure to meet this standard reveals inadequate legal reasoning and can justify severe sanctions.

Final Thoughts - The Path Forward 🚀

Be a smart lawyer. USe AI wisely. Always check your work!

The ABA Journal's coverage of cases showing "justifiable kindness" for attorneys facing personal tragedies while committing AI errors highlights judicial recognition of human circumstances, but courts consistently maintain that personal difficulties do not excuse professional obligations. The trend toward harsher sanctions reflects judicial concern that lenient approaches have proven ineffective as deterrents.

Legal professionals must embrace transparent verification practices while acknowledging mistakes promptly when they occur. Courts consistently show greater leniency toward attorneys who immediately admit errors rather than attempting to defend indefensible positions. This approach maintains client trust while demonstrating professional integrity.

The evolving landscape requires legal professionals to balance technological innovation with fundamental ethical obligations. As Stanford research indicates that legal AI models hallucinate in approximately one out of six benchmarking queries, the imperative for rigorous verification becomes even more critical. Success in this environment demands both technological literacy and unwavering commitment to professional standards that have governed legal practice for generations.

MTC