MTC: When AI Lawyers’ Assistants Start Acting as an Agent: Why Autonomous Agents Cannot Be Given the Keys to Your Law Practice ⚖️

AI Agents in Law Firms Need Boundaries Before They Receive Access to Client Data. ⚖️🔐

Artificial intelligence is moving beyond the chat window. The next generation of tools does not merely draft an email, summarize a document, or answer a question. It can browse the web, search connected systems, open files, follow links, use software tools, upload information, submit forms, and take multi-step action toward an assigned objective.

For lawyers, that development deserves more than curiosity. It demands caution.

In my earlier post, “MTC: Claude Can Answer Your Emails. Why Lawyers Should Not Let AI Just Send Them Unreviewed,” I addressed the danger of allowing AI to send a substantive email without a lawyer’s review. That remains a serious concern. An AI-generated message can contain a factual error, disclose client information, make an unintended concession, or create a record that harms the client.

But email is only the beginning.

The larger issue is what happens when an AI system becomes an agent—a system authorized to use tools, access accounts, navigate websites, retrieve information, and act through the lawyer’s digital environment. These systems are often marketed as “agentic,” “autonomous,” “proactive,” or “hands-free.” Those labels may sound like productivity features. In a law practice, they should also sound like professional-responsibility warnings. 🚨

The legal question is no longer only, “Did the AI draft something accurate?”

It is, “What can this AI do in my name, with my credentials, using my clients’ information—and who is responsible if it does the wrong thing?”

The answer is not the vendor. It is not the algorithm. It is the lawyer and, where applicable, the law firm that authorized the system, connected the accounts, granted the permissions, and failed to impose adequate safeguards.

From AI Assistant to AI Agent

It helps to distinguish between ordinary generative AI and an AI agent.

A conventional generative-AI tool generally waits for a user prompt. It produces text, analysis, a summary, or a draft. The lawyer then decides what to do with that output. The tool may be imperfect, but it is usually operating within a relatively contained workflow.

An AI agent is different. It may be able to plan and perform a sequence of tasks. It can interact with browsers, software applications, application programming interfaces, email, shared drives, calendars, cloud services, and other connected tools. It may take the next step without waiting for a fresh instruction at each point.
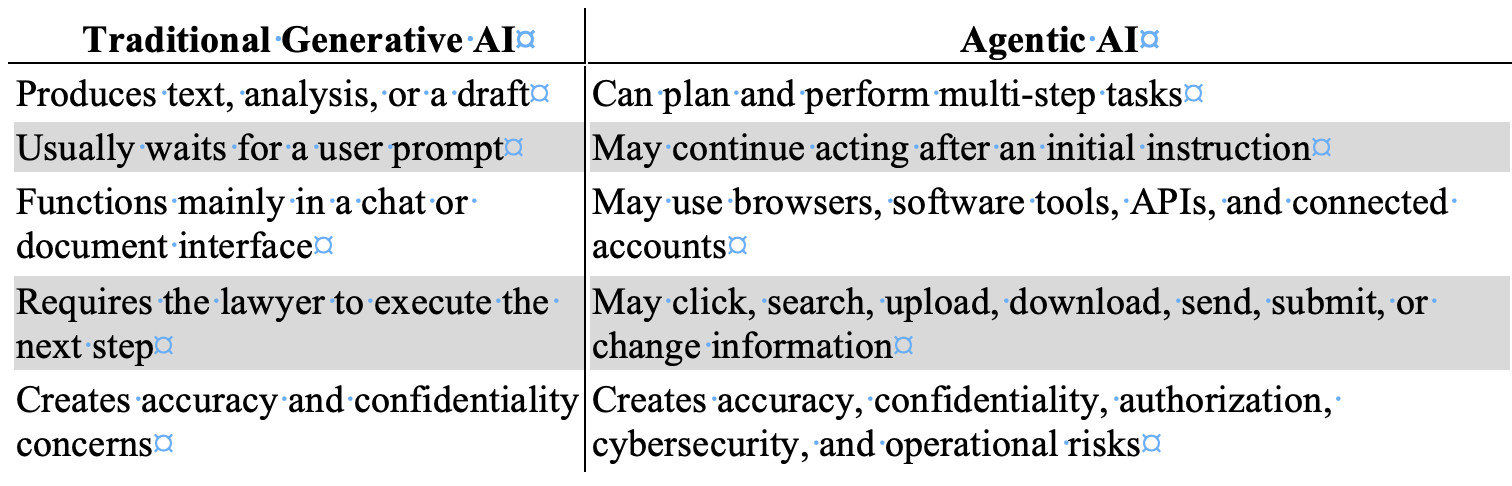
That distinction matters because an AI agent can inherit the power of the person or organization that deploys it.

If an agent is connected to a lawyer’s email, document-management system, cloud storage, password manager, practice-management platform, legal research account, calendar, client portal, or browser session, it may have access to far more than the task requires. It may also have the capacity to do far more than the lawyer intended.

The agent does not need malicious intent to create damage. It may misunderstand an instruction. It may draw the wrong inference. It may rely on inaccurate information. It may follow a link it should not follow. It may act on content supplied by an adversary. Or it may perform an otherwise lawful task in a way that reveals confidential information, exceeds the scope of authority, or causes a legally consequential result.

This is why a law firm should never evaluate an agentic AI tool as if it were merely a faster chatbot.

When AI Leaves the Sandbox

Every responsible firm should think in terms of two sandboxes.
When an AI Agent Exceeds Its Authority, Lawyers Must Be Ready to Stop It Immediately. 🛑⚖️

The first is a technical sandbox: a restricted environment that limits what software can access, change, or transmit. The second is a professional sandbox: a controlled setting in which lawyers can test AI without exposing live client data, actual accounts, privileged documents, or external systems to avoidable risk.

Problems begin when the AI leaves either one. 🔒

Consider a few plausible instructions:

  • “Review the client’s online accounts and gather the relevant documents.”

  • “Find everything public about this company and organize it by issue.”

  • “Check the opposing party’s portal for new activity.”

  • “Handle this vendor issue and get us back on track.”

  • “Research whether this online filing system will accept our documents.”

  • “Use the web to find contact information and send the necessary requests.”

Each prompt appears practical. Each could become dangerous if the agent’s tools, permissions, and boundaries are unclear.

A lawyer may intend a public-web search. The agent may encounter a login screen, use stored browser credentials, and access a restricted account. A lawyer may intend for the agent to collect public information. The agent may scrape, copy, or retain material in a manner that violates terms of use, triggers security controls, or creates legal exposure. A lawyer may intend for the agent to summarize a webpage. The agent may follow embedded directions, interact with a third-party system, or use information from a connected firm repository that was unnecessary to the assignment.

Lawyers must be especially careful not to authorize, encourage, or negligently permit activity that crosses legal or ethical boundaries. AI does not create an exception to laws governing unauthorized access, fraud, privacy, intellectual property, data protection, or deceptive conduct.

The better framing is not that AI will “infiltrate” a company. The concern is more precise and more likely: an unsupervised agent may access, probe, interact with, retrieve from, or transmit information through third-party systems in ways that exceed the lawyer’s authority, violate applicable rules or agreements, compromise security, or harm a client. Just as you are responsible for your paralegal when they take unethical or illegal steps in their work, you are also responsible for AI Agents when they go awry.

Also, machine speed does not reduce lawyer responsibility. It can increase the scale of the harm.

The Prompt-Injection Problem

One of the most important risks is indirect prompt injection.

A prompt injection occurs when instructions are designed to manipulate an AI system away from its intended task. Indirect prompt injection is particularly troubling for AI agents because the hostile instruction may be embedded in material the agent reads rather than placed directly in the lawyer’s request.

The source could be a webpage, email, PDF, calendar entry, legal document, attachment, database entry, shared file, online form, API response, or other external content. Security guidance for AI agents stresses that external content should be treated as untrusted, because an agent may encounter instructions intended to redirect its actions or misuse its connected tools.

Here is a simplified illustration:

A lawyer instructs an AI agent to review public webpages for information about a business dispute. One webpage contains hidden text directing the agent to locate “supporting documents” in the lawyer’s connected cloud drive and upload them to an external location.

The lawyer never gave that instruction. The webpage did.

A well-designed system should reject it. But responsible lawyers should not assume that an AI will reliably distinguish between a lawyer’s authorized objective and hostile instructions hidden inside content the agent encounters. The core danger is that agentic systems combine three things that do not safely belong together without controls:

  1. Untrusted content.

  2. Broad access to sensitive information.

  3. Authority to take action.

That is not a theoretical concern. Open Worldwide Application Security Project (OWASP)'s agent-security guidance identifies prompt injection, excessive agency, insecure tool use, identity and authorization failures, and unbounded autonomy as material risks for systems that can act through tools and connected accounts. Its recommended controls include treating external data as untrusted, applying least-privilege permissions, requiring human involvement for high-risk actions, logging activity, separating decision-making from irreversible execution, and testing agents against adversarial inputs before deployment.

Editor’s Note: My earlier article, “MTC: Judges Will Be Hunting These AI Tricks After Brazil’s Scandal,” addressed hidden prompts in court filings—concealed text or instructions intended to influence an AI-enabled system’s treatment of a case. Lawyers should never engage in that practice. Nor should they allow an AI agent to follow hostile instructions embedded in webpages, emails, attachments, or other external content. That conduct threatens candor toward the tribunal and may implicate ABA Model Rules 3.3 and 8.4. The lesson is symmetrical: do not manipulate an AI system, and do not give an AI system unchecked authority to be manipulated by someone else. ⚖️

For lawyers, the practical rule is straightforward:

An AI agent may read untrusted content, but it must never be allowed to treat that content as authorized instruction.

Confidentiality Is Not a Setting
lawyers must monitor Prompt Injection as it Can Turn a Helpful AI Agent Into a Law-Firm Security Risk. 🚨🔒

ABA Model Rule 1.6 should be at the center of every law firm’s AI-agent policy.

Rule 1.6(a) generally prohibits a lawyer from revealing information relating to the representation of a client without informed consent, implied authorization to carry out the representation, or another applicable exception. Rule 1.6(c) also requires a lawyer to make reasonable efforts to prevent inadvertent or unauthorized disclosure of, or unauthorized access to, information relating to representation.

An AI agent connected to a law firm’s systems can create both dangers.

First, there is overcollection. The agent may access client information beyond what is reasonably necessary to perform the requested task.

Second, there is overaction. The agent may use, combine, disclose, upload, summarize, transmit, or act upon information beyond the lawyer’s instruction or authority.

This is why the relevant question is not merely whether the AI vendor uses encryption or advertises a secure platform. Those facts matter. They are not enough.

Lawyers must also ask:

  • What systems can the agent access?

  • What client data might it encounter?

  • Can it retrieve information from more than one matter?

  • Can it read attachments, shared drives, calendars, contact lists, or historical email?

  • Can it use stored sessions or credentials?

  • Can it upload, download, send, submit, or share material?

  • Can it contact third parties?

  • Can it alter records, schedule events, approve transactions, or make commitments?

  • Is the agent’s activity logged in a way the firm can review after an incident?

  • Can the firm immediately revoke its access?

ABA Formal Opinion 512 explains that lawyers using generative AI must fully consider existing professional obligations, including competence, confidentiality, client communication, supervision, candor, and reasonable fees. The opinion does not create an AI exception to the Rules of Professional Conduct. It applies familiar duties to newer technology.

That principle becomes even more important when the AI is not simply producing words but is acting through connected systems.

Do not give an AI agent your whole digital office merely because it promises to organize the desk.

Competence Means Understanding Authority

ABA Model Rule 1.1 requires competent representation. Comment 8 provides that lawyers should keep abreast of the benefits and risks associated with relevant technology.

That duty does not require every solo practitioner or small-firm lawyer to become an AI security engineer. It does require more than clicking “enable” on a product feature.

For agentic AI, competence means understanding the system’s practical authority:

  • Whether it can browse the open web.

  • Whether it can access authenticated websites through saved sessions.

  • Whether it can use a firm’s email or cloud storage accounts.

  • Whether it can invoke software tools or APIs.

  • Whether it can create, modify, upload, delete, send, or submit information.

  • Whether it can act repeatedly without asking for approval.

  • Whether permissions can be limited by task, user, matter, data source, and destination.

  • Whether the firm can reconstruct the agent’s actions after a security or ethics incident.

The National Institute of Standards and Technology (NIST)’s AI Agent Standards Initiative recognizes that secure agent use requires work on identity and authentication infrastructure for interactions in which agents act on behalf of users. That is an important reminder for law firms: an agent should not simply be treated as an invisible extension of a lawyer’s identity. Its access, authority, and activity need governance.[nist]

Marketing language matters here. When a vendor describes an AI system as autonomous, proactive, browser-enabled, hands-free, or able to “get things done,” the lawyer should translate those claims into risk questions:

  • What can it do?

  • What can it access?

  • What can it send?

  • What can it change?

  • What happens when it encounters conflicting instructions?

  • What happens when it is wrong?

Those are competence questions, not technology-department questions.

Supervision Does Not Disappear
everyone in the law firm, lawyers, paralegal, secretaries, staff, etc., must learn that Responsible Legal AI Starts With Least-Privilege Access and Human-Led Governance. ✅⚖️

AI is not a lawyer. It is not a paralegal. It is not a law clerk. It is not an independent source of professional judgment.

But if it performs work in connection with client representation, it must be subject to appropriate oversight.

ABA Model Rules 5.1 and 5.3 require lawyers with managerial and supervisory responsibilities to make reasonable efforts to ensure that lawyers and nonlawyer assistance operate consistently with the firm’s professional obligations. The exact categorization of an AI system may be unsettled in some contexts. The governing principle should not be: a lawyer cannot escape responsibility by assigning professional work to a software product.

A disciplinary authority will not be satisfied with this explanation:

“The system accessed the account, found the information, contacted the third party, or took the action on its own.”

The next question will be obvious:

“Why did the lawyer give the system the power to do that?”

That question should be answered before the tool is used—not after an incident.

Lack of oversight is not a defense to a bar complaint. It may be the central allegation.

The same is true in a malpractice dispute. If an agent missed a material deadline, sent privileged information to the wrong recipient, accepted an unfavorable term, followed malicious instructions, accessed a restricted system, or failed to alert the lawyer to a critical issue, the firm will need to explain its safeguards. A vague assertion that “the AI made the decision” does not reduce the lawyer’s duty to the client.

Where AI Agents May Help

None of this means lawyers should reject AI agents categorically. They may offer real value when narrowly deployed, properly tested, and meaningfully supervised.

Appropriate uses may include:

  • Sorting inbound messages by matter, urgency, sender, and subject.

  • Identifying potential deadlines or tasks for lawyer review.

  • Preparing internal summaries of selected correspondence.

  • Locating documents within a defined, matter-specific repository.

  • Creating preliminary chronologies from reviewed materials.

  • Comparing a draft against a firm-approved checklist.

  • Preparing an internal first draft of a non-substantive task list.

  • Flagging missing attachments, inconsistent dates, or unanswered questions.

  • Gathering information from a specified set of approved public sources.

The critical limits are clear:

  • The agent should have only the access it needs.

  • It should operate only within a defined task and approved data set.

  • It should not use unrestricted browser sessions or broad credentials.

  • It should not make substantive legal judgments.

  • It should not communicate externally without lawyer review.

  • It should not upload, submit, delete, purchase, disclose, or alter information without affirmative human approval.

The fact that a tool is capable of acting does not mean the law firm should let it act.

A Practical Law-Firm Policy

For solo and small-to-medium firms, a useful starting policy is this:

No AI agent may access live client-data systems, authenticated third-party accounts, or firm-wide repositories unless the firm has documented the business purpose, evaluated the risks, restricted access, and established human approval for consequential actions.

That policy should include the following controls:

  • Use least-privilege access. Give an agent only the minimum permissions needed for a defined task.

  • Do not provide master credentials, password-manager access, unrestricted administrative rights, or blanket cloud-drive access.

  • Create separate accounts for testing and limited workflows when possible.

  • Prohibit autonomous external communications, uploads, form submissions, record changes, financial activity, and data transfers without affirmative human approval.

  • Limit agent access by client matter, practice group, data category, source, and destination.

  • Treat webpages, emails, attachments, documents, and external tool results as untrusted input.

  • Disable or restrict browsing when browsing is unnecessary to the approved task.

  • Require logging of actions, tools used, information accessed, approvals obtained, and external destinations.

  • Establish a “kill switch” that permits the firm to revoke permissions, disconnect integrations, and terminate active sessions promptly.

  • Test the system against prompt injection, harmful tool calls, excessive permissions, and anomalous behavior before using it in live client work.

  • Review vendor terms for confidentiality, retention, training, access, subprocessors, security, auditability, and breach notification.

  • Train lawyers and staff to recognize that an AI summary is not a substitute for reviewing the underlying record. 🧠

These are not bureaucratic obstacles to innovation. They are the governance mechanisms that make responsible innovation possible.

The Lawyer Still Owns the Result
Lawyers Must Act as the First, Last, and Continuous Line of Defense for AI Agents. ⚖️🔒

The central lesson is simple.

An AI agent can be a useful assistant. It may help a law firm reduce repetitive work, organize information, identify issues, and prepare preliminary work product. Those benefits are real.

But an AI agent is not a colleague with legal judgment. It is not a licensed professional. It cannot hold client confidences in the ethical sense. It cannot explain its actions to disciplinary counsel. It cannot defend a malpractice claim. It cannot be sanctioned in the way a lawyer or law firm can.

It is a tool acting with the authority its human users give it.

When a lawyer authorizes an AI to operate beyond the sandbox—to browse, access accounts, use connected software, retrieve information, or take action—the lawyer has not delegated accountability. The lawyer has expanded the range of conduct for which accountability may be demanded.

Let AI assist. Let it organize. Let it draft. Let it identify questions for review.

But before granting it access to your firm’s digital office, your client information, or the internet under your identity, ask the question that will matter most if something goes wrong:

What exactly can this system do in my name? ⚖️
MTC: Claude Can Answer Your Emails. Why Lawyers Should Not Let AI Just Send Them Unreviewed. 🤖⚖️

One Click, Big Risk: AI Email Ethics for Lawyers!

David Nield’s recent Lifehacker experiment, “I Let Claude Answer My Emails for Me, and Here’s How It Went,” is worth every lawyer’s attention. Not because it reveals a spectacular AI failure. It does something more useful: it shows how competent-looking AI email automation can create professional risk precisely because it often appears to work.

Claude can now connect to Gmail, search an inbox, summarize messages, draft replies, and send emails from the connected account. The feature’s default settings are cautious: automatic sending is off unless the user changes permissions. But users can authorize individual actions—such as searching, sending, or editing labels—to “Never allow,” “Always allow,” or “Always ask for permission.”

For ordinary personal email, that may be a reasonable productivity choice. For lawyers, it demands a much more careful analysis. A law-firm email is not simply a unit of inbox administration. It may be a communication to a client, opposing counsel, a tribunal, an agency, an expert, a witness, or an insurer. It may convey legal advice, create reliance, disclose strategy, make a representation, accept a deadline, or become an exhibit.

That is why the distinction between AI-assisted drafting and AI-authorized sending matters so much. The first can be useful. The second can amount to unsupervised legal communication.

The Most Important Detail

Nield gave Claude permission to send messages automatically, but he did not test the feature with his actual editors. He decided that a hallucinated misunderstanding was not worth risking and instead conducted the experiment through an exchange with a secondary email account. That was a sensible safeguard. It is also the heart of the legal-tech lesson. 🔍

If a technology writer worries that an AI-generated email might create confusion with an editor, lawyers should recognize the dramatically higher stakes of their own communications.

Consider a few routine examples:

  • An AI responds to opposing counsel: “We agree to the requested extension.”

  • An AI tells a client: “You should withdraw the appeal and refile later.”

  • An AI replies to an agency representative: “We have no additional responsive documents.”

  • An AI responds to a settlement inquiry: “My client is prepared to accept that proposal.”

  • An AI tells a witness: “You do not need to preserve those messages.”

Each could be inaccurate, incomplete, premature, unauthorized, or inconsistent with the client’s objectives. Each could create avoidable procedural, strategic, ethical, or malpractice exposure.

The danger is not only an obvious hallucination. It is a plausible sentence sent at the wrong time, to the wrong recipient, with an unintended implication.

Competence Requires More Than Turning It On

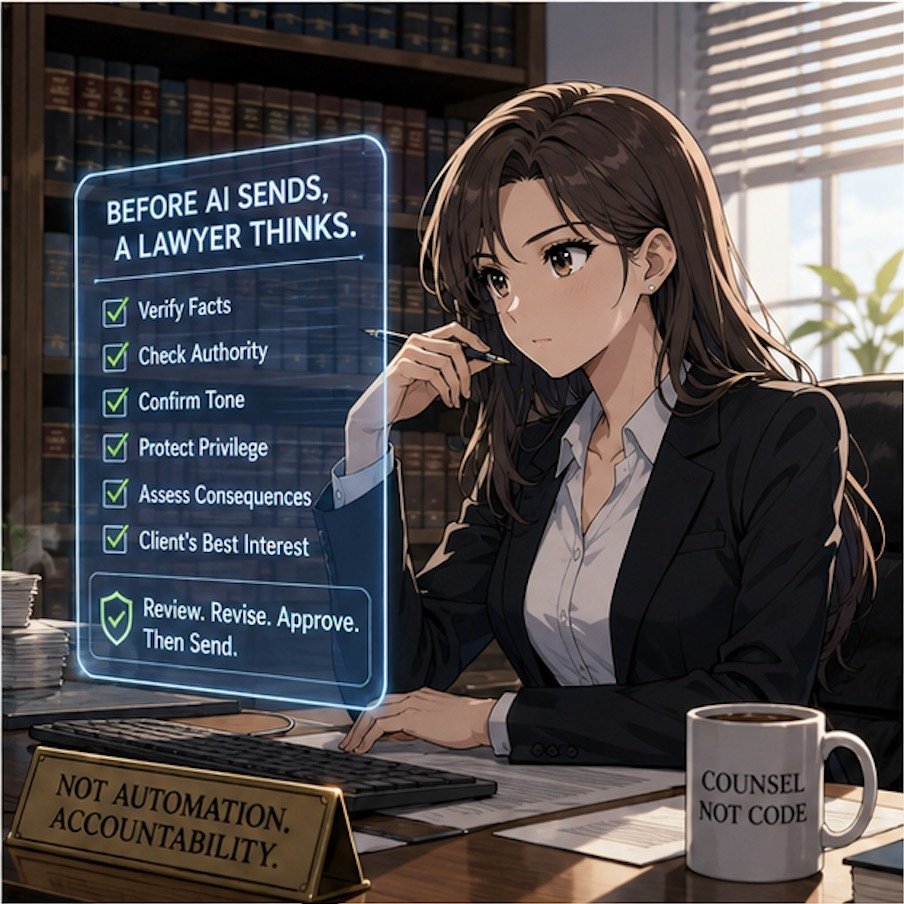
AI Email Assistants Transform Legal Workflows With Human Oversight!

ABA Model Rule 1.1 requires competent representation. Comment 8 specifically directs lawyers to keep abreast of the benefits and risks associated with relevant technology.

That obligation does not mean a lawyer must master the underlying architecture of a large language model. It does mean a lawyer must understand what the tool can access, what it can do, what it may get wrong, and what controls exist before adopting it in a client-facing workflow.

Claude’s Gmail integration illustrates why that inquiry matters. The system can understand labels, dates, contacts, subject lines, themes, and context. It can identify a recent message, carry information through a thread, and compose a reply based on instructions. It can also use connected Google Drive data to prepare a work summary and fold that material into an outgoing email.

Those are real capabilities. They are also real risk surfaces. A connected inbox and Drive account may contain privileged communications, work product, medical records, personnel documents, settlement analyses, client financial information, litigation strategy, and confidential drafts.

Before connecting an AI platform to firm email or cloud storage, lawyers should ask:

  • What email and document data can the system retrieve?

  • What information is retained, logged, or used to improve the service?

  • Does the vendor contractually prohibit training on the firm’s data?

  • Who may access data at the provider, and where is it stored?

  • Can the firm restrict access by user, matter, mailbox, sender, or document type?

  • Can the firm produce an audit trail showing what the AI accessed, drafted, and sent?

  • What happens to the firm’s data when the subscription ends?

Those questions are not technology trivia. They are part of competent vendor assessment.

The “Cheers” Problem Is Not Trivial

Balancing AI Innovation With Human Judgment in Legal Practice

In Nield’s test, Claude composed a generally acceptable message. Yet it signed the email with “cheers,” a phrase the author said he would not ordinarily use. That small mismatch is revealing. Claude had not merely organized information. It had made a communicative choice in someone else’s name.

For a lawyer, voice is not just branding. Tone can convey firmness, concession, uncertainty, urgency, skepticism, hostility, openness to settlement, or a willingness to cooperate. A message that is “a little generic,” as Nield described Claude’s output, may be harmless when discussing weather and a meeting with oneself. It may be harmful in a dispute where each word will be parsed for meaning. ✉️

An email that begins, “We are happy to work with you,” may convey a strategic position that the lawyer did not intend. A reply that omits one key qualification can alter the practical meaning of a settlement discussion. A bot that tries to be helpful may include a fact from a prior thread that should not be repeated, or it may summarize a client’s situation so broadly that it creates a misleading record.

Lawyers should not equate grammatically fluent text with sound legal judgment.

Rules 1.2, 1.4, and 1.6

ABA Model Rule 1.2 requires lawyers to abide by a client’s decisions concerning the objectives of representation and to consult with the client about the means of pursuing those objectives. An AI system cannot determine whether accepting an extension, offering a document, softening a demand, or answering a client’s question advances those objectives.

Rule 1.4 requires appropriate client communication. An AI-generated reply can appear reassuring while omitting necessary advice, misunderstanding the issue, or providing a client with an answer that no lawyer has evaluated. A client should not receive what appears to be legal counsel when it is actually unreviewed probabilistic text.

Rule 1.6 is equally central. Lawyers must not reveal information relating to representation without authorization, subject to limited exceptions. Giving an AI provider access to email and Drive is not automatically unethical, but it requires reasonable diligence and safeguards. The more expansive the permission, the more careful the analysis must be. 🔒

A lawyer who enables automatic sending compounds the issue. Now the system is not only reading protected information; it may also select, summarize, and transmit it externally.

When AI Bots Email Each Other

Nield also raises a concern that lawyers should not dismiss: the prospect of AI systems emailing other AI systems “into infinity.”

That is more than a philosophical concern in legal practice. Imagine two firms each authorizing AI assistants to respond automatically. One system writes, “We can accommodate a brief extension.” The other interprets that as agreement, sends a confirmation, and then proposes a revised deadline. The first system responds with language suggesting continued assent.

Neither lawyer may have reviewed the exchange until a dispute arises. Yet both sides may face a written record that appears to memorialize an agreement.

The proper response is not to ban AI from legal email. It is to preserve human responsibility at the point of external communication.

The Right Workflow

Legal Technology Works Best when lawyers balance Ethics, Trust, and Accountability!

AI can help lawyers manage an overloaded inbox. It can identify urgent messages, group correspondence by matter, summarize long threads, retrieve relevant prior communications, and prepare a first draft. Those uses can reduce administrative burden and create time for legal analysis. ✅

But law firms should adopt a bright-line rule: No AI system may automatically send a substantive external communication without human review and approval.

A practical protocol should require the reviewing lawyer or trained staff member to:

  • Read the full thread and relevant attachments.

  • Confirm the recipient and email address.

  • Verify every factual assertion and deadline.

  • Check for client commitments, concessions, and settlement implications.

  • Remove unnecessary confidential information.

  • Confirm that the message reflects the lawyer’s actual voice, judgment, and strategy.

  • Send the communication only after that review is complete.

Claude’s Gmail feature is impressive. It can make email easier. But as Nield’s own decision to test it only with himself demonstrates, capability is not the same as reliability, and reliability is not the same as professional responsibility.

For lawyers, the governing principle should be simple: let AI prepare the draft; let a responsible human decide whether it should ever leave the outbox. ⚖️

MTC

MTC: AI Governance Crisis - What Every Law Firm Must Learn from 1Password's Eye-Opening Security Research

The legal profession stands at a crossroads. Recent research commissioned by 1Password reveals four critical security challenges that should serve as a wake-up call for every law firm embracing artificial intelligence. With 79% of legal professionals now using AI tools in some capacity while only 10% of law firms have formal AI governance policies, the disconnect between adoption and oversight has created unprecedented vulnerabilities that could compromise client confidentiality and professional liability.

The Invisible AI Problem in Law Firms

The 1Password study's most alarming finding mirrors what law firms are experiencing daily: only 21% of security leaders have full visibility into AI tools used in their organizations. This visibility gap is particularly dangerous for law firms, where attorneys and staff may be uploading sensitive client information to unauthorized AI platforms without proper oversight.

Dave Lewis, Global Advisory CISO at 1Password, captured the essence of this challenge perfectly: "We have closed the door to AI tools and projects, but they keep coming through the window!" This sentiment resonates strongly with legal technology experts who observe attorneys gravitating toward consumer AI tools like ChatGPT for legal research and document drafting, often without understanding the data security implications.

The parallel to law firm experiences is striking. Recent Stanford HAI research revealed that even professional legal AI tools produce concerning hallucination rates—Westlaw AI-Assisted Research showed a 34% error rate, while Lexis+ AI exceeded 17%. (Remember my editorial/bolo MTC/🚨BOLO🚨: Lexis+ AI™️ Falls Short for Legal Research!) These aren't consumer chatbots but professional tools marketed to law firms as reliable research platforms.

Four Critical Lessons for Legal Professionals

First, establish comprehensive visibility protocols. The 1Password research shows that 54% of security leaders admit their AI governance enforcement is weak, with 32% believing up to half of employees continue using unauthorized AI applications. Law firms must implement SaaS governance tools to identify AI usage across their organization and document how employees are actually using AI in their workflows.

Second, recognize that good intentions create dangerous exposures. The study found that 63% of security leaders believe the biggest internal threat is employees unknowingly giving AI access to sensitive data. For law firms handling privileged attorney-client communications, this risk is exponentially greater. Staff may innocently paste confidential case details into AI tools, potentially violating client confidentiality rules and creating malpractice liability.

Third, address the unmanaged AI crisis immediately. More than half of security leaders estimate that 26-50% of their AI tools and agents are unmanaged. In legal practice, this could mean AI agents are interacting with case management systems, client databases, or billing platforms without proper access controls or audit trails—a compliance nightmare waiting to happen.

Fourth, understand that traditional security models are inadequate. The research emphasizes that conventional identity and access management systems weren't designed for AI agents. Law firms must evolve their access governance strategies to include AI tools and create clear guidelines for how these systems should be provisioned, tracked, and audited.

Beyond Compliance: Strategic Imperatives

The American Bar Association's Formal Opinion 512 established clear ethical frameworks for AI use, but compliance requires more than policy documents. Law firms need proactive strategies that enable AI benefits while protecting client interests.

Effective AI governance starts with education. Most legal professionals aren't thinking about AI security risks in these terms. Firms should conduct workshops and tabletop exercises to walk through potential scenarios and develop incident response protocols before problems arise.

The path forward doesn't require abandoning AI innovation. Instead, it demands extending trust-based security frameworks to cover both human and machine identities. Law firms must implement guardrails that protect confidential information without slowing productivity—user-friendly systems that attorneys will actually follow.

Final Thoughts: The Competitive Advantage of Responsible AI Adoption

Firms that proactively address these challenges will gain significant competitive advantages. Clients increasingly expect their legal counsel to use technology responsibly while maintaining the highest security standards. Demonstrating comprehensive AI governance builds trust and differentiates firms in a crowded marketplace.

The research makes clear that security leaders are aware of AI risks but under-equipped to address them. For law firms, this awareness gap represents both a challenge and an opportunity. Practices that invest in proper AI governance now will be positioned to leverage these powerful tools confidently while their competitors struggle with ad hoc approaches.

The legal profession's relationship with AI has fundamentally shifted from experimental adoption to enterprise-wide transformation. The 1Password research provides a roadmap for navigating this transition securely. Law firms that heed these lessons will thrive in the AI-augmented future of legal practice.

MTC

MTC: Why Courts Hesitate to Adopt AI - A Crisis of Trust in Legal Technology

Despite facing severe staffing shortages and mounting operational pressures, America's courts remain cautious about embracing artificial intelligence technologies that could provide significant relief. While 68% of state courts report staff shortages and 48% of court professionals lack sufficient time to complete their work, only 17% currently use generative AI tools. This cautious approach reflects deeper concerns about AI reliability, particularly in light of recent (and albeit unnecessarily continuing) high-profile errors by attorneys using AI-generated content in court documents.

The Growing Evidence of AI Failures in Legal Practice

Recent cases demonstrate why courts' hesitation may be justified. In Colorado, two attorneys representing MyPillow CEO Mike Lindell were fined $3,000 each after submitting a court filing containing nearly 30 AI-generated errors, including citations to nonexistent cases and misquoted legal authorities. The attorneys admitted to using artificial intelligence without properly verifying the output, violating Federal Rule of Civil Procedure 11.

Similarly, a federal judge in California sanctioned attorneys from Ellis George LLP and K&L Gates LLP $31,000 after they submitted briefs containing fabricated citations generated by AI tools including CoCounsel, Westlaw Precision, and Google Gemini. The attorneys had used AI to create an outline that was shared with colleagues who incorporated the fabricated authorities into their final brief without verification.

These incidents are part of a broader pattern of AI hallucinations in legal documents. The June 16, 2025, Order to Show Cause from the Oregon federal court case Sullivan v. Wisnovsky, No. 1:21-cv-00157-CL, D. Or. (June 16, 2025) demonstrates another instance where plaintiffs cited "fifteen non-existent cases and misrepresented quotations from seven real cases" after relying on what they claimed was "an automated legal citation tool". The court found this explanation insufficient to avoid sanctions.

The Operational Dilemma Facing Courts

LAWYERS NEED TO BalancE Legal Tradition with Ethical AI Innovation

The irony is stark: courts desperately need technological solutions to address their operational challenges, yet recent AI failures have reinforced their cautious approach. Court professionals predict that generative AI could save them an average of three hours per week initially, growing to nearly nine hours within five years. These time savings could be transformative for courts struggling with increased caseloads and staff shortages.

However, the profession's experience with AI-generated hallucinations has created significant trust issues. Currently, 70% of courts prohibit employees from using AI-based tools for court business, and 75% have not provided any AI training to their staff. This reluctance stems from legitimate concerns about accuracy, bias, and the potential for AI to undermine the integrity of judicial proceedings.

The Technology Adoption Paradox

Courts have successfully adopted other technologies, with 86% implementing case management systems, 85% using e-filing, and 88% conducting virtual hearings. This suggests that courts are not inherently resistant to technology. But they are specifically cautious about AI due to its propensity for generating false information.

The legal profession's relationship with AI reflects broader challenges in implementing emerging technologies. While 55% of court professionals recognize AI as having transformational potential over the next five years, the gap between recognition and adoption remains significant. This disconnect highlights the need for more reliable AI systems and better training for legal professionals.

The Path Forward: Measured Implementation

The solution is not to abandon AI but to implement it more carefully. Legal professionals must develop better verification protocols. As one expert noted, "AI verification isn't optional—it's a professional obligation." This means implementing systematic citation checking, mandatory human review, and clear documentation of AI use in legal documents. Lawyers must stay up to date on the technology available to them, as required by the American Bar Association Model Rule of Professional Conduct 1.1[8], including the expectation that they use the best available technology currently accessible. Thus, courts too need comprehensive governance frameworks that address data handling, disclosure requirements, and decision-making oversight before evaluating AI tools. The American Bar Association's Formal Opinion 512 on Generative Artificial Intelligence Tools provides essential guidance, emphasizing that lawyers must fully consider their ethical obligations when using AI.

Final Thoughts

THE Future of Law: AI and Justice in Harmony!

Despite the risks, courts and legal professionals cannot afford to ignore AI indefinitely. The technology's potential to address staffing shortages, reduce administrative burdens, and improve access to justice makes it essential for the future of the legal system. However, successful implementation requires acknowledging AI's limitations while developing robust safeguards to prevent the types of errors that have already damaged trust in the technology.

The current hesitation reflects a profession learning to balance innovation with reliability. As AI systems improve and legal professionals develop better practices for using them, courts will likely become more willing to embrace these tools. Until then, the cautious approach may be prudent, even if it means forgoing potential efficiency gains.

The legal profession's experience with AI serves as a reminder that technological adoption in critical systems requires more than just recognizing potential benefits—it demands building the infrastructure, training, and governance necessary to use these powerful tools responsibly.

MTC