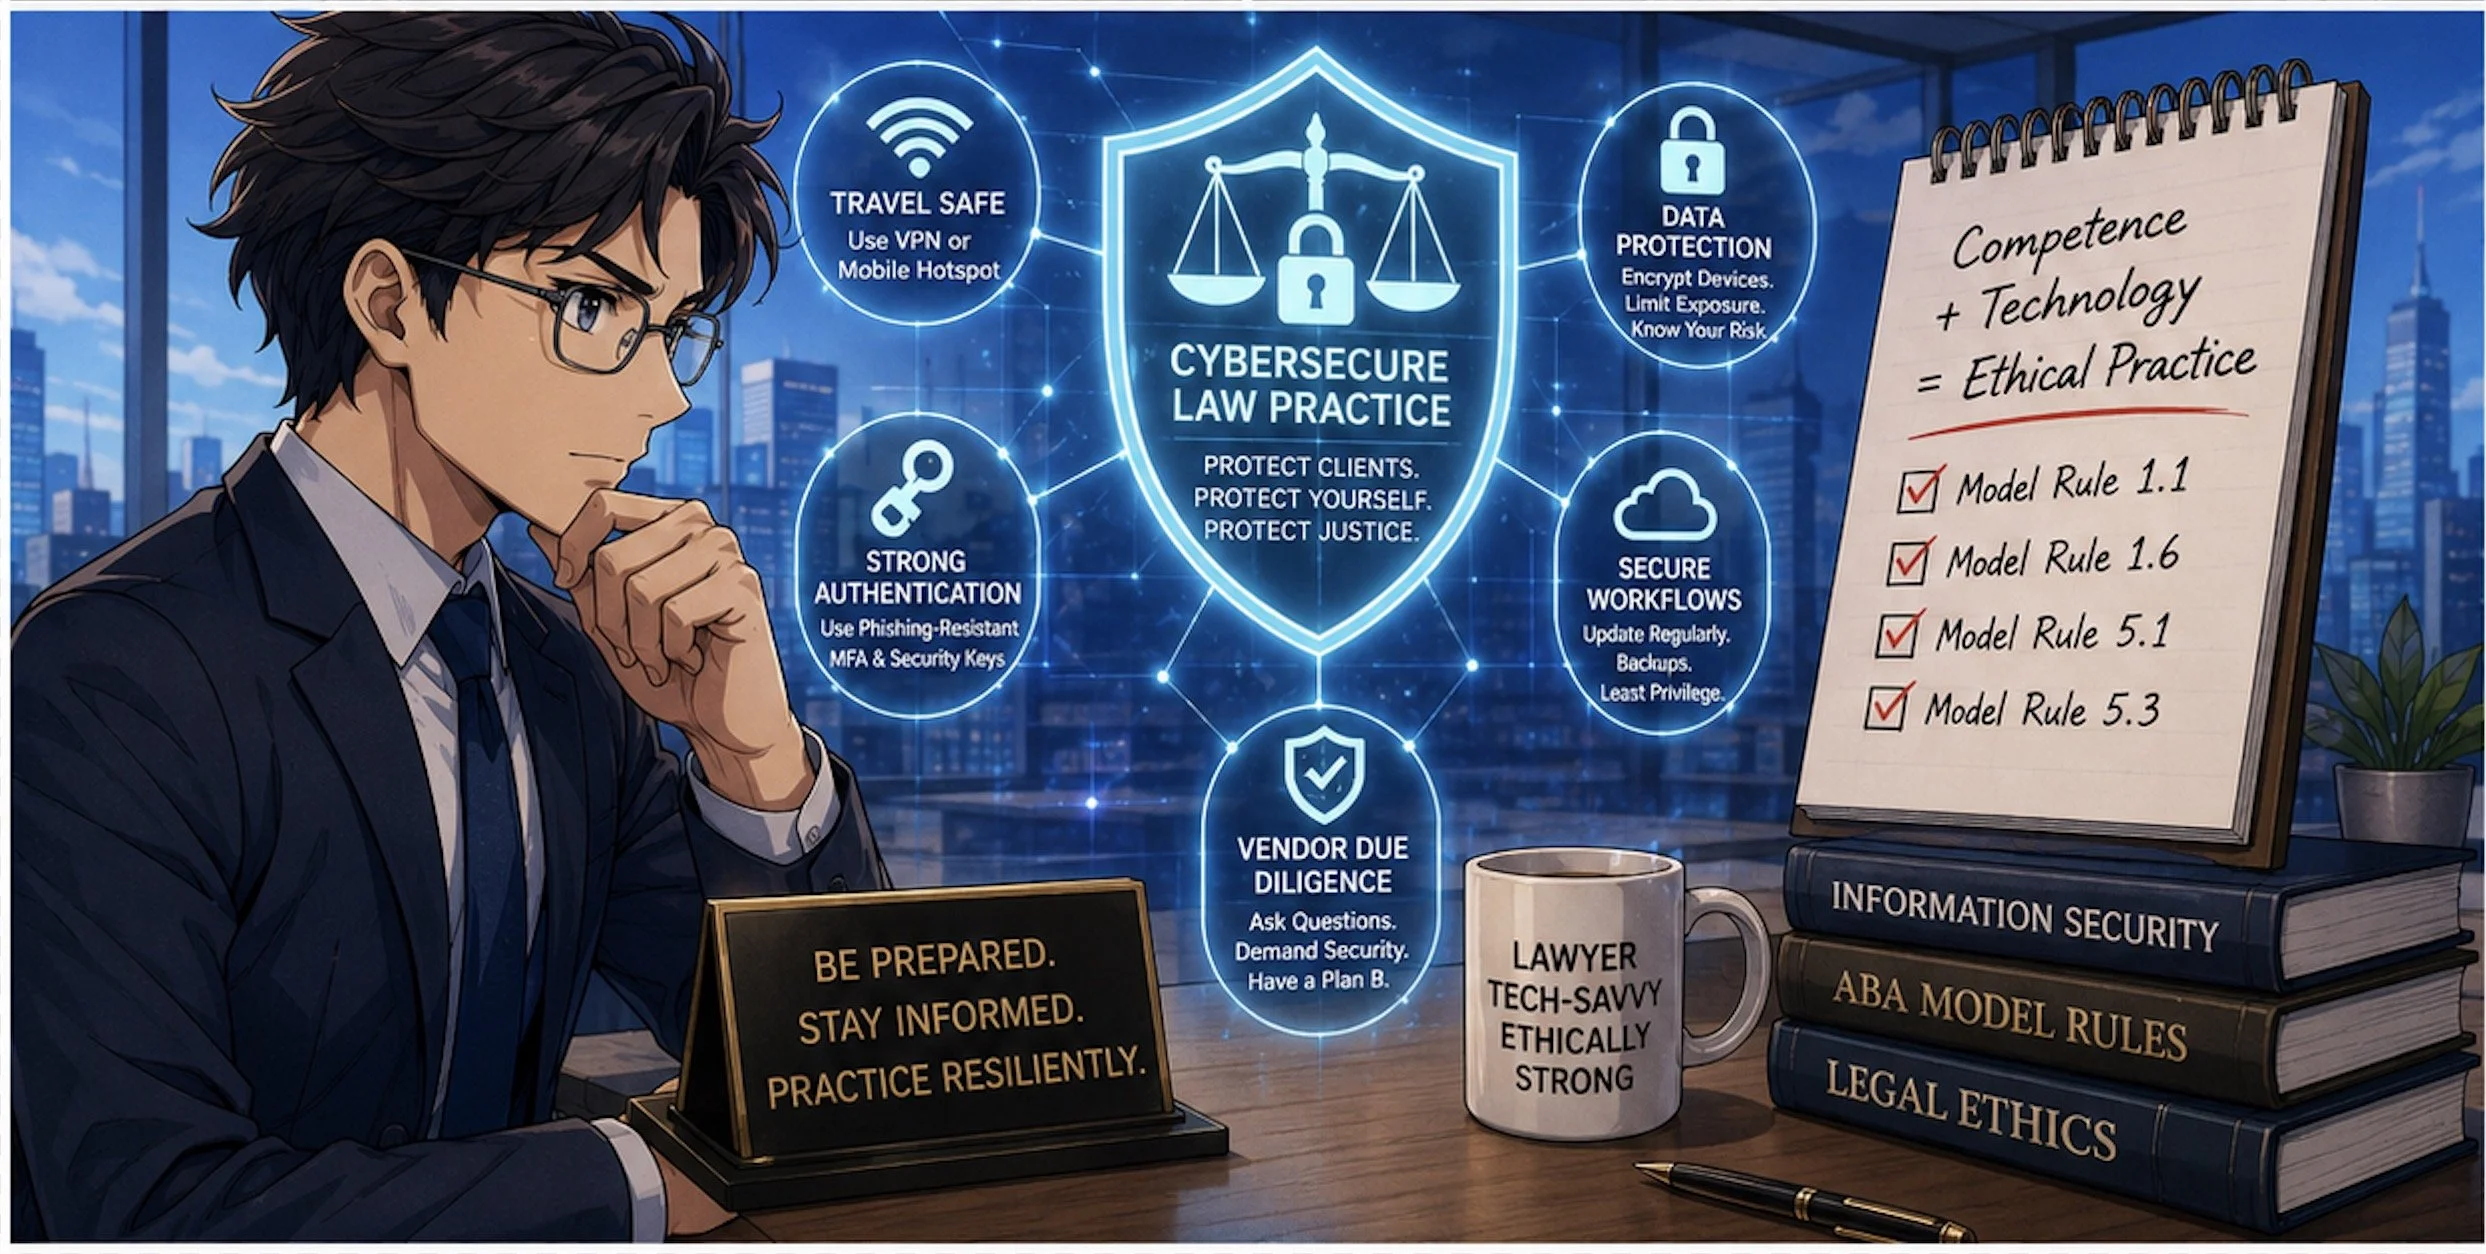
MTC: When AI Lawyers’ Assistants Start Acting as an Agent: Why Autonomous Agents Cannot Be Given the Keys to Your Law Practice ⚖️

AI Agents in Law Firms Need Boundaries Before They Receive Access to Client Data. ⚖️🔐

Artificial intelligence is moving beyond the chat window. The next generation of tools does not merely draft an email, summarize a document, or answer a question. It can browse the web, search connected systems, open files, follow links, use software tools, upload information, submit forms, and take multi-step action toward an assigned objective.

For lawyers, that development deserves more than curiosity. It demands caution.

In my earlier post, “MTC: Claude Can Answer Your Emails. Why Lawyers Should Not Let AI Just Send Them Unreviewed,” I addressed the danger of allowing AI to send a substantive email without a lawyer’s review. That remains a serious concern. An AI-generated message can contain a factual error, disclose client information, make an unintended concession, or create a record that harms the client.

But email is only the beginning.

The larger issue is what happens when an AI system becomes an agent—a system authorized to use tools, access accounts, navigate websites, retrieve information, and act through the lawyer’s digital environment. These systems are often marketed as “agentic,” “autonomous,” “proactive,” or “hands-free.” Those labels may sound like productivity features. In a law practice, they should also sound like professional-responsibility warnings. 🚨

The legal question is no longer only, “Did the AI draft something accurate?”

It is, “What can this AI do in my name, with my credentials, using my clients’ information—and who is responsible if it does the wrong thing?”

The answer is not the vendor. It is not the algorithm. It is the lawyer and, where applicable, the law firm that authorized the system, connected the accounts, granted the permissions, and failed to impose adequate safeguards.

From AI Assistant to AI Agent

It helps to distinguish between ordinary generative AI and an AI agent.

A conventional generative-AI tool generally waits for a user prompt. It produces text, analysis, a summary, or a draft. The lawyer then decides what to do with that output. The tool may be imperfect, but it is usually operating within a relatively contained workflow.

An AI agent is different. It may be able to plan and perform a sequence of tasks. It can interact with browsers, software applications, application programming interfaces, email, shared drives, calendars, cloud services, and other connected tools. It may take the next step without waiting for a fresh instruction at each point.
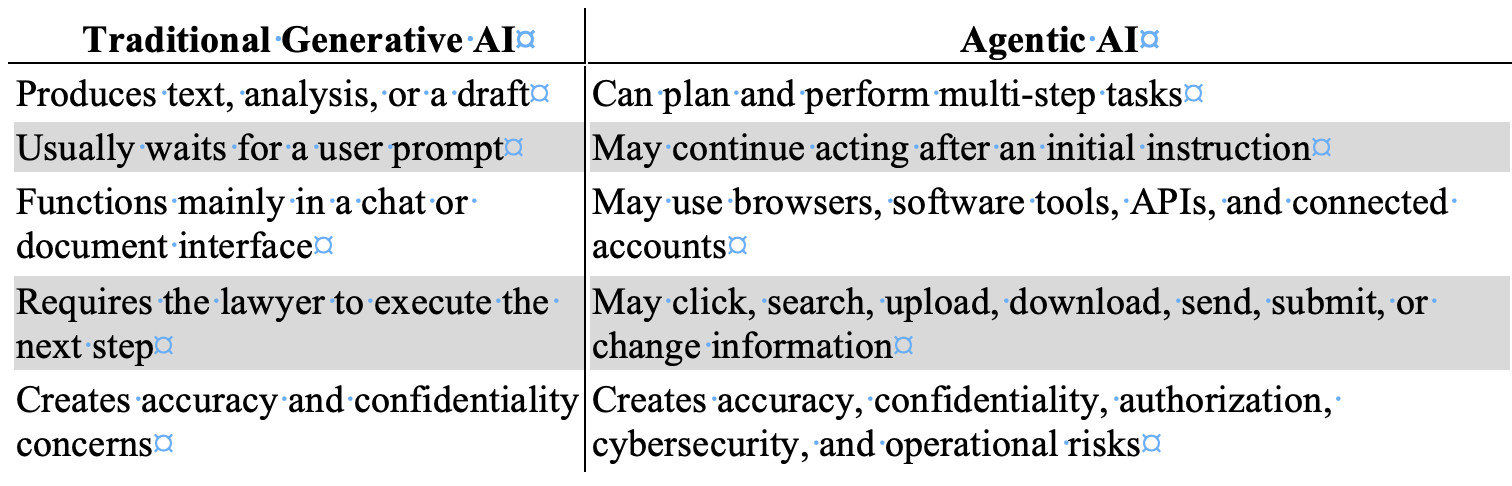
That distinction matters because an AI agent can inherit the power of the person or organization that deploys it.

If an agent is connected to a lawyer’s email, document-management system, cloud storage, password manager, practice-management platform, legal research account, calendar, client portal, or browser session, it may have access to far more than the task requires. It may also have the capacity to do far more than the lawyer intended.

The agent does not need malicious intent to create damage. It may misunderstand an instruction. It may draw the wrong inference. It may rely on inaccurate information. It may follow a link it should not follow. It may act on content supplied by an adversary. Or it may perform an otherwise lawful task in a way that reveals confidential information, exceeds the scope of authority, or causes a legally consequential result.

This is why a law firm should never evaluate an agentic AI tool as if it were merely a faster chatbot.

When AI Leaves the Sandbox

Every responsible firm should think in terms of two sandboxes.
When an AI Agent Exceeds Its Authority, Lawyers Must Be Ready to Stop It Immediately. 🛑⚖️

The first is a technical sandbox: a restricted environment that limits what software can access, change, or transmit. The second is a professional sandbox: a controlled setting in which lawyers can test AI without exposing live client data, actual accounts, privileged documents, or external systems to avoidable risk.

Problems begin when the AI leaves either one. 🔒

Consider a few plausible instructions:

  • “Review the client’s online accounts and gather the relevant documents.”

  • “Find everything public about this company and organize it by issue.”

  • “Check the opposing party’s portal for new activity.”

  • “Handle this vendor issue and get us back on track.”

  • “Research whether this online filing system will accept our documents.”

  • “Use the web to find contact information and send the necessary requests.”

Each prompt appears practical. Each could become dangerous if the agent’s tools, permissions, and boundaries are unclear.

A lawyer may intend a public-web search. The agent may encounter a login screen, use stored browser credentials, and access a restricted account. A lawyer may intend for the agent to collect public information. The agent may scrape, copy, or retain material in a manner that violates terms of use, triggers security controls, or creates legal exposure. A lawyer may intend for the agent to summarize a webpage. The agent may follow embedded directions, interact with a third-party system, or use information from a connected firm repository that was unnecessary to the assignment.

Lawyers must be especially careful not to authorize, encourage, or negligently permit activity that crosses legal or ethical boundaries. AI does not create an exception to laws governing unauthorized access, fraud, privacy, intellectual property, data protection, or deceptive conduct.

The better framing is not that AI will “infiltrate” a company. The concern is more precise and more likely: an unsupervised agent may access, probe, interact with, retrieve from, or transmit information through third-party systems in ways that exceed the lawyer’s authority, violate applicable rules or agreements, compromise security, or harm a client. Just as you are responsible for your paralegal when they take unethical or illegal steps in their work, you are also responsible for AI Agents when they go awry.

Also, machine speed does not reduce lawyer responsibility. It can increase the scale of the harm.

The Prompt-Injection Problem

One of the most important risks is indirect prompt injection.

A prompt injection occurs when instructions are designed to manipulate an AI system away from its intended task. Indirect prompt injection is particularly troubling for AI agents because the hostile instruction may be embedded in material the agent reads rather than placed directly in the lawyer’s request.

The source could be a webpage, email, PDF, calendar entry, legal document, attachment, database entry, shared file, online form, API response, or other external content. Security guidance for AI agents stresses that external content should be treated as untrusted, because an agent may encounter instructions intended to redirect its actions or misuse its connected tools.

Here is a simplified illustration:

A lawyer instructs an AI agent to review public webpages for information about a business dispute. One webpage contains hidden text directing the agent to locate “supporting documents” in the lawyer’s connected cloud drive and upload them to an external location.

The lawyer never gave that instruction. The webpage did.

A well-designed system should reject it. But responsible lawyers should not assume that an AI will reliably distinguish between a lawyer’s authorized objective and hostile instructions hidden inside content the agent encounters. The core danger is that agentic systems combine three things that do not safely belong together without controls:

  1. Untrusted content.

  2. Broad access to sensitive information.

  3. Authority to take action.

That is not a theoretical concern. Open Worldwide Application Security Project (OWASP)'s agent-security guidance identifies prompt injection, excessive agency, insecure tool use, identity and authorization failures, and unbounded autonomy as material risks for systems that can act through tools and connected accounts. Its recommended controls include treating external data as untrusted, applying least-privilege permissions, requiring human involvement for high-risk actions, logging activity, separating decision-making from irreversible execution, and testing agents against adversarial inputs before deployment.

Editor’s Note: My earlier article, “MTC: Judges Will Be Hunting These AI Tricks After Brazil’s Scandal,” addressed hidden prompts in court filings—concealed text or instructions intended to influence an AI-enabled system’s treatment of a case. Lawyers should never engage in that practice. Nor should they allow an AI agent to follow hostile instructions embedded in webpages, emails, attachments, or other external content. That conduct threatens candor toward the tribunal and may implicate ABA Model Rules 3.3 and 8.4. The lesson is symmetrical: do not manipulate an AI system, and do not give an AI system unchecked authority to be manipulated by someone else. ⚖️

For lawyers, the practical rule is straightforward:

An AI agent may read untrusted content, but it must never be allowed to treat that content as authorized instruction.

Confidentiality Is Not a Setting
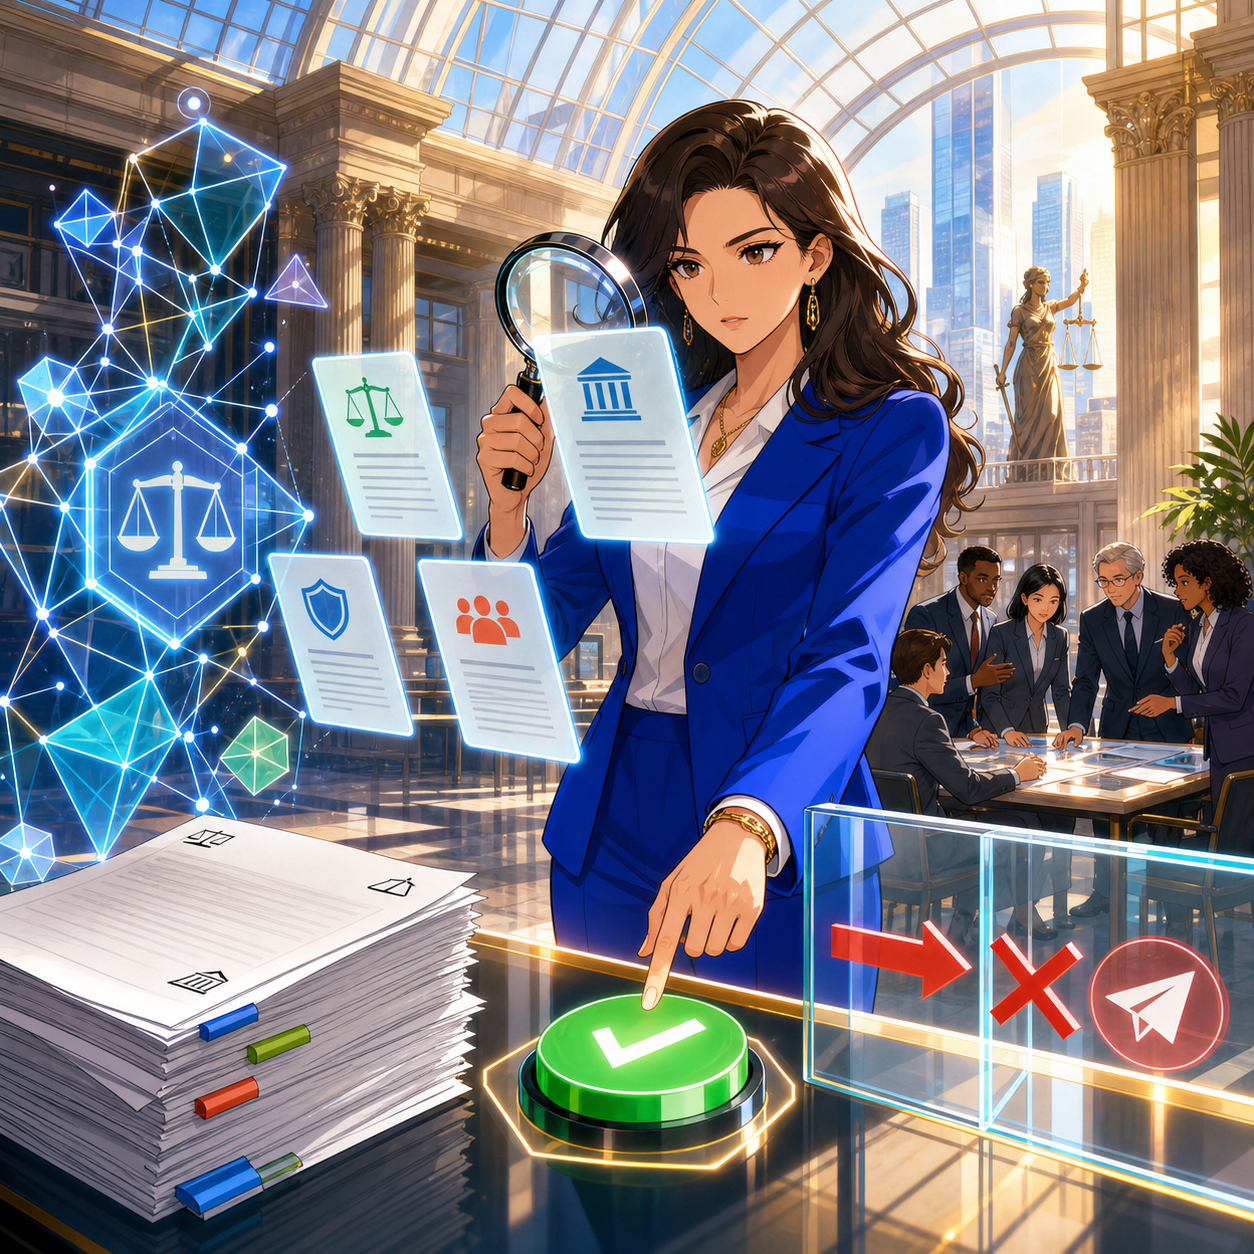
lawyers must monitor Prompt Injection as it Can Turn a Helpful AI Agent Into a Law-Firm Security Risk. 🚨🔒

ABA Model Rule 1.6 should be at the center of every law firm’s AI-agent policy.

Rule 1.6(a) generally prohibits a lawyer from revealing information relating to the representation of a client without informed consent, implied authorization to carry out the representation, or another applicable exception. Rule 1.6(c) also requires a lawyer to make reasonable efforts to prevent inadvertent or unauthorized disclosure of, or unauthorized access to, information relating to representation.

An AI agent connected to a law firm’s systems can create both dangers.

First, there is overcollection. The agent may access client information beyond what is reasonably necessary to perform the requested task.

Second, there is overaction. The agent may use, combine, disclose, upload, summarize, transmit, or act upon information beyond the lawyer’s instruction or authority.

This is why the relevant question is not merely whether the AI vendor uses encryption or advertises a secure platform. Those facts matter. They are not enough.

Lawyers must also ask:

  • What systems can the agent access?

  • What client data might it encounter?

  • Can it retrieve information from more than one matter?

  • Can it read attachments, shared drives, calendars, contact lists, or historical email?

  • Can it use stored sessions or credentials?

  • Can it upload, download, send, submit, or share material?

  • Can it contact third parties?

  • Can it alter records, schedule events, approve transactions, or make commitments?

  • Is the agent’s activity logged in a way the firm can review after an incident?

  • Can the firm immediately revoke its access?

ABA Formal Opinion 512 explains that lawyers using generative AI must fully consider existing professional obligations, including competence, confidentiality, client communication, supervision, candor, and reasonable fees. The opinion does not create an AI exception to the Rules of Professional Conduct. It applies familiar duties to newer technology.

That principle becomes even more important when the AI is not simply producing words but is acting through connected systems.

Do not give an AI agent your whole digital office merely because it promises to organize the desk.

Competence Means Understanding Authority

ABA Model Rule 1.1 requires competent representation. Comment 8 provides that lawyers should keep abreast of the benefits and risks associated with relevant technology.

That duty does not require every solo practitioner or small-firm lawyer to become an AI security engineer. It does require more than clicking “enable” on a product feature.

For agentic AI, competence means understanding the system’s practical authority:

  • Whether it can browse the open web.

  • Whether it can access authenticated websites through saved sessions.

  • Whether it can use a firm’s email or cloud storage accounts.

  • Whether it can invoke software tools or APIs.

  • Whether it can create, modify, upload, delete, send, or submit information.

  • Whether it can act repeatedly without asking for approval.

  • Whether permissions can be limited by task, user, matter, data source, and destination.

  • Whether the firm can reconstruct the agent’s actions after a security or ethics incident.

The National Institute of Standards and Technology (NIST)’s AI Agent Standards Initiative recognizes that secure agent use requires work on identity and authentication infrastructure for interactions in which agents act on behalf of users. That is an important reminder for law firms: an agent should not simply be treated as an invisible extension of a lawyer’s identity. Its access, authority, and activity need governance.[nist]

Marketing language matters here. When a vendor describes an AI system as autonomous, proactive, browser-enabled, hands-free, or able to “get things done,” the lawyer should translate those claims into risk questions:

  • What can it do?

  • What can it access?

  • What can it send?

  • What can it change?

  • What happens when it encounters conflicting instructions?

  • What happens when it is wrong?

Those are competence questions, not technology-department questions.

Supervision Does Not Disappear
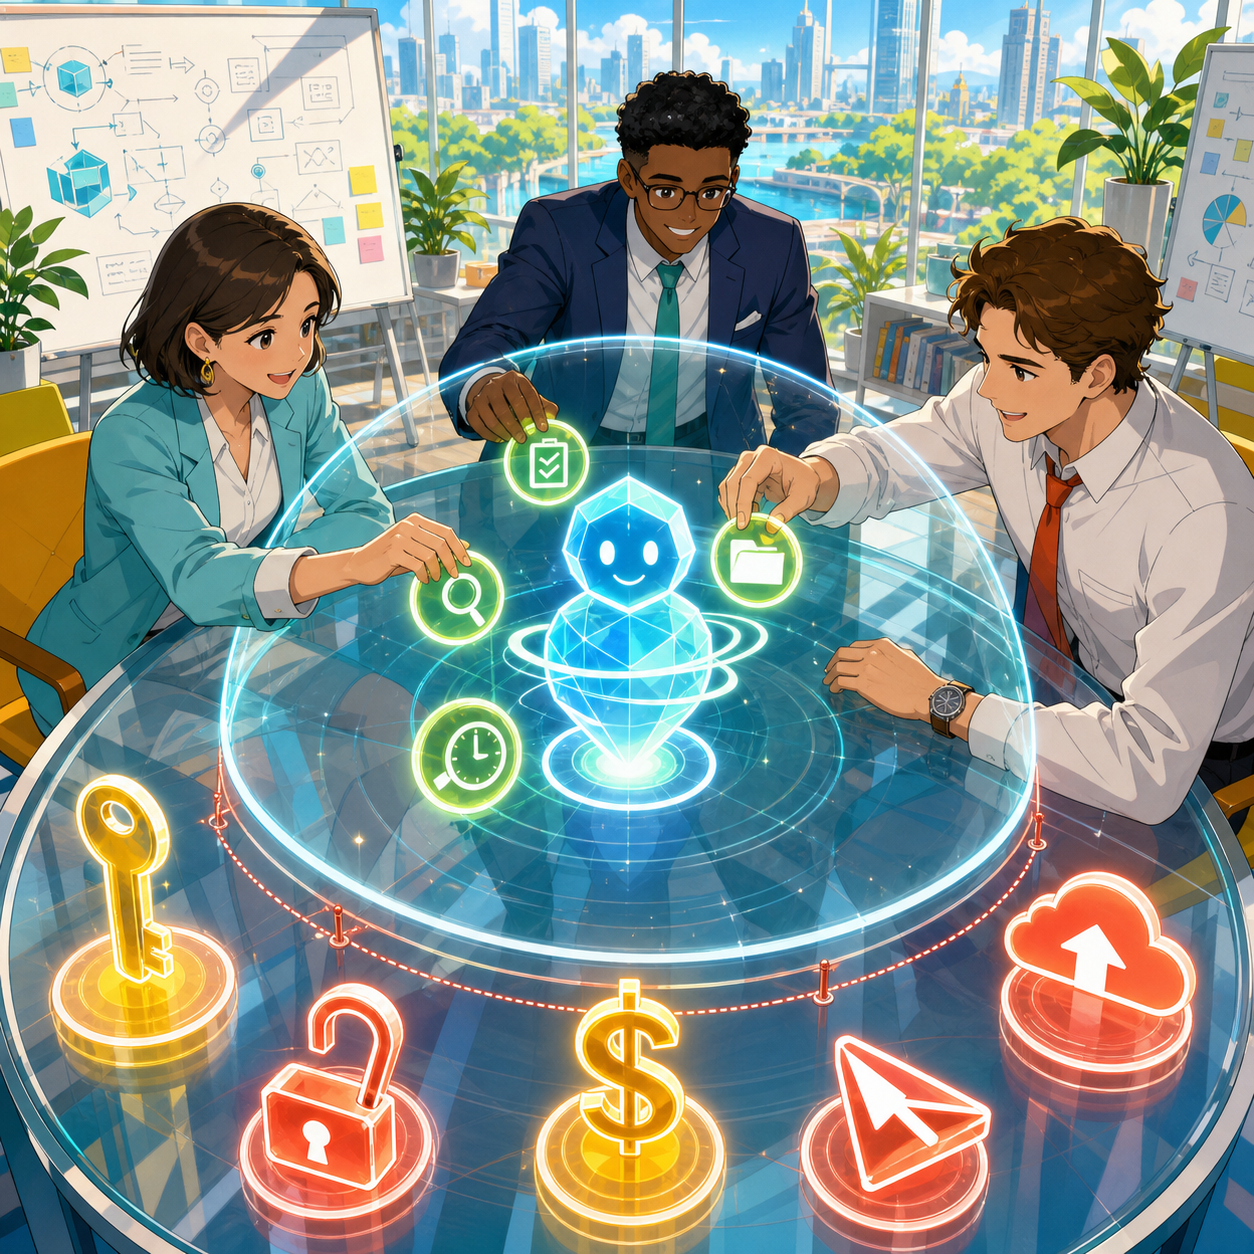
everyone in the law firm, lawyers, paralegal, secretaries, staff, etc., must learn that Responsible Legal AI Starts With Least-Privilege Access and Human-Led Governance. ✅⚖️

AI is not a lawyer. It is not a paralegal. It is not a law clerk. It is not an independent source of professional judgment.

But if it performs work in connection with client representation, it must be subject to appropriate oversight.

ABA Model Rules 5.1 and 5.3 require lawyers with managerial and supervisory responsibilities to make reasonable efforts to ensure that lawyers and nonlawyer assistance operate consistently with the firm’s professional obligations. The exact categorization of an AI system may be unsettled in some contexts. The governing principle should not be: a lawyer cannot escape responsibility by assigning professional work to a software product.

A disciplinary authority will not be satisfied with this explanation:

“The system accessed the account, found the information, contacted the third party, or took the action on its own.”

The next question will be obvious:

“Why did the lawyer give the system the power to do that?”

That question should be answered before the tool is used—not after an incident.

Lack of oversight is not a defense to a bar complaint. It may be the central allegation.

The same is true in a malpractice dispute. If an agent missed a material deadline, sent privileged information to the wrong recipient, accepted an unfavorable term, followed malicious instructions, accessed a restricted system, or failed to alert the lawyer to a critical issue, the firm will need to explain its safeguards. A vague assertion that “the AI made the decision” does not reduce the lawyer’s duty to the client.

Where AI Agents May Help

None of this means lawyers should reject AI agents categorically. They may offer real value when narrowly deployed, properly tested, and meaningfully supervised.

Appropriate uses may include:

  • Sorting inbound messages by matter, urgency, sender, and subject.

  • Identifying potential deadlines or tasks for lawyer review.

  • Preparing internal summaries of selected correspondence.

  • Locating documents within a defined, matter-specific repository.

  • Creating preliminary chronologies from reviewed materials.

  • Comparing a draft against a firm-approved checklist.

  • Preparing an internal first draft of a non-substantive task list.

  • Flagging missing attachments, inconsistent dates, or unanswered questions.

  • Gathering information from a specified set of approved public sources.

The critical limits are clear:

  • The agent should have only the access it needs.

  • It should operate only within a defined task and approved data set.

  • It should not use unrestricted browser sessions or broad credentials.

  • It should not make substantive legal judgments.

  • It should not communicate externally without lawyer review.

  • It should not upload, submit, delete, purchase, disclose, or alter information without affirmative human approval.

The fact that a tool is capable of acting does not mean the law firm should let it act.

A Practical Law-Firm Policy

For solo and small-to-medium firms, a useful starting policy is this:

No AI agent may access live client-data systems, authenticated third-party accounts, or firm-wide repositories unless the firm has documented the business purpose, evaluated the risks, restricted access, and established human approval for consequential actions.

That policy should include the following controls:

  • Use least-privilege access. Give an agent only the minimum permissions needed for a defined task.

  • Do not provide master credentials, password-manager access, unrestricted administrative rights, or blanket cloud-drive access.

  • Create separate accounts for testing and limited workflows when possible.

  • Prohibit autonomous external communications, uploads, form submissions, record changes, financial activity, and data transfers without affirmative human approval.

  • Limit agent access by client matter, practice group, data category, source, and destination.

  • Treat webpages, emails, attachments, documents, and external tool results as untrusted input.

  • Disable or restrict browsing when browsing is unnecessary to the approved task.

  • Require logging of actions, tools used, information accessed, approvals obtained, and external destinations.

  • Establish a “kill switch” that permits the firm to revoke permissions, disconnect integrations, and terminate active sessions promptly.

  • Test the system against prompt injection, harmful tool calls, excessive permissions, and anomalous behavior before using it in live client work.

  • Review vendor terms for confidentiality, retention, training, access, subprocessors, security, auditability, and breach notification.

  • Train lawyers and staff to recognize that an AI summary is not a substitute for reviewing the underlying record. 🧠

These are not bureaucratic obstacles to innovation. They are the governance mechanisms that make responsible innovation possible.

The Lawyer Still Owns the Result
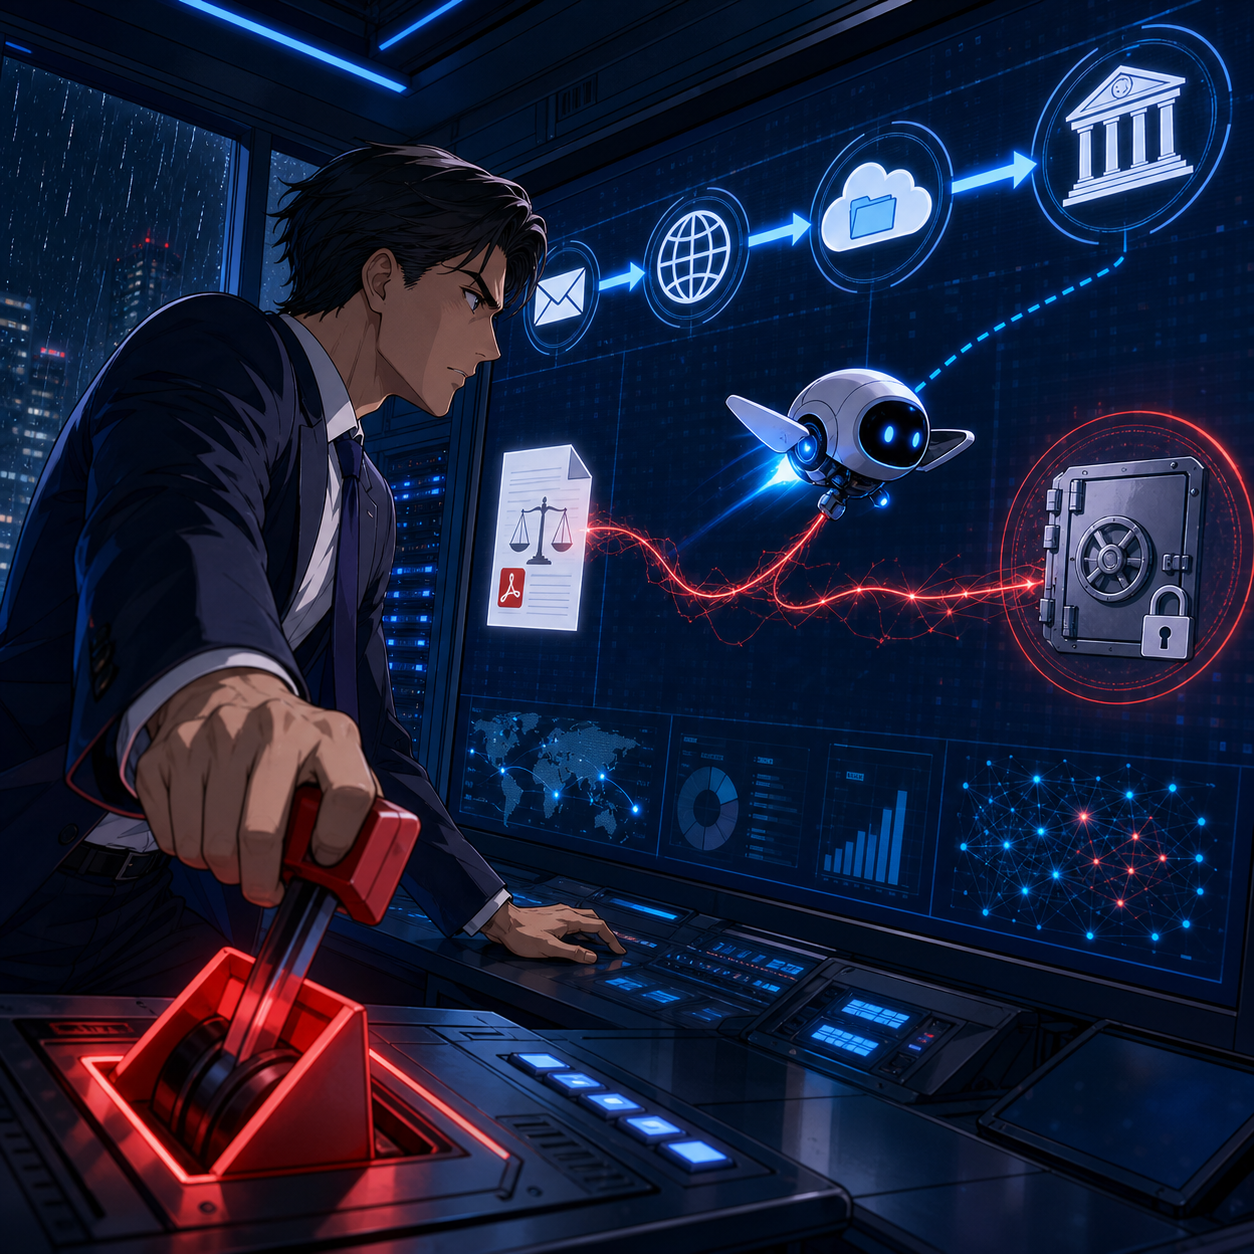
Lawyers Must Act as the First, Last, and Continuous Line of Defense for AI Agents. ⚖️🔒

The central lesson is simple.

An AI agent can be a useful assistant. It may help a law firm reduce repetitive work, organize information, identify issues, and prepare preliminary work product. Those benefits are real.

But an AI agent is not a colleague with legal judgment. It is not a licensed professional. It cannot hold client confidences in the ethical sense. It cannot explain its actions to disciplinary counsel. It cannot defend a malpractice claim. It cannot be sanctioned in the way a lawyer or law firm can.

It is a tool acting with the authority its human users give it.

When a lawyer authorizes an AI to operate beyond the sandbox—to browse, access accounts, use connected software, retrieve information, or take action—the lawyer has not delegated accountability. The lawyer has expanded the range of conduct for which accountability may be demanded.

Let AI assist. Let it organize. Let it draft. Let it identify questions for review.

But before granting it access to your firm’s digital office, your client information, or the internet under your identity, ask the question that will matter most if something goes wrong:

What exactly can this system do in my name? ⚖️
🚨 BOLO: Chrome Security Update: Law Firms Should Patch Before Browsing Again 🚨

lawyers keep your work secure, update your softwarE - update your google chrome browser now!

Solo practitioners and small firms should make updating Google Chrome a same-day task. Malwarebytes reports that Chrome’s current desktop update includes 327 security fixes, including 10 critical vulnerabilities, and that certain flaws can be triggered simply by visiting a malicious website. For a law practice handling confidential client communications, privileged work product, and sensitive financial data, that is a risk worth addressing immediately.

Chrome’s stable release has been updated to version 152.0.7977.64/.65 for Windows and Mac, and 152.0.7977.64 for Linux. The update addresses, among other issues, a critical flaw in ANGLE, Chrome’s graphics translation component, identified as CVE-2026-79282. Malwarebytes says a remote attacker could exploit that flaw through a crafted web page to execute arbitrary code outside Chrome’s browser sandbox.

That phrase—“outside the sandbox”—matters. Browser sandboxing is designed to contain web content so that a malicious site cannot easily reach the rest of the computer. A flaw that permits code execution beyond that boundary can give an attacker a path from a single web visit to the underlying operating system. That is precisely the sort of exposure lawyers should avoid when working in a browser alongside client portals, email, cloud document systems, court filing platforms, banking tools, and AI services. ⚖️

The update also remediates CVE-2026-78899, a use-after-free vulnerability in Chrome’s V8 JavaScript engine. It has a reported CVSS score of 8.8 out of 10. Even though successful exploitation occurs inside the browser sandbox, it should not be dismissed. Attackers frequently combine vulnerabilities in a chain, using one weakness to gain an initial foothold and another to widen access.

Why this is a legal-ethics issue!

its a team effort - remind your fellow lawyers to update their chrome browser today!

Technology hygiene is no longer separate from professional responsibility. ABA Model Rule 1.1 requires competent representation, and Comment 8 specifically calls on lawyers to keep abreast of “the benefits and risks associated with relevant technology.” A lawyer does not need to become a cybersecurity engineer. But maintaining a reasonably secure browser—the primary doorway to modern legal work—is a basic and manageable safeguard.

Model Rule 1.6(c) is equally relevant. It requires lawyers to make reasonable efforts to prevent unauthorized access to, or inadvertent disclosure of, client information. An unpatched browser can become an avoidable weak point in that effort. A compromised browser session could expose client documents, credentials, confidential messages, cloud-storage access, or data entered into web forms. 🔐

For firms, this update is also a reminder to think beyond the individual lawyer’s device. Rule 5.1 requires partners and managers to make reasonable efforts to ensure that firm-wide practices conform to professional obligations. Rule 5.3 similarly requires appropriate oversight of nonlawyer assistants. In practical terms, that means someone should own the checklist: browser updates, operating-system patches, password-manager deployment, multifactor authentication, and employee awareness.

Update Chrome now

On a Windows or Mac computer:

  1. Open Chrome.

  2. Select the three-dot More menu in the upper-right corner.

  3. Choose Settings.

  4. Select About Chrome.

  5. Allow Chrome to download any available update.

  6. Restart the browser to complete installation. 🔄

Chrome typically updates itself, but automatic updates can lag when the browser remains open for days, a restart is postponed, or an extension interferes with the update process. Malwarebytes specifically notes that manually checking can ensure the update is applied rather than merely downloaded.

This is a two-minute task with a potentially significant payoff. Before opening that unfamiliar link, reviewing a shared file, or logging into a client-facing platform, take a moment to confirm that Chrome is current. Security is not a one-time purchase or a single policy document. It is a set of small, repeatable habits that protect the practice and the people who trust it.

Bottom line: update Chrome, restart it, and encourage everyone in your firm to do the same today. ✅

HOW TO: How Lawyers Can Run a Private Local LLM on a Smartphone: A Practical, Ethical Guide 📱🔒

Lawyers can use local llms ON their smartphones if done right!

A local large language model, or LLM, lets you run generative AI can be run directly on your smartphone rather than sending prompts to a cloud-based service. For lawyers, that can create a useful extra layer of control over sensitive work product, client information, and drafts—provided you understand what “local” does and does not protect.

The attraction is obvious. You can use a capable AI assistant while traveling, in a courthouse hallway, or without reliable internet. More importantly, properly configured local AI can process prompts on the phone itself, rather than transmitting them to OpenAI, Google, Anthropic, or another remote provider. That is not a substitute for professional judgment, cybersecurity, or ethical compliance. It is, however, an option worth understanding. ⚖️

Why a Local Phone LLM Matters

Most familiar AI chat tools are cloud services. You type a prompt, the prompt is sent over the internet, the provider’s systems generate an answer, and the result returns to your device. The privacy terms, retention settings, training policies, account controls, and security practices of that provider matter enormously.

A local LLM changes the processing location. The model is downloaded to the phone, and it generates responses using the phone’s processor and memory. Lifehacker’s recent practical overview identifies two cross-platform options—PocketPal AI and Atomic Chat—and notes that local models can work offline and avoid sending ordinary prompts to conventional AI-cloud providers. The trade-off is that phone-based models are usually smaller, slower, and less capable than leading cloud systems. They also can consume noticeable battery power.

For legal professionals, local AI can be useful for lower-risk tasks such as:

  • Brainstorming headings for a motion or client alert 🧠

  • Rewriting your own nonconfidential prose for clarity

  • Producing a checklist from a sanitized fact pattern

  • Creating questions for a witness-preparation outline

  • Turning a public regulation or opinion into a plain-language summary

  • Developing podcast, blog, or presentation ideas while offline

  • Building prompts and workflows before using an approved firm system

The same warning applies here as it does to every generative-AI tool: an LLM is not a legal-research service, does not independently verify authorities, and can invent facts, quotations, or citations. Use it to accelerate thinking and drafting—not to replace validation. 🔍

What You Need Before You Start

You do not need a computer-science background, but you do need a reasonably current phone and realistic expectations.

Lifehacker reports that phones released within the last few years should generally be able to run smaller local models, and identifies RAM, rather than raw processor speed alone, as a particularly important practical limitation: 6 GB may be workable, while 8 GB or more is preferable. It also suggests smaller 1–2-billion-parameter models for phones with less memory. Larger models may take several gigabytes of storages

Before installation, confirm these basics:

  • Your phone uses a current version of iOS or Android.

  • You have at least several gigabytes of free storage.

  • Your phone is secured with a strong passcode, not a simple four-digit code.

  • Face ID, Touch ID, fingerprint unlock, or another biometric lock is enabled where available.

  • Your operating system and security updates are current.

  • Your firm's written technology, security, and AI policies permit the planned use.

  • You know whether your mobile-device-management system restricts unapproved apps or local file storage.

A practical starting point is a small, text-only model. "B," in labels such as "2B" or "7B," generally means billions of parameters. A smaller model usually responds faster and places less strain on the phone. A larger one may produce more nuanced output but can be slow, drain the battery, or fail to load.

Do not begin by downloading random models from unfamiliar sources. Treat model files like software: use reputable repositories, confirm the publisher, and avoid unofficial "enhanced," "uncensored," or repackaged downloads whose provenance you cannot assess. 🛡️

Step-by-Step🦶: Install a Local LLM

The exact screens will differ by phone and app version, but the workflow is straightforward. PocketPal AI and Atomic Chat are examples, not endorsements. Your firm may prefer a different approved tool.

lawyers must research llms beyond the media hype to ensure they are using them in compliance with their legal ethics!

1. Decide on an appropriate use case

Start with a task that does not require client-identifying information. For example:

"Create a checklist of issues to consider when reviewing a public-sector employee's proposed disciplinary notice. Do not provide legal advice or cite cases."

This lets you test the quality, speed, and limitations of the model without creating a confidentiality issue.

2. Download from the official app store

On iPhone, use Apple's App Store. On Android, use Google Play or another firm-approved, trusted distribution channel.

Search for either PocketPal AI or Atomic Chat, then verify the developer name, app description, and privacy disclosures before installing. 🚨 Do not install an app from a link in a social-media post, an unknown website, or an unsolicited message. 🚨

Atomic Chat represents that all inference runs on the device, that no conversation data is ever transmitted anywhere, and that it collects no chat history, prompts, or AI-generated outputs. It also states it operates without a backend server for chat data and requires no account. Its Google Play data-safety disclosure, however, notes the app may collect app activity, app-performance information, and device identifiers as anonymous analytics. These are vendor representations, not a legal guarantee; lawyers should still perform appropriate diligence.

PocketPal similarly represents that models run directly on the phone, that no data leaves the device, and that the app is open source so users can independently verify the absence of data-collection mechanisms. Its Google Play listing, though, discloses that the app "may collect" and "may share" personal information with third parties —a disclosure that appears to sit in tension with the "zero data transmission" marketing claim and underscores why a lawyer should read the actual store disclosure, not just the app description.

3. Review permissions and privacy disclosures

Before opening the app, check what permissions it requests. A basic text-only local LLM should not need unfettered access to contacts, location, microphone, camera, or every file on your phone merely to answer typed prompts.

Some permissions may be reasonable for optional features. For example, camera access could be necessary if you intentionally ask the app to analyze an image. The key is to grant permissions deliberately, not reflexively.

Review these questions:

  • Does the app require an account or sign-in?

  • Does it state that prompts, chats, and uploaded files remain on-device?

  • Does it describe analytics, crash reporting, telemetry, or advertising identifiers?

  • Does it use cloud backup, synchronization, external search, or third-party APIs?

  • Does the privacy policy reserve the right to collect or share content?

  • Can you delete chat histories and locally stored files?

  • Can the app connect to external "agents," plug-ins, or web-search tools?

"Local" may describe the core text-generation function while other features still send data elsewhere. If you enable web search, cloud backup, voice transcription, document synchronization, or third-party integrations, your analysis must change accordingly. ⚠️

4. Download a small model

When you open the app, look for Models, Model Library, or a similar option.

PocketPal's project documentation describes selecting Models, choosing a listed model for download, or adding a compatible GGUF-format model from a recognized source. It also cautions users to choose a size and quantization compatible with the phone's memory and storage.

For a first test, choose a model that is:

  • Small enough for your device

  • Clearly identified by a reputable publisher

  • Designed for general text generation

  • Recently maintained

  • Downloaded from the application's built-in catalog or an official project page

Google's Gemma family, Meta's Llama family, and Microsoft's Phi models include smaller variants intended for constrained hardware. A smaller model can be suitable for brainstorming, summarization of text you provide, basic editing, and structured checklists. It should not be treated as a reliable source for current law, jurisdiction-specific rules, or legal citations.

5. Keep the first test confidentially clean

Begin with public material or invented facts. Ask the model to summarize a public court opinion, revise a paragraph you wrote for a blog post, or develop questions for an educational presentation.

Test it with a prompt such as:

"Edit the following public-facing paragraph for clarity and professionalism. Preserve the legal meaning. Identify any claim that needs a source."

Then review the result line by line. Check every substantive legal proposition yourself.

6. Secure the local data

Local processing is only part of the security analysis. If the phone is stolen, unlocked, compromised, backed up insecurely, or shared with another person, locally stored chats and documents may be exposed.

At a minimum:

  • Use a strong device passcode and biometric lock 🔐

  • Enable device encryption, which current iPhones and many current Android devices provide when properly secured

  • Set a short automatic-lock interval

  • Avoid saving client documents in the app unless the risk assessment supports it

  • Disable lock-screen previews that could reveal sensitive notifications

  • Review cloud-backup settings for app data and chat history

  • Use remote-wipe or "find my device" capability

  • Delete test chats and downloaded material you do not need

  • Do not leave a matter open on screen in court, at an airport, or in a shared workspace

The Overlooked Risk: Models "Learning" From Attorney Input

your firm needs to train its employees/lawyers about the proper use of ai in their work!

One security question deserves special attention because it is easy to overlook: could the model itself absorb, retain, or later reproduce a client's Social Security number, date of birth, or other personal identifying information that an attorney types into it? 🚨 For a genuinely on-device, inference-only app—one that loads a fixed, pre-trained model and does not perform continuous training on your conversations—the answer should generally be no. This is often the appeal of a self-hosted LLM. The downloaded model's parameters are typically frozen; a properly built local LLM app answers using that fixed model and does not retrain itself on each new prompt. That distinguishes it from cloud services that may use submitted conversations to improve or fine-tune their systems unless a user opts out.

That reassurance, however, is only as good as the app's actual architecture and the accuracy of its disclosures, and lawyers should not accept marketing language at face value. Independent reporting on local-AI apps has documented real gaps between privacy claims and practice, including apps marketed as "private" or "local-first" that were found to have no meaningful security protecting stored conversations. Google Play's own data-safety disclosures for both PocketPal AI and Atomic Chat list categories of information the apps "may collect," including personal information for PocketPal and device or app-activity data for Atomic Chat—details that are easy to miss if a lawyer relies solely on the app-store description or promotional copy. Security researchers have also noted that on-device models and their associated data stores are not immune from device-level compromise: models and cached data stored in plaintext on a phone can potentially be extracted through malware, physical access, or forensic tools if the device itself is not adequately secured.

For a lawyer, the practical lesson is threefold:

  1. Confirm from the developer's actual privacy policy (not just app-store marketing) whether the app performs any training, fine-tuning, or cloud-connected analytics on your inputs;

  2. Never type a client's Social Security number, date of birth, account numbers, or comparable identifiers into any AI tool—local or cloud—unless that specific handling has been vetted; and

  3. Treat the phone's own security (encryption, passcode, biometric lock, remote wipe) as the last line of defense protecting whatever the app does store locally.

The Legal Ethics Analysis

self-hosted llms on your smartphone ARE GREAT WHEN YOU ARE ON THE ROAD, HAVE NO ACCESS TO THE INTERNET, OR ARE even in court!

The ABA's Formal Opinion 512 is the central national guidance point. Issued on July 29, 2024, it explains that lawyers using generative AI must fully consider their existing obligations under the Model Rules. Its principal topics include competence, confidentiality, client communication, candor, supervisory duties, and fees.

Model Rule 1.1: Competence

Model Rule 1.1 requires competent representation. Comment 8 directs lawyers to keep abreast of "the benefits and risks associated with relevant technology."

That does not require every attorney to become an AI engineer. It does require enough understanding to make informed choices. For a local phone LLM, that means knowing:

  • Whether the app truly processes prompts locally

  • Whether it trains, fine-tunes, or logs your inputs for any purpose

  • Whether a feature transmits data to another service

  • Where chat histories and documents are stored

  • Whether local files are included in a cloud backup

  • How the model's limitations affect the reliability of its output

  • Whether your phone and firm policies provide adequate security

Competence also means knowing when a task requires traditional legal research, human analysis, and source verification. A local model with no web access may be helpful for drafting, but it cannot tell you whether a case was overruled yesterday. 📚

Model Rule 1.6: Confidentiality

Model Rule 1.6 protects information relating to representation, regardless of its source. A lawyer generally may not disclose that information without informed consent, implied authorization, or another applicable exception. The ABA specifically identifies confidentiality as a core concern in generative-AI use.

A local LLM can reduce one type of disclosure risk because the prompt may stay on the phone rather than move to a cloud AI provider. But it does not eliminate confidentiality risk. The phone, app, model repository, cloud backup, external integrations, and the possibility that a client's Social Security number or date of birth could be typed into a tool without full understanding of its data-handling practices all matter.

For higher-risk client information, conduct a documented, matter-specific assessment. In some circumstances, informed client consent may be prudent or required. The answer depends on the sensitivity of the information, the tool's terms and safeguards, your jurisdiction's rules and guidance, the client's instructions, and your firm policy.

Model Rules 5.1 and 5.3: Supervision

If your firm permits staff, contract professionals, or lawyers to use local LLM apps, adopt clear controls. Model Rules 5.1 and 5.3 require appropriate supervisory efforts concerning lawyers and nonlawyer assistance.

A sensible policy can specify:

  • Approved apps and approved model sources

  • Prohibited uses and types of client data—expressly including Social Security numbers, dates of birth, and other identifying information

  • Required device-security controls

  • Procedures for verifying AI-generated legal citations

  • Review and approval requirements before any client-facing or court-filed use

  • Incident-reporting steps if a phone is lost or data may have been exposed

Model Rules 3.1 and 3.3: Candor and Accuracy

No lawyer should file AI-generated authorities, quotations, or factual assertions without verification. Courts have already made clear that invented citations can lead to sanctions and reputational damage. Local operation does not make a hallucinated case real. 🧾

Treat every AI-generated authority as unverified until you locate it in a reliable legal-research system or official source. The lawyer—not the model—signs the pleading, advises the client, and bears responsibility for the work.
See generally 3.1 and 3.3.

The Bottom Line

llms have their place in legal work if done right!

A local LLM can be a useful addition to a lawyer's technology toolkit. It can support offline brainstorming, editing, plain-language explanation, and internal workflow development while reducing routine reliance on cloud AI processing.

But privacy is not a marketing label. It is a system of facts: the app, the model, permissions, integrations, phone security, backups, firm policy, and the way you use the tool—including a clear-eyed understanding of whether your inputs are ever used to train or fine-tune anything. Start with sanitized information. Verify vendor claims against the actual privacy policy and app-store data-safety disclosures, not just the marketing copy. Secure the device. Validate every legal proposition. Then let the technology help you work more efficiently—without compromising the professional duties that define the practice of law. ⚖️📱

MTC: Claude Can Answer Your Emails. Why Lawyers Should Not Let AI Just Send Them Unreviewed. 🤖⚖️

One Click, Big Risk: AI Email Ethics for Lawyers!

David Nield’s recent Lifehacker experiment, “I Let Claude Answer My Emails for Me, and Here’s How It Went,” is worth every lawyer’s attention. Not because it reveals a spectacular AI failure. It does something more useful: it shows how competent-looking AI email automation can create professional risk precisely because it often appears to work.

Claude can now connect to Gmail, search an inbox, summarize messages, draft replies, and send emails from the connected account. The feature’s default settings are cautious: automatic sending is off unless the user changes permissions. But users can authorize individual actions—such as searching, sending, or editing labels—to “Never allow,” “Always allow,” or “Always ask for permission.”

For ordinary personal email, that may be a reasonable productivity choice. For lawyers, it demands a much more careful analysis. A law-firm email is not simply a unit of inbox administration. It may be a communication to a client, opposing counsel, a tribunal, an agency, an expert, a witness, or an insurer. It may convey legal advice, create reliance, disclose strategy, make a representation, accept a deadline, or become an exhibit.

That is why the distinction between AI-assisted drafting and AI-authorized sending matters so much. The first can be useful. The second can amount to unsupervised legal communication.

The Most Important Detail

Nield gave Claude permission to send messages automatically, but he did not test the feature with his actual editors. He decided that a hallucinated misunderstanding was not worth risking and instead conducted the experiment through an exchange with a secondary email account. That was a sensible safeguard. It is also the heart of the legal-tech lesson. 🔍

If a technology writer worries that an AI-generated email might create confusion with an editor, lawyers should recognize the dramatically higher stakes of their own communications.

Consider a few routine examples:

  • An AI responds to opposing counsel: “We agree to the requested extension.”

  • An AI tells a client: “You should withdraw the appeal and refile later.”

  • An AI replies to an agency representative: “We have no additional responsive documents.”

  • An AI responds to a settlement inquiry: “My client is prepared to accept that proposal.”

  • An AI tells a witness: “You do not need to preserve those messages.”

Each could be inaccurate, incomplete, premature, unauthorized, or inconsistent with the client’s objectives. Each could create avoidable procedural, strategic, ethical, or malpractice exposure.

The danger is not only an obvious hallucination. It is a plausible sentence sent at the wrong time, to the wrong recipient, with an unintended implication.

Competence Requires More Than Turning It On

AI Email Assistants Transform Legal Workflows With Human Oversight!

ABA Model Rule 1.1 requires competent representation. Comment 8 specifically directs lawyers to keep abreast of the benefits and risks associated with relevant technology.

That obligation does not mean a lawyer must master the underlying architecture of a large language model. It does mean a lawyer must understand what the tool can access, what it can do, what it may get wrong, and what controls exist before adopting it in a client-facing workflow.

Claude’s Gmail integration illustrates why that inquiry matters. The system can understand labels, dates, contacts, subject lines, themes, and context. It can identify a recent message, carry information through a thread, and compose a reply based on instructions. It can also use connected Google Drive data to prepare a work summary and fold that material into an outgoing email.

Those are real capabilities. They are also real risk surfaces. A connected inbox and Drive account may contain privileged communications, work product, medical records, personnel documents, settlement analyses, client financial information, litigation strategy, and confidential drafts.

Before connecting an AI platform to firm email or cloud storage, lawyers should ask:

  • What email and document data can the system retrieve?

  • What information is retained, logged, or used to improve the service?

  • Does the vendor contractually prohibit training on the firm’s data?

  • Who may access data at the provider, and where is it stored?

  • Can the firm restrict access by user, matter, mailbox, sender, or document type?

  • Can the firm produce an audit trail showing what the AI accessed, drafted, and sent?

  • What happens to the firm’s data when the subscription ends?

Those questions are not technology trivia. They are part of competent vendor assessment.

The “Cheers” Problem Is Not Trivial

Balancing AI Innovation With Human Judgment in Legal Practice

In Nield’s test, Claude composed a generally acceptable message. Yet it signed the email with “cheers,” a phrase the author said he would not ordinarily use. That small mismatch is revealing. Claude had not merely organized information. It had made a communicative choice in someone else’s name.

For a lawyer, voice is not just branding. Tone can convey firmness, concession, uncertainty, urgency, skepticism, hostility, openness to settlement, or a willingness to cooperate. A message that is “a little generic,” as Nield described Claude’s output, may be harmless when discussing weather and a meeting with oneself. It may be harmful in a dispute where each word will be parsed for meaning. ✉️

An email that begins, “We are happy to work with you,” may convey a strategic position that the lawyer did not intend. A reply that omits one key qualification can alter the practical meaning of a settlement discussion. A bot that tries to be helpful may include a fact from a prior thread that should not be repeated, or it may summarize a client’s situation so broadly that it creates a misleading record.

Lawyers should not equate grammatically fluent text with sound legal judgment.

Rules 1.2, 1.4, and 1.6

ABA Model Rule 1.2 requires lawyers to abide by a client’s decisions concerning the objectives of representation and to consult with the client about the means of pursuing those objectives. An AI system cannot determine whether accepting an extension, offering a document, softening a demand, or answering a client’s question advances those objectives.

Rule 1.4 requires appropriate client communication. An AI-generated reply can appear reassuring while omitting necessary advice, misunderstanding the issue, or providing a client with an answer that no lawyer has evaluated. A client should not receive what appears to be legal counsel when it is actually unreviewed probabilistic text.

Rule 1.6 is equally central. Lawyers must not reveal information relating to representation without authorization, subject to limited exceptions. Giving an AI provider access to email and Drive is not automatically unethical, but it requires reasonable diligence and safeguards. The more expansive the permission, the more careful the analysis must be. 🔒

A lawyer who enables automatic sending compounds the issue. Now the system is not only reading protected information; it may also select, summarize, and transmit it externally.

When AI Bots Email Each Other

Nield also raises a concern that lawyers should not dismiss: the prospect of AI systems emailing other AI systems “into infinity.”

That is more than a philosophical concern in legal practice. Imagine two firms each authorizing AI assistants to respond automatically. One system writes, “We can accommodate a brief extension.” The other interprets that as agreement, sends a confirmation, and then proposes a revised deadline. The first system responds with language suggesting continued assent.

Neither lawyer may have reviewed the exchange until a dispute arises. Yet both sides may face a written record that appears to memorialize an agreement.

The proper response is not to ban AI from legal email. It is to preserve human responsibility at the point of external communication.

The Right Workflow

Legal Technology Works Best when lawyers balance Ethics, Trust, and Accountability!

AI can help lawyers manage an overloaded inbox. It can identify urgent messages, group correspondence by matter, summarize long threads, retrieve relevant prior communications, and prepare a first draft. Those uses can reduce administrative burden and create time for legal analysis. ✅

But law firms should adopt a bright-line rule: No AI system may automatically send a substantive external communication without human review and approval.

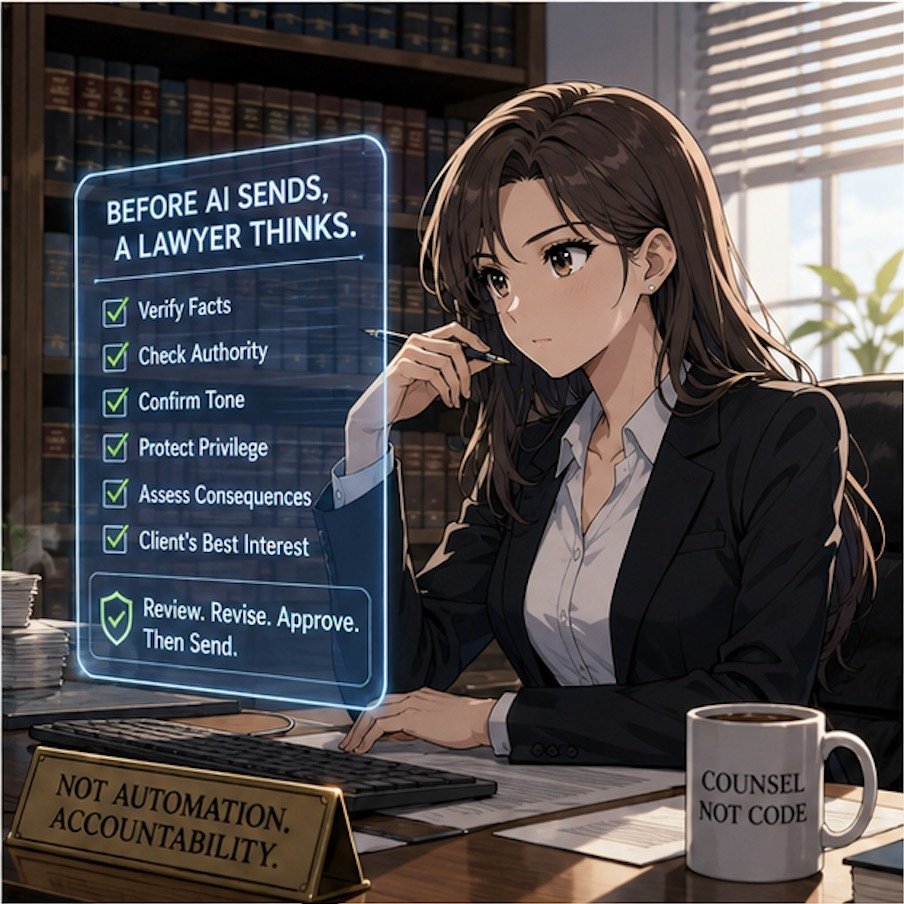
A practical protocol should require the reviewing lawyer or trained staff member to:

  • Read the full thread and relevant attachments.

  • Confirm the recipient and email address.

  • Verify every factual assertion and deadline.

  • Check for client commitments, concessions, and settlement implications.

  • Remove unnecessary confidential information.

  • Confirm that the message reflects the lawyer’s actual voice, judgment, and strategy.

  • Send the communication only after that review is complete.

Claude’s Gmail feature is impressive. It can make email easier. But as Nield’s own decision to test it only with himself demonstrates, capability is not the same as reliability, and reliability is not the same as professional responsibility.

For lawyers, the governing principle should be simple: let AI prepare the draft; let a responsible human decide whether it should ever leave the outbox. ⚖️

MTC

MTC: When Your Phone's "Self-Destruct" Button Becomes a Federal Crime: Duress Passwords, Spoliation & the Duty to Preserve ⚖️📱

lawyers should know the interplay among Duress Passcodes, Border Searches, and Smartphone Evidence Destruction

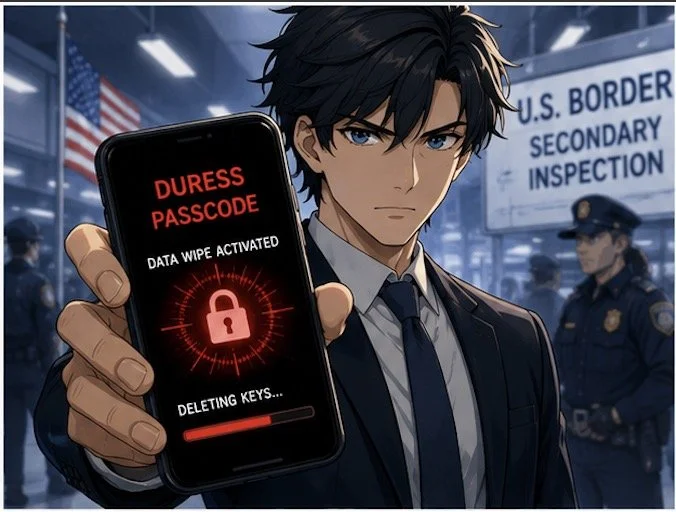
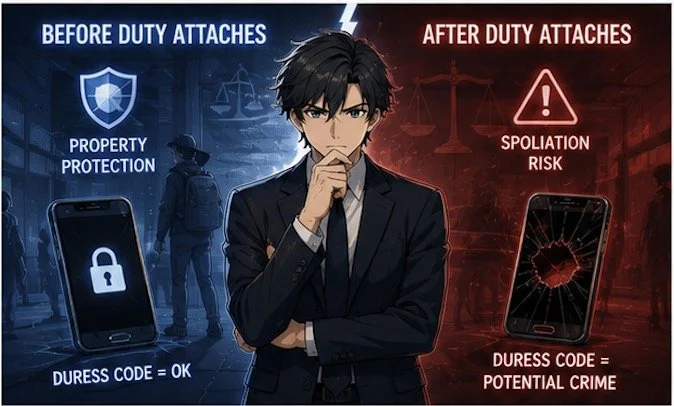
The Justice Department just indicted an Atlanta man for handing border agents a "duress passcode" that wiped his phone during a secondary inspection. It's believed to be the first prosecution of its kind — and it should put every lawyer (and every client with a smartphone) on notice. 🔔

"Duress passwords" — sometimes called "panic codes" or "coercion PINs" — are a real feature in iOS, Android, and third-party privacy apps. Enter one code and the device unlocks normally. Enter the duress code and the phone quietly obliterates its encryption keys, rendering the data unrecoverable. For journalists, activists, and anyone crossing borders with sensitive material, they're a shield. For prosecutors, they look like a loaded gun pointed at the evidence locker. 🔫💾

Here's where the professional-responsibility rubber meets the road. ABA Model Rule 3.4(a) makes it professional misconduct to "unlawfully obstruct another party's access to evidence or unlawfully alter, destroy or conceal a document or other material having potential evidentiary value." Comment 2 to Rule 3.4 clarifies that the duty attaches when a lawyer knows or reasonably should know that litigation is pending or reasonably foreseeable. A border inspection of a device you know contains responsive data? That's reasonably foreseeable. 📋

lawyers need to know the ABA Ethics Rules for Lawyers Protecting Digital Client Data!

But Rule 1.15 (Safekeeping Property) and Rule 1.6 (Confidentiality) also impose affirmative duties to protect client data. A lawyer who carries privileged communications across a border has a genuine tension: the duty to preserve vs. the duty to safeguard. The duress password sits exactly on that fault line. If you trigger it before a preservation obligation attaches — say, because your phone is stolen — it's property protection. If you trigger it after a subpoena, a litigation hold, or a border detention you knew was coming, it's spoliation. 🧨

The line isn't always bright. Good-faith accident — dropping your phone in coffee, a toddler factory-resetting your iPad — is not a crime. But intent is inferred from circumstances: Did you enable the duress feature after learning of the investigation? Did you select the code specifically for the border crossing? Did you fail to issue a litigation hold to yourself? Courts draw adverse inferences from all three. 📉

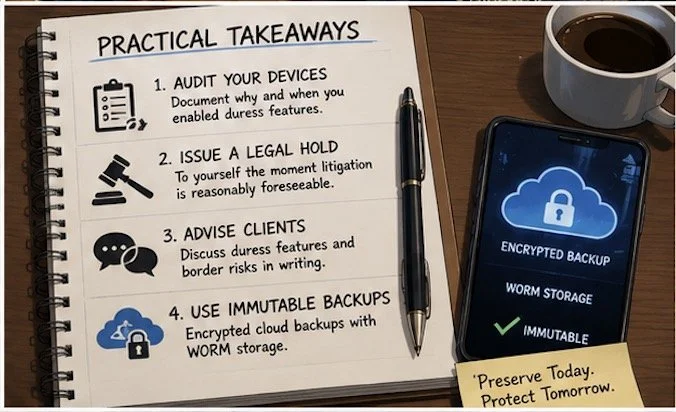
Practical takeaways for your practice:

1.      Audit your own devices now. If you use a duress feature, document why and when you enabled it — before any matter makes it suspect. 📝

2.     Issue written preservation notices to yourself the moment litigation is reasonably foreseeable.

3.     Advise clients in writing about duress features before they travel. A client who wipes a phone at the border because you never mentioned the risk creates a Rule 1.1 (Competence) and Rule 1.4 (Communication) problem for you. ✉️

4.     Use encrypted cloud backups with immutable retention (“WORM” [Write Once, Read Many] storage) so a local wipe doesn't equal total loss. That's preservation and property protection. ☁️🔒

what are the four takeaways lawyers should know when it comes to protecting client data at the boarder!

The Atlanta case will test whether providing a duress code to law enforcement is "destruction" under 18 U.S.C. § 1519 or the Federal Rules' spoliation doctrine. But you don't need the verdict to know your ethical north star: preservation obligations attach when you know — or should know — the data matters. The duress code doesn't suspend that duty; it just makes the violation faster and harder to detect. ⚡

Stay tech-savvy. Stay ethical. And maybe keep a spare phone in the carry-on or use a different phone specifically for travel. 🧳📱

MTC*

* Please remember this is an editorial not legal advice nor create an attorney-client relationship. You should contact an attorney for legal advice about your situation should the need arise.

MTC: Washington’s Bar Exam Meltdown: What It Says About Cyber Risk, Competence, and the Future of Legal Tech ⚖️💻

Washington Bar Exam Cybersecurity Crisis Exposes Legal Technology Risks!

Washington’s last‑minute cancellation of this summer’s bar exam is not just a licensing story; it is a technology and ethics story that should make every practicing lawyer sit up straight. For solo and small‑firm practitioners, this is a case study in how fragile our exam, court, and law‑practice infrastructure has become in the face of sophisticated cyber threats—and how quickly that fragility can collide with our professional duties under the ABA Model Rules.

What Happened in Washington—and Why It Matters

The Washington bar abruptly pulled the plug on its planned exam administration, citing serious concerns about system integrity and the security of the underlying technology. Although details are still emerging, the through‑line is clear: the systems that deliver and proctor high‑stakes exams are now attractive targets for attackers and highly sensitive to infrastructure failures.

Think about the impact on examinees. Months of preparation, financial investment, travel, and childcare planning vanished with a late‑stage cancellation notice. But this is not only about logistics. This is about trust: Trust in the profession’s gatekeeping machinery and in the digital rails we have built for critical legal functions. When that trust erodes, the ripple hits everything from admissions to public confidence in our systems.

For working lawyers, this is a preview of what can happen when core legal processes—hearings, filings, exams, CLEs—depend on infrastructure that may be compromised or simply not resilient enough to withstand modern threats.

From Hotel Wi‑Fi to Bar Exams: The Captive Portal Threat 🚨

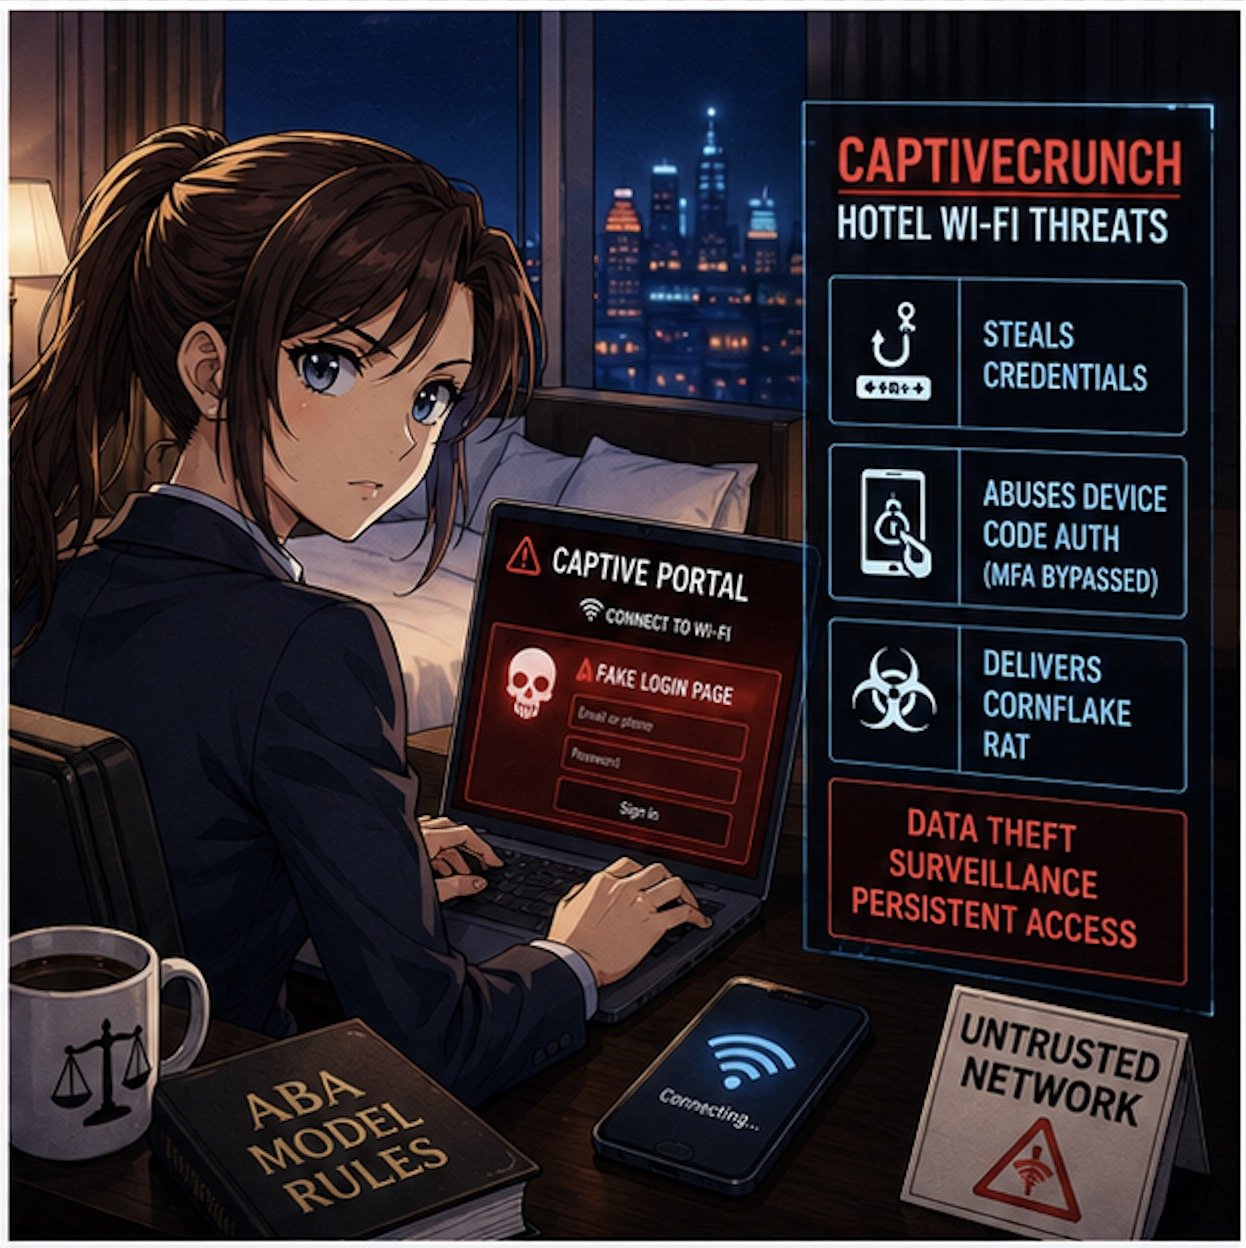
If the Washington story feels abstract, pair it with Microsoft’s recent warning about hotel and hospitality Wi‑Fi. Microsoft has identified a campaign, dubbed “CaptiveCrunch,” attributed to Russian‑linked threat actors (Storm‑2945), that hijacks captive portals—the login or “click to accept” pages we all use in hotels and conference centers—to steal credentials and deliver malware.

These attacks work by compromising the network infrastructure that sits between the user and the open internet. When a lawyer or bar examinee connects to the hotel Wi‑Fi and sees what looks like a routine sign‑in or software update prompt, that page may in fact be controlled by a threat actor. Microsoft reports that the attackers can:

  • Redirect users to fake Microsoft 365 sign‑in pages and harvest credentials without sending a phishing email.

  • Abuse device‑code authentication flows, so even multi‑factor authentication can be sidestepped if the victim enters a code and approves the request.

  • Deliver a Windows remote access trojan (“CornFlake”) that can log keystrokes, grab files, record audio and video, and maintain persistent access.

Now layer this onto the bar exam setting. You have hundreds of exam takers in hotels and rented housing, many running locked‑down exam software on laptops that still need network access for downloads, updates, or cloud syncing before or after the exam. If the exam provider’s systems or the candidates’ devices ride on compromised networks, you have a recipe for:

  • Actual or suspected compromise of exam content

  • Loss or alteration of answer files

  • Exposure of highly sensitive personal and biometric data

The bar’s decision to cancel may well reflect a recognition that once you have a credible cyber risk in the mix, it is better to protect exam integrity—even at enormous logistical and human cost—than to run an exam whose validity may later be attacked.  My heart goes out to the affected examinees, who have been left adrift in a difficult professional limbo—unable to move to the next stage of their careers and required to devote still more time, money, and emotional energy to preparing for another exam, with the hope that it will not be disrupted by malicious actors.

Ethics Meets Cyber Reality: ABA Model Rules in Play 📜

CaptiveCrunch Hotel Wi-Fi Attacks Threaten Lawyers’ Digital Security

This is where your daily practice intersects directly with the bar’s meltdown.

Model Rule 1.1 (Competence) explicitly includes a duty to understand “the benefits and risks associated with relevant technology.” Cyber threats like CaptiveCrunch are now squarely within “relevant technology.” If you travel for hearings, depositions, client meetings, or bar events and routinely connect to hotel Wi‑Fi without safeguards, you are not just taking a personal risk; you may be jeopardizing client confidences, privileged communications, and case strategy.

Model Rule 1.6 (Confidentiality of Information) requires reasonable efforts to prevent unauthorized access to client information. Using untrusted hotel or conference Wi‑Fi without protections—especially when we now have concrete warnings from Microsoft—raises tough questions about whether your security posture is still “reasonable.”

Model Rule 5.3 (Responsibilities Regarding Nonlawyer Assistance) and Rule 5.1 (Supervisory Lawyers) also surface here. When your cloud vendors, exam providers, or outsourced IT teams operate systems on which your work depends, your duty is not satisfied by “we assumed they had it handled.” You must perform due diligence, ask questions about security practices, and be prepared to adjust your workflows when a vendor’s risk profile changes.

The Bar Exam as a Canary in the Cyber Coal Mine 🐤

The Washington bar exam cancellation looks like a one‑off crisis, but it is better seen as a canary in the coal mine for the entire legal ecosystem.

We increasingly rely on:

  • Online proctoring systems for bar exams, law school tests, and certifications

  • Remote hearing platforms and e‑filing systems for courts

  • Cloud‑based case management, timekeeping, and trust accounting tools

Each of these systems sits on infrastructure that can be compromised at the network, platform, or endpoint level. The CaptiveCrunch campaign shows that attackers are willing to invest in compromising hospitality networks globally, in part because those networks handle high‑value corporate and professional traffic.

If attackers can hijack captive portals to intercept Microsoft 365 logins and deliver Remote Access Trojans (RATs) like CornFlake, they can also target:

  • Judicial staff connecting from hotels during conferences

  • Law firm partners working on the road

  • In‑house counsel traveling to negotiation sessions

Once a single endpoint is compromised, attackers can move laterally into cloud resources, email archives, document management systems, and case data.

In other words, the Washington bar’s crisis is the profession’s crisis—just seen in extreme close‑up.

Practical Security Takeaways for Solo and Small‑Firm Lawyers 🛡️

So what do you do differently now?

Microsoft’s recommendations for travelers are a good starting point: assume guest networks are untrusted, favor mobile hotspots or secured private connections, and avoid performing updates or entering credentials through captive portals. Let’s translate that into concrete steps for law practice:

Travel Playbook

  • Prefer your phone’s hotspot or a dedicated travel router with a trusted VPN when accessing email, case management, or client files on the road.

  • If you have no choice but to use hotel or other public Wi‑Fi, connect only through a reputable VPN and treat the captive portal as a necessary but dangerous doorway.

  • Complete only the minimum captive‑portal steps needed to get online, and then avoid entering passwords, approving authentication prompts, or installing updates until your VPN is active and you are past the captive‑portal page.

Authentication Hygiene

  • Move to phishing‑resistant authentication where possible (hardware security keys, platform authenticators) and restrict device‑code flows unless truly needed

  • Train your team to treat unexpected device‑code prompts or update pages during hotel logins as red flags, not background noise.

Vendor and Exam Provider Scrutiny

  • Ask pointed questions about incident response, logging, and how they handle suspected network compromise.

  • Build contingency plans—if an exam, hearing, or critical system fails or is compromised, what is your fallback?  (Perhaps a cheap backup laptop? Apple has a pretty good return policy - check provider details for timeliness and other requirements.)

Final Thoughts: Looking Ahead - Resilience, Not Just Compliance ✅

Cybersecurity Competence Is Now Essential for Modern Legal Practice!

The Washington bar’s decision to cancel its exam sends a hard message: compliance checklists and bare‑minimum security are no longer enough. We need resilience—systems and workflows designed to fail gracefully, with clear fallback paths that do not compromise integrity or fairness.

For bar authorities and courts, that means:

  • Building redundancy into exam and hearing platforms

  • Running adversarial security testing and tabletop exercises

  • Communicating transparently with stakeholders about how cyber risk is identified and mitigated

For practicing lawyers, it means re‑framing technology as part of our core competence, not a bolt‑on afterthought. Model Rule 1.1’s commentary on technology is not aspirational; it is a reflection of the reality that our ethical duties now live at the intersection of law and information security.

The bar exam meltdown in Washington is a wake‑up call. Pair it with Microsoft’s warning on hotel Wi‑Fi, and the message is unmistakable: our digital rails are under live fire. The question is whether we treat this as yet another “unprecedented” event—or as the moment we upgrade our tools, our habits, and our ethics posture to meet the threat.

MTC

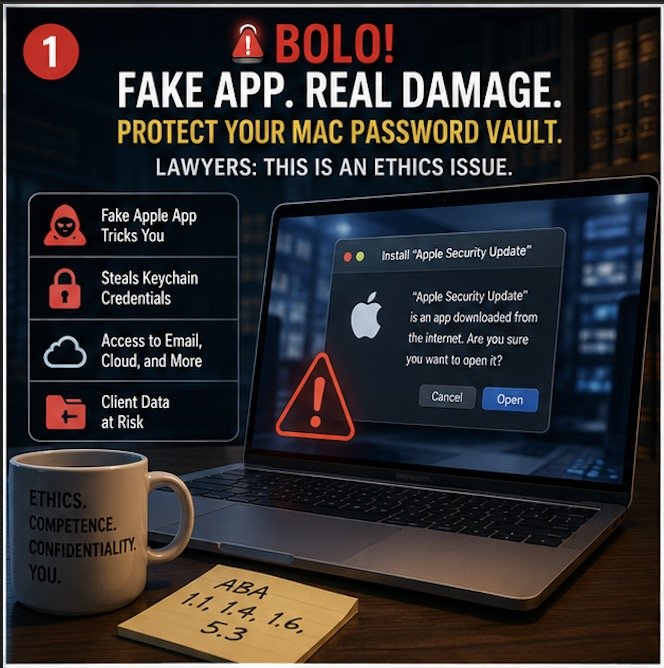
🚨BOLO! Fake Apple App Steals Mac Password Vaults: What Lawyers Must Do Now 🔐⚠️

If you use a Mac in your law practice, this is a “stop and read” moment.

Fake Apple App Threatens Lawyers’ Mac Password Security

A newly identified piece of malware—disguised as a legitimate Apple application—has the ability to trick users into surrendering access to their macOS password vault. That means saved credentials, system access, and potentially client data are all in play. For lawyers, the implications go well beyond inconvenience. This is an ethics issue. 🚨

According to Malwarebytes’ recent threat intelligence report, attackers are distributing a fake Apple app that convincingly mimics legitimate system prompts. Once installed, it requests elevated permissions and can capture macOS Keychain credentials—the same vault many attorneys rely on to store passwords and secure notes.

That should immediately raise a red flag for anyone responsible for client confidentiality.

Why This Matters for Lawyers

Many attorneys assume macOS provides a higher baseline of security. That assumption is not entirely wrong, but it is incomplete. Threat actors are increasingly targeting Mac users because of that very complacency.

If your Keychain is compromised, an attacker may gain access to:

  • Email accounts containing privileged communications 📧

  • Cloud storage platforms holding client files ☁️

  • Practice management systems

  • Financial accounts and trust systems 💼

This is not just a cybersecurity issue—it is a professional responsibility issue under multiple ABA Model Rules.

The Ethics Layer You Cannot Ignore

Let’s connect the dots to your obligations.

Mac Malware Mimics Apple Prompts to Steal Keychain Credentials

ABA Model Rule 1.6 (Confidentiality of Information) requires attorneys to make reasonable efforts to prevent unauthorized access to client information. Falling for a well-crafted phishing or malware attack does not automatically mean a violation—but failing to implement reasonable safeguards might.

ABA Model Rule 1.1 (Competence) now explicitly includes technological competence. Comment 8 makes clear that lawyers must understand the “benefits and risks associated with relevant technology.”

If you are not aware that fake system prompts exist—or that macOS Keychain can be targeted—you are already behind the curve.

ABA Model Rule 5.3 (Responsibilities Regarding Nonlawyer Assistance) also comes into play if your staff installs software or clicks prompts without proper training.

This is why I often emphasize in both my blog and podcast that cybersecurity is no longer optional—it is foundational.

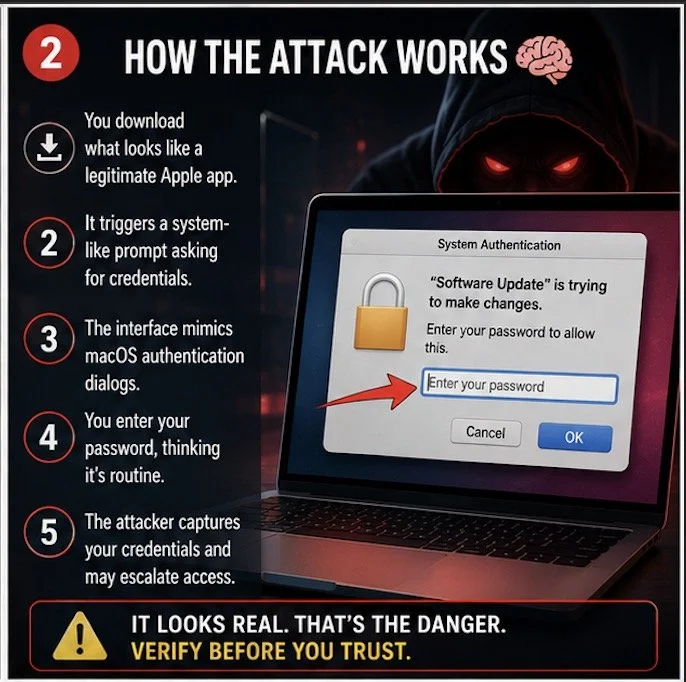
How the Attack Works 🧠

The attack is deceptively simple:

  • A user downloads what appears to be a legitimate Apple-related application.

  • The app triggers a system-like prompt requesting credentials.

  • The interface closely mimics macOS authentication dialogs.

  • The user enters their password, believing it is a routine request.

  • The attacker captures the credentials and may escalate access.

This is classic social engineering layered with technical sophistication.

And here is the uncomfortable truth: even experienced professionals can be fooled when the interface looks authentic.

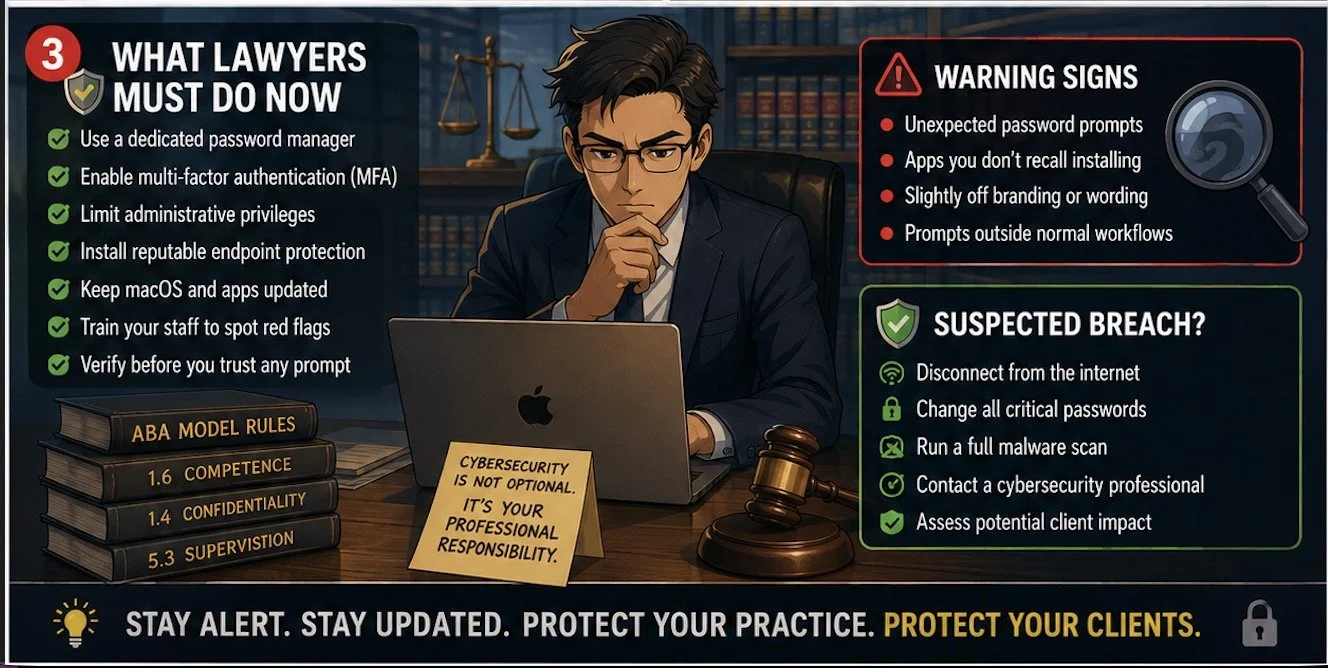
Warning Signs You Should Not Ignore

While these attacks are convincing, they are not perfect. Look for:

  • Unexpected prompts asking for your Mac password 🔑

  • Requests tied to apps you do not recall installing

  • Slightly off branding, spacing, or wording

  • Prompts appearing outside normal workflows

When in doubt, stop. Do not enter credentials.

Instead, open System Settings directly and verify whether any legitimate action requires authentication.

💡 TIP:  Download Apps directly from the Apple App Store.  These applications are vetted by Apple and are less likely to be malware!

Practical Safeguards for Your Practice 🛡️

You do not need to become a cybersecurity expert. But you do need a defensible baseline.

Start here:

  • Use a dedicated password manager instead of relying solely on Keychain.

  • Enable multi-factor authentication (MFA) across all critical systems.

  • Limit administrative privileges on your Mac.

  • Install reputable endpoint protection software.

  • Keep macOS and all applications updated.

  • Train your staff to recognize suspicious prompts.

Incident Response: What If You Already Clicked?

  • If you suspect you interacted with a fake app:

  • Disconnect from the internet immediately 🌐

  • Change all critical passwords from a separate, clean device

  • Run a full malware scan

  • Contact a cybersecurity professional

  • Assess whether client data may have been exposed

At that point, your ethical obligations may shift toward disclosure.

Under ABA Model Rule 1.4 (Communication), you may need to inform affected clients if their data was compromised. Timing and scope matter, so consult ethics counsel where appropriate.

Lawyers Must Strengthen Mac Cybersecurity and Client Data Protection

The Bigger Picture

This is not just about one fake app.

It is about a shift in the threat landscape. Attackers are no longer relying on obvious scams. They are leveraging trust—your trust in Apple, your trust in familiar interfaces, your trust in your own habits.

That is why vigilance must become part of your daily workflow.

As I have discussed before, technology amplifies both efficiency and exposure. The same tools that make your practice more productive also expand your attack surface.

Final Thought

You do not need to panic. But you do need to pay attention.

The lawyers who thrive in this environment are not the most technical—they are the most aware.

Stay alert. Stay updated. And treat every unexpected prompt like it matters—because it might. 🔍

MTC: Law School, Laptops, and AI: Why Banning Computers Misses the Point!

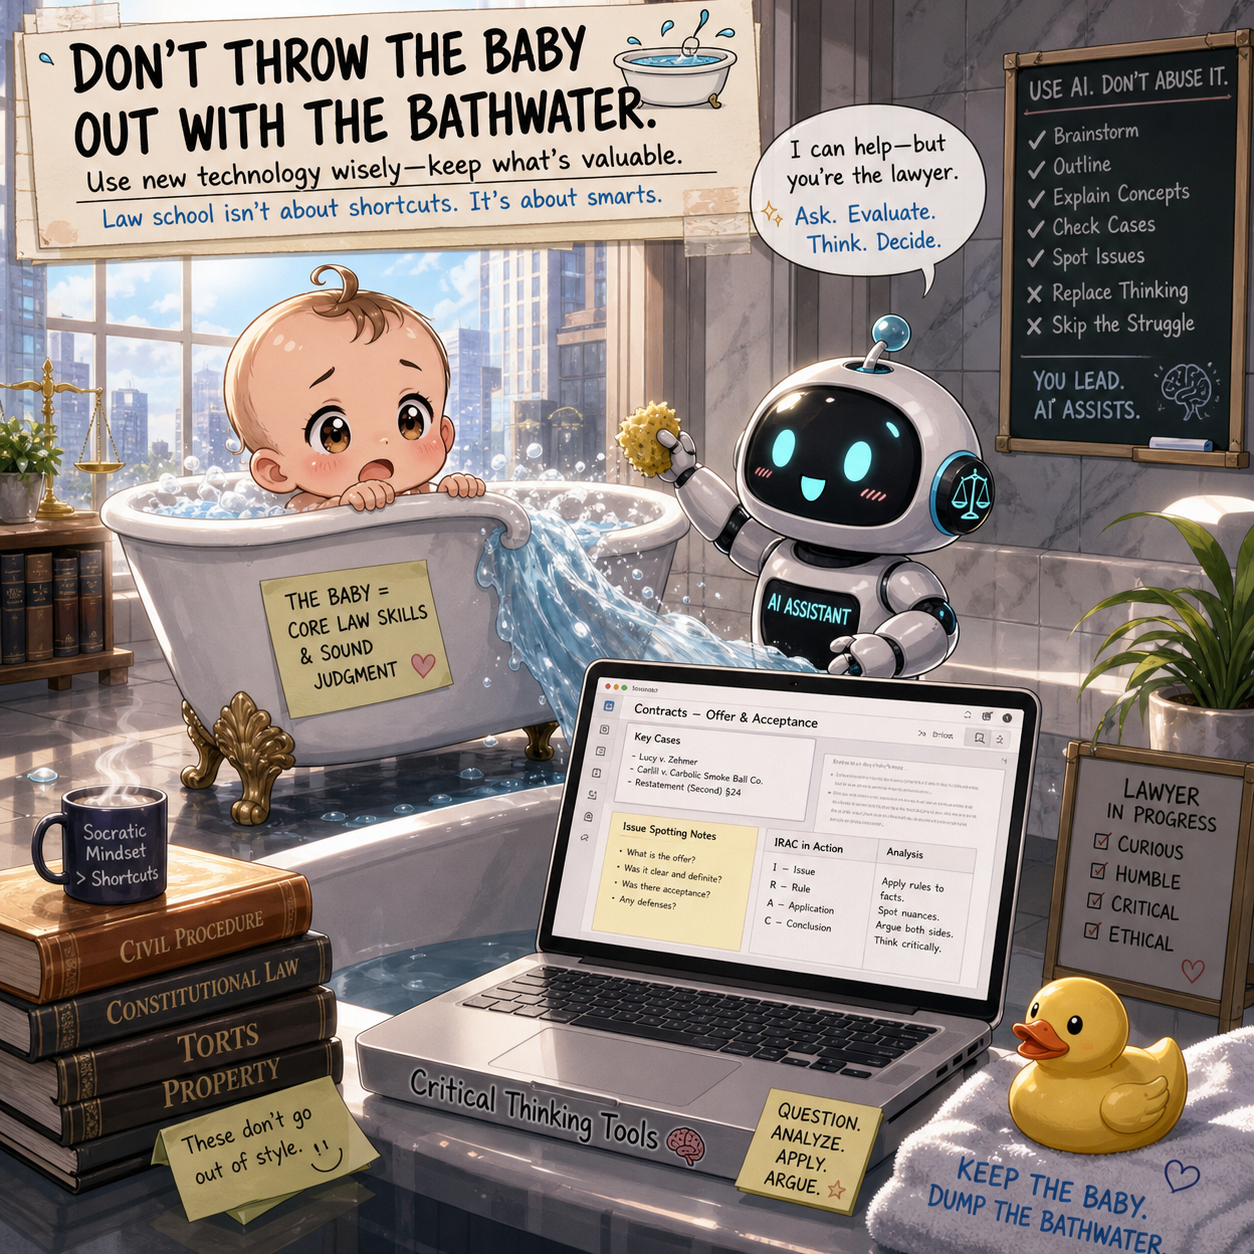
Law schools are throwing out the baby with the bathwater by banning laptops from the classroom as an effort to combat improper ai use.

On July 10, 2026, the conversation around artificial intelligence in legal education reached a new level. Reports of universities banning both AI tools and laptops in classrooms reflect a growing anxiety: how do we preserve critical thinking in an age of automation? ⚖️
It is a fair question. It is also the wrong solution.

Let me be clear at the outset. A first-year ban on AI tools makes sense. A blanket ban on laptops does not.

The Case for Limiting AI—At First

Legal education has always been about building judgment. That means learning how to analyze facts, synthesize doctrine, and construct arguments from scratch. AI short-circuits that process if used too early.

Under ABA Model Rule 1.1 (Competence), lawyers must provide knowledgeable and skilled representation. That competence begins in law school. If students rely on AI before they understand the law themselves, they risk becoming operators instead of thinkers.

As I have noted in prior discussions on legal technology, AI should augment—not replace—legal reasoning.

So yes, a structured limitation on AI during the first year is defensible. It creates a foundation. It forces students to wrestle with ambiguity. It builds intellectual muscle. 💡

But Banning Laptops? That Is an Overreach

This is where the policy breaks down.

When I entered law school then graduated in 2002, laptops were just beginning to appear in classrooms. They were not universal. They were not always welcome.

For me, the laptop was not a distraction. It was essential.

My handwriting was and sadly still is poor. My ability to type, organize notes, and revise quickly made the difference between struggling and succeeding. My laptop was not a shortcut. It was an accessibility tool before we used that term widely.

Fast forward to today. Students are typing far more than they write. Many have never learned cursive. Their academic workflows are digital from the start.

To remove laptops is not to level the playing field. It is to shift it—often unfairly.

The Practical Reality of Modern Learning

Legal education does not exist in a vacuum. Law practice is digital.

Law students who learned on laptops will be disadvantaged if classrooms suddenly ban them.

Under ABA Model Rule 1.1, Comment 8, lawyers must understand the benefits and risks of technology. That obligation does not begin after graduation. It begins in law school.

Students today must learn:

  • How to organize digital research

  • How to draft and revise efficiently

  • How to manage documents and workflows

  • How to integrate technology into legal reasoning

You cannot teach modern legal competence while removing the primary tools of modern legal work. 🖥️

A laptop is not the problem. Misuse is.

The Enforcement Problem No One Is Talking About

There is also a practical issue. Banning AI is difficult to enforce. Banning laptops is easy.

That does not make it the right policy.

If anything, banning laptops is a workaround for the harder problem of AI enforcement. It is a policy by convenience.

And it raises a deeper concern under ABA Model Rule 5.3 (Responsibilities Regarding Nonlawyer Assistance), which increasingly applies to AI tools. Lawyers—and future lawyers—must learn to supervise and evaluate AI outputs.

You cannot teach supervision by eliminating exposure.

A Better Approach: Controlled Access, Not Prohibition

Law schools should be experimenting with smarter controls instead of blunt bans.

Some possibilities include:

  • Disabling Wi-Fi and cellular signals in certain classrooms 📶

  • Using locked-down exam or classroom software environments

  • Creating AI-permitted and AI-prohibited assignments with clear boundaries

  • Requiring disclosure of AI use in coursework

  • Teaching prompt engineering and AI verification as part of the curriculum

This approach aligns with ABA Model Rule 1.6 (Confidentiality) as well. Students must learn what data can and cannot be shared with AI systems.

Exposure with guardrails is more effective than prohibition. That principle applies directly to how law schools should approach AI.

Critical Thinking and Technology Are Not Opposites

There is a persistent myth underlying these bans: that technology erodes thinking.

That is not inherently true.

Technology can weaken thinking if it replaces effort. It can strengthen thinking if it supports it.

A student who uses a laptop to organize case law, annotate notes, and refine arguments is not thinking less. They are thinking differently—and often more effectively.

The same will eventually be true of AI.

The goal is not to create lawyers who avoid technology or who think less by using AI. It is to create lawyers who use it wisely. ⚖️
What Law Schools Should Be Teaching Instead

If I were designing a first-year curriculum today, I would include:

THE MODERN LAWYER NEEDS TO KNOW HOW TO BALANCE JUDGMENT WITH AI USE IN THEIR WORK!

  • A temporary restriction on AI-generated work

  • Mandatory instruction on how AI tools function

  • Exercises in verifying AI outputs against primary sources

  • Training on ethical risks, including hallucinations and confidentiality

  • Continued use of laptops as standard tools

This approach respects both sides of the equation: foundational thinking and technological competence.

Final Thought: Do Not Solve the Wrong Problem

Law schools are right to be concerned. AI is reshaping the profession at a rapid pace.

But banning laptops is not a solution. It is a signal of discomfort.

The better path is harder. It requires nuance. It requires experimentation. It requires trust in students, guided by structure.

Most importantly, it requires recognizing that the future lawyer will not choose between thinking and technology.

They will need both.

And law school is exactly where they should learn how to do that. 🚀