MTC: Why Lawyers Should Wait Before Upgrading to the iPhone 18 Pro Max and Apple Watch Ultra 4, let alone any new hardware upon release 📱⌚⚖️

Why Lawyers Should Wait Before Buying New Hardware!

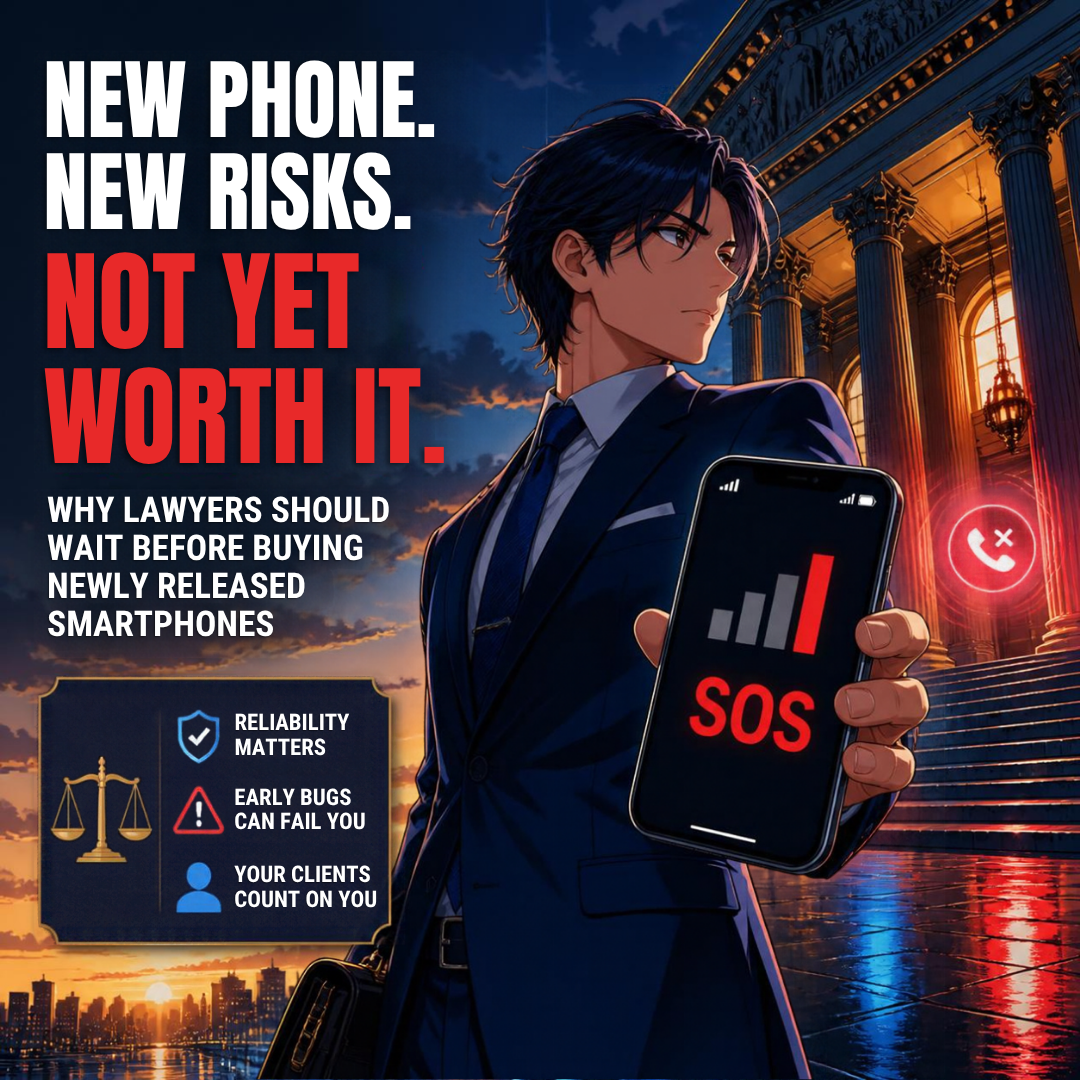
I'll admit it up front. I love Apple products. 🍎 My desk, my bag, and my wrist tell that story better than I can. Every September, I feel the pull of the keynote and all the reviews that follow. This year, I'm holding back. I haven't upgraded to the iPhone 18 Pro Max or the Apple Watch Ultra 4. Two news stories explain why.

This isn't an anti-Apple column. But it is an early adoption/purchase warning! ⚠️ Apple will likely fix both issues. But lawyers don't get to treat new hardware like a hobby purchase (as much as I’d like to! 🤗). Our devices carry client secrets, court deadlines, and our professional reputations. That changes the math. ⚖️

What Happened With the iPhone 18 Pro Max 📵

Lifehacker reports that a "small number" of iPhone 18 Pro Max units on AT&T can lose cellular service and show an SOS icon. Affected phones may not be able to make cellular calls. That may include calls to 911. 🚨

Apple released iOS 27.0.1 and an AT&T carrier-settings update. Those updates are meant to prevent the problem. They do not fix a phone that has already lost its connection. According to Lifehacker, the fix for an affected phone is a free exchange through Apple or AT&T. It is treated as a hardware defect under warranty.

Think about what that means for a solo practitioner. Your phone is your office line, your two-factor authenticator, and your client hotline. If it goes dark on a hearing day, the warranty does not help you that morning.

What Happened With the Apple Watch Ultra 4 ⌚🔥

MacRumors reports that some Apple Watch Series 12 and Ultra 4 owners describe a burning sensation and redness under the sensor area. The new models check heart rate every five seconds. They also have a larger ECG electrode surface and larger green LEDs. MacRumors notes that no one yet knows whether those changes cause the irritation.

The Mac Observer adds an important caution. The reports do not establish a widespread defect, and no common cause has been confirmed. Apple's guidance points to band fit, trapped sweat, and soap. Apple also advises anyone with redness or swelling to consult a physician before wearing the watch again. 🩺

Some owners say the irritation cleared up. Others returned their watches. Either way, I'd rather not run that experiment on my own wrist during trial prep.

Rule 1.1: Competence Includes Knowing When Not to Buy 🧠
A Lawyer’s Guide to Safer hardware Upgrades.

ABA Model Rule 1.1, and Comment 8, require lawyers to keep up with the benefits and risks of relevant technology. Most of us read that as a duty to adopt. It is also a duty to evaluate. 🔍

Early adopters absorb the first wave of defects. That is a fair trade for a hobbyist. A lawyer's risk tolerance should be lower. Knowing about a known defect and buying anyway is not technology competence. It is impulse.

Rules 1.3 and 1.4: Reachability Is an Ethics Issue 📞

Rule 1.3 requires reasonable diligence and promptness. Rule 1.4 requires you to keep clients reasonably informed and to respond promptly to reasonable requests for information.

A phone stuck on SOS can't take a client's urgent call. It can't receive a text from opposing counsel about a continuance. It can't reach the court clerk. Wi-Fi calling may cover you at the office. It won't cover you in a parking garage outside the courthouse. ⏰

Rule 1.6(c): The Warranty Swap Is a Confidentiality Event 🔐

Here's the part many lawyers miss. A defective device usually ends in an exchange. An exchange means your phone leaves your custody.

Rule 1.6(c) requires reasonable efforts to prevent unauthorized access to client information. Before any device goes back to Apple or a carrier, you need a verified backup. You need to move your authenticator apps. You need to sign out of firm accounts, remove the device from management tools, and complete a secure wipe.

A dead phone makes that harder. If it won't connect, you may struggle to receive verification codes on the very device you're trying to replace. Plan for that before you buy, not after. 🧯

I covered device offboarding in MTC: Apple Upgrade Lease vs. Buying vs. Carrier Financing — Which iPhone 18 Pro Deal Actually Works for Solo and Small Firm Lawyers? That written wipe protocol matters even more when the exchange is unplanned.

The Legal and Logistical Fine Print 📜
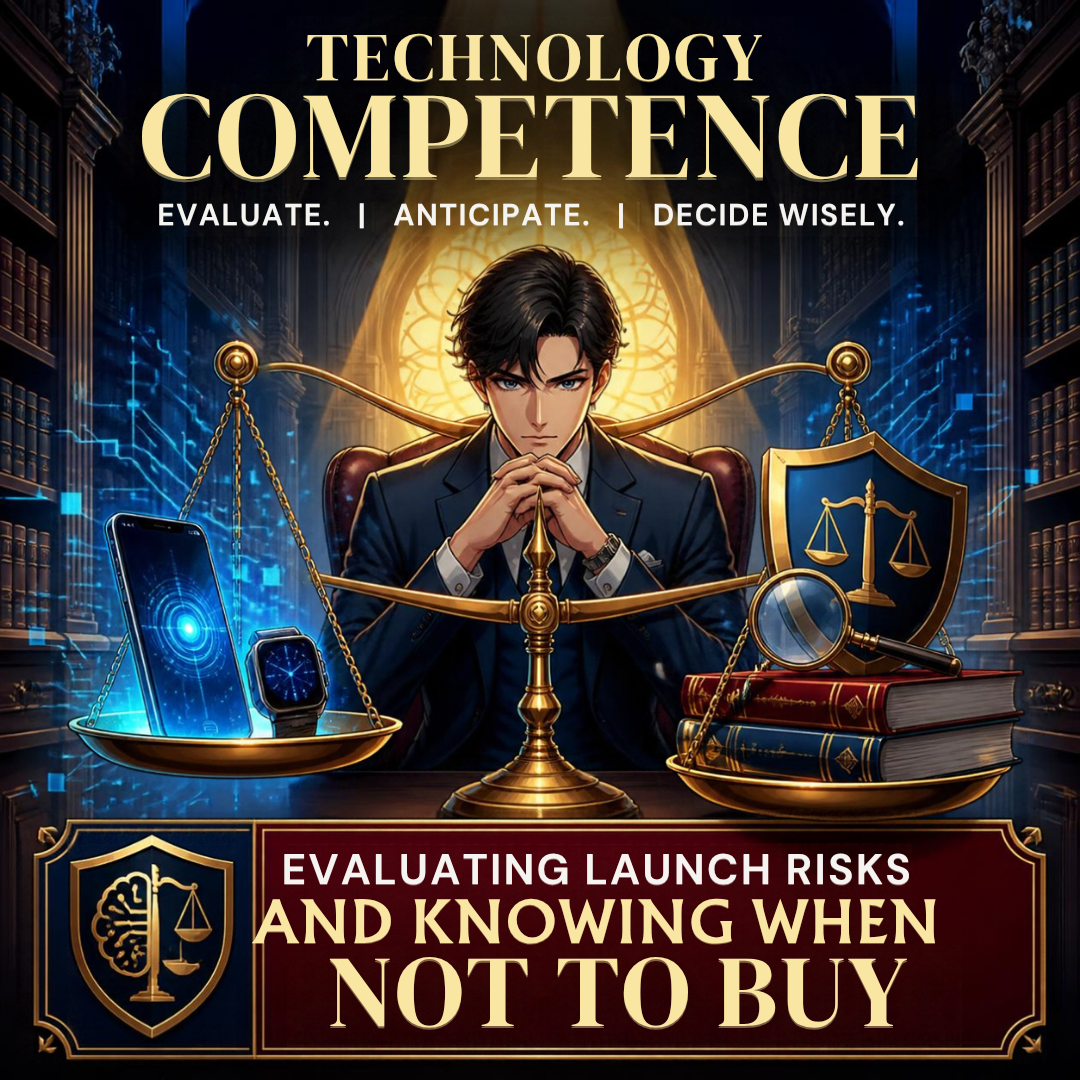
Technology Competence Means Waiting Before Every Hardware/software Upgrade!

Defects also raise contract questions. Read them before checkout.

  • Return windows: Apple's standard return window is short. Apple’s return policy is 14 days from receipt for Apple Store purchases. Skin irritation that appears after "several days" can push you close to that line.

  • Carrier lock-in: As I noted in my financing post, some carrier promotions spread bill credits over 36 months. Leaving early can forfeit the remaining credits and leave you responsible for the unpaid balance. A defective phone does not always unwind that deal cleanly.

  • Lease condition terms: Apple Upgrade requires a return in good working condition. Know how a defect exchange affects your lease term and buyout before you sign.

  • Emergency calling: If your phone cannot reach 911, that is a safety issue first. It can also become an employment and liability issue if the firm issued the device to a staff member who travels alone. 🚨

  • Firm-issued devices: If your firm hands staff a new watch or phone, you own part of that rollout. Rules 5.1 and 5.3 require reasonable measures for the conduct of lawyers and nonlawyer staff. That includes device policies. 👥

Treat Apple and your carrier like any other vendor. My Word of the Week on vendor risk management for law firms explains the mindset. Hardware is a vendor relationship too.

A Practical "Wait and Watch" Checklist ✅

  1. Wait 30 to 60 days after launch. Let the first software patches land.

  2. Read the support forums and trusted tech outlets before buying.

  3. Confirm your return window and keep the receipt handy.

  4. Keep your current device working until the new one proves itself. 📱

  5. Back up, verify the backup, and document your authenticator transfers.

  6. Test cellular calls, including your carrier's emergency settings, on day one.

  7. Wear a new watch on a loose band at first. Stop if irritation appears. ⌚

  8. Write it down. A short device-change log shows reasonable efforts under Rule 1.6(c).

If you're still deciding which phone fits your practice, see MTC: iPhone 18 Pro vs. iPhone Duo vs. Samsung and Pixel Foldables — Which Smartphone Is Better for Lawyers? The right device is the one that supports competent, secure representation.

My Bottom Line 🎯
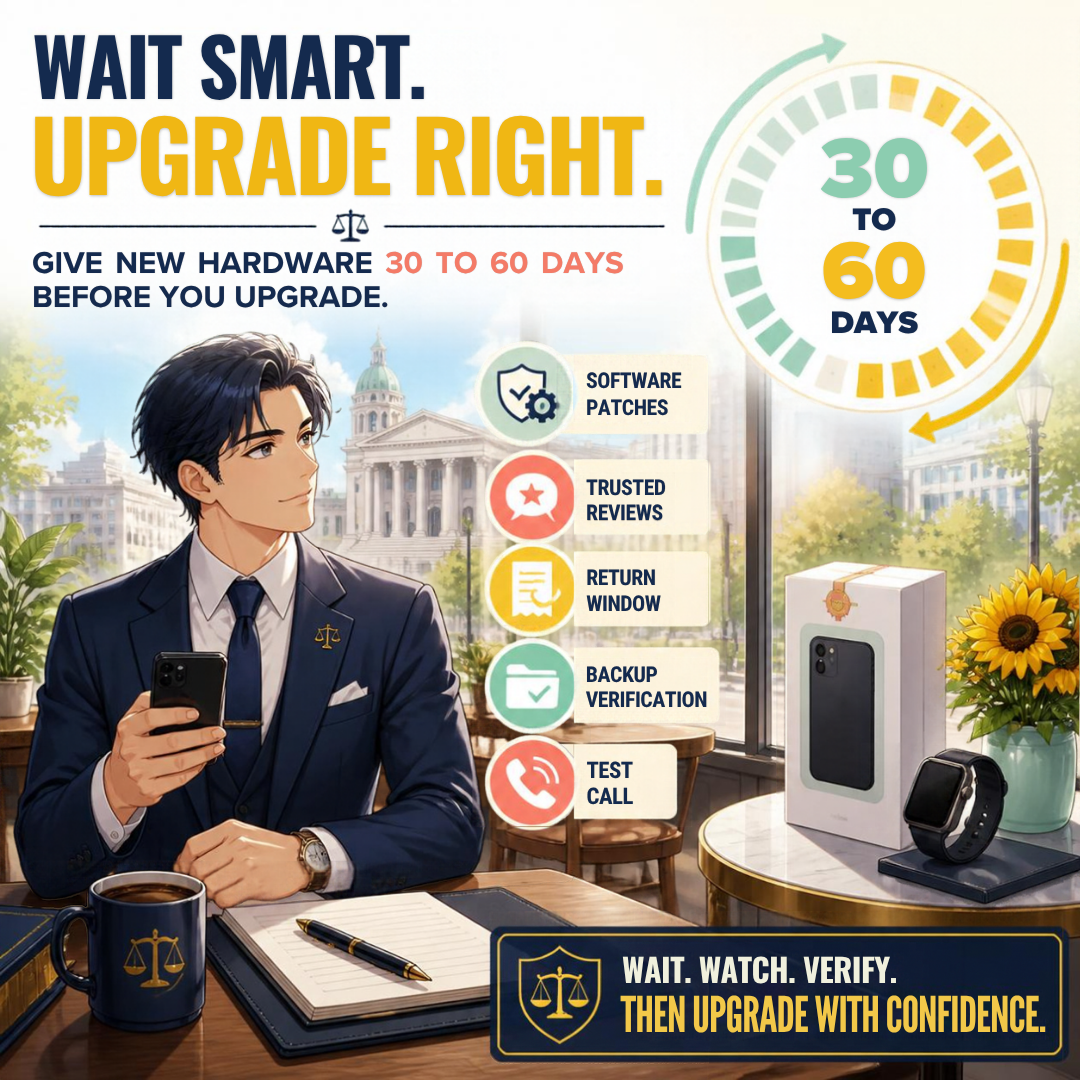
Wait, Watch, and Verify: A Legal Technology Upgrade Checklist!

I still expect to own both devices. Apple has a long track record of fixing launch problems. iOS 27.0.1 is already a sign of that. But "eventually fixed" is not the standard for a law practice. Reliability is. Patience, in this case, is simply good risk management. 🛡️

Let the early adopters of any new electronic hardware find the edges. Let the patches arrive. Then upgrade on your schedule, with a plan, and with your client data protected. Your clients will never thank you for being first in line. They will notice if you can't be reached. 🍎⚖️

MTC
MTC: Meta Muse, Google Gemini Spark, and Apple's Full Disk Access Warning: What Lawyers Must Know Before Letting a Personal AI Agent Run Their Computer 🤖⚖️🔐

AI Agents and Legal Ethics: What Lawyers Must Know!

The personal AI agent has arrived. It is not a chatbot that waits for your next question. It is software that works on your behalf, around the clock, while your laptop sits closed on the kitchen table. 🕒

Meta launched Muse in September 2026 and described it as a personal agent that "actually does the work." Days later, Meta released a Mac version of Muse that can act directly on your computer with permission. It can organize your Downloads folder, find files, and summarize your Messages, Calendar, and notes. Google is on the same path. Its Gemini Spark agent, announced at Google I/O 2026, runs on dedicated virtual machines in Google Cloud. It keeps working after you lock your phone, and Google has promised Mac desktop support for local files. OpenAI joined the race on September 29 with Dots. Business Standard reports that each Dots agent has its own cloud computer and browser and can connect to more than 4,000 applications.

Then Apple spoke up. 🍎

Apple's Warning Is Not Just Corporate Grumbling 🚨

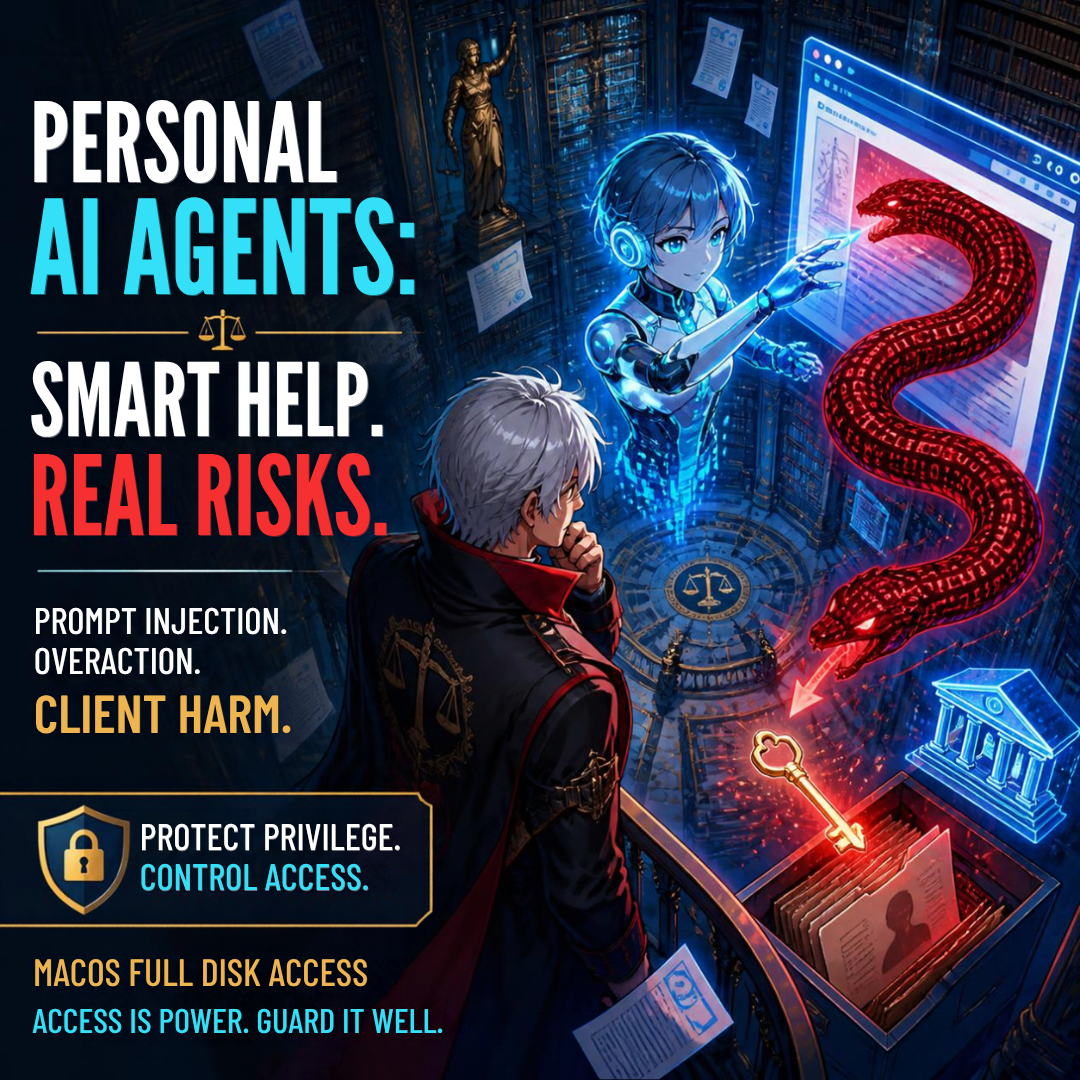
On October 2, 2026, Apple announced additional controls for macOS Full Disk Access. Apple explained that the permission largely sidesteps its other privacy controls. It was designed for backup apps. Now some developers ask users to grant it routinely. That can expose files, mail, messages, and browsing history without users fully understanding the consequences. Apple named the growing risk from AI agents, with Meta's Muse and OpenAI's Dots cited as examples. Going forward, users who want to grant this "extraordinary level of access" will have to take "very explicit user action." Apple has not yet said when the controls will arrive.

Some will dismiss this as Apple protecting its turf. Lifehacker frames the change as Apple "making it harder to run agentic AI on your Mac." It also notes that Apple does not offer frontier models of its own the way OpenAI and Anthropic do. Competitive motives may well be present. But lawyers should focus on the substance. Apple's most important point is this: Full Disk Access does not only expose you. It can expose everyone you communicate with. 📨

For a lawyer, "everyone you communicate with" means clients, opposing counsel, courts, and witnesses. That is the heart of the problem.

What Lawyers Should Actually Worry About ⚠️

The Lawyer’s Checklist for Responsible Personal AI Agents!

  1. Confidentiality under ABA Model Rule 1.6. Rule 1.6(c) requires reasonable efforts to prevent the unauthorized disclosure of, or access to, client information. A personal agent with full-disk rights can read every privileged email, client text, and draft brief on your machine. If that agent sends content to a vendor's cloud for processing, you have disclosed client information to a third party. You must understand that flow before you click "Allow." ABA Formal Opinion 512 makes clear that the existing rules apply fully to generative AI. There is no AI exception.

  2. Competence under Model Rule 1.1. Comment 8 requires lawyers to keep abreast of the benefits and risks of relevant technology. Competence here means knowing what the agent can see, what it can do in your name, and whether its actions are logged. Consumer marketing pages are not enough. Read the terms on data retention, model training, and subprocessors. 📚

  3. Prompt injection and "overaction." Lifehacker highlights a chilling scenario: a poisoned prompt hidden on a website manipulates an agent into exposing bank access. I covered this danger in MTC: When AI Lawyers' Assistants Start Acting as an Agent: Why Autonomous Agents Cannot Be Given the Keys to Your Law Practice ⚖️. The dangerous combination is untrusted content, broad access to sensitive data, and authority to act. Full Disk Access delivers the second ingredient in one click. 🧨

  4. Supervision under Model Rules 5.1 and 5.3. Software that acts for you is functionally nonlawyer assistance. Partners and supervising lawyers must have measures in place to ensure its conduct is compatible with your professional obligations. "The agent did it" will not persuade a disciplinary counsel.

  5. Communication and fees under Model Rules 1.4 and 1.5. Some clients will want to know whether a consumer agent touches their files. Opinion 512 also warns against billing clients for time a tool saved or for learning a tool you chose to adopt.

How Do Cloud Personal Agents Compare with Self-Hosted AI? 🖥️☁️

Cloud AI vs. Local AI: What is a lawyer’s best set up that follows bar ethic rules?!

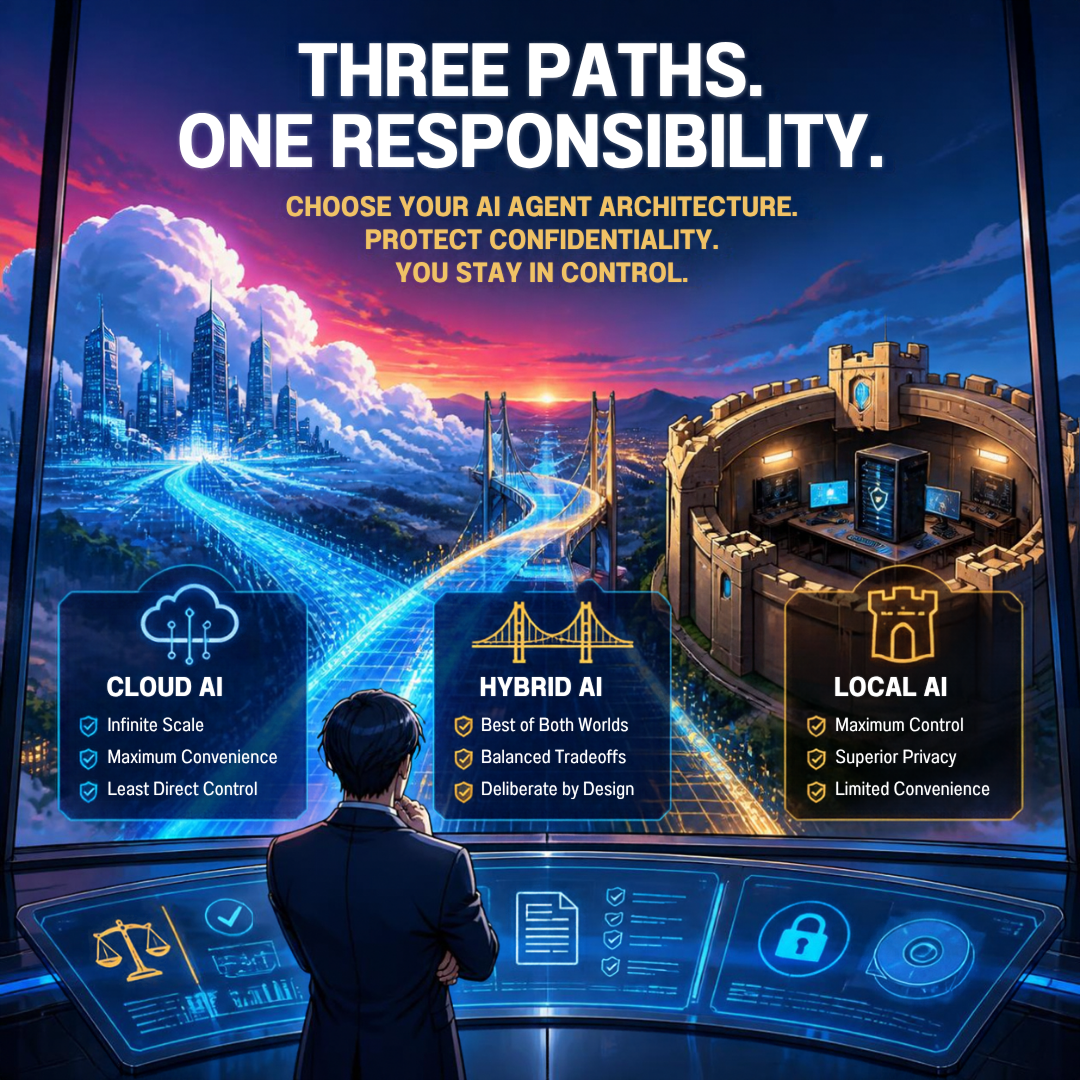
This is where the conversation gets practical. In MTC: Should Lawyers Host Their Own AI (or Hybrid AI)?, I explained that Opinion 512 neither requires nor forbids self-hosting. The main advantage of local or hybrid AI is control. You decide where client data lives and which files and apps the AI can reach. A dedicated, sandboxed Mac mini can be kept separate from your primary network and cloud storage, with access limited to selected folders.

Compare that architecture with a consumer agent on your everyday Mac. The cloud agent's reach is broad by design. Its "memory" of you lives on someone else's servers. Its training and retention policies can change. The self-hosted model's reach is whatever you allow. Nothing leaves the box unless you configure it to.

Self-hosting is not a magic shield, though. 🛡️ That same May editorial warned that firms unable to manage patches, access controls, backups, and audit logs may increase their risk by going local. A well-vetted cloud provider with strong contractual commitments may be the safer choice for some solos.

The same caution applies at the smallest scale. My guide, HOW TO: How Lawyers Can Run a Private Local LLM on a Smartphone: A Practical, Ethical Guide 📱🔒, explains that "local" may describe only the text-generation engine. Web search, cloud backup, and third-party integrations can quietly change the privacy analysis. Local models are also smaller and less capable. A hallucinated case does not become real because it was hallucinated on your own hardware.

The honest comparison looks like this:

  • Cloud personal agents 🌐 offer the most capability and convenience. They also carry the broadest access, the greatest vendor dependence, and the largest prompt-injection exposure.

  • Self-hosted or sandboxed agents 🏠 offer the most control and auditability. They demand real technical discipline and accept some loss of capability.

  • Hybrid setups 🔀 often fit best. Routine, sanitized work goes to vetted cloud tools. Sensitive matters stay on controlled hardware.

A Practical Checklist Before You Click "Allow" ✅

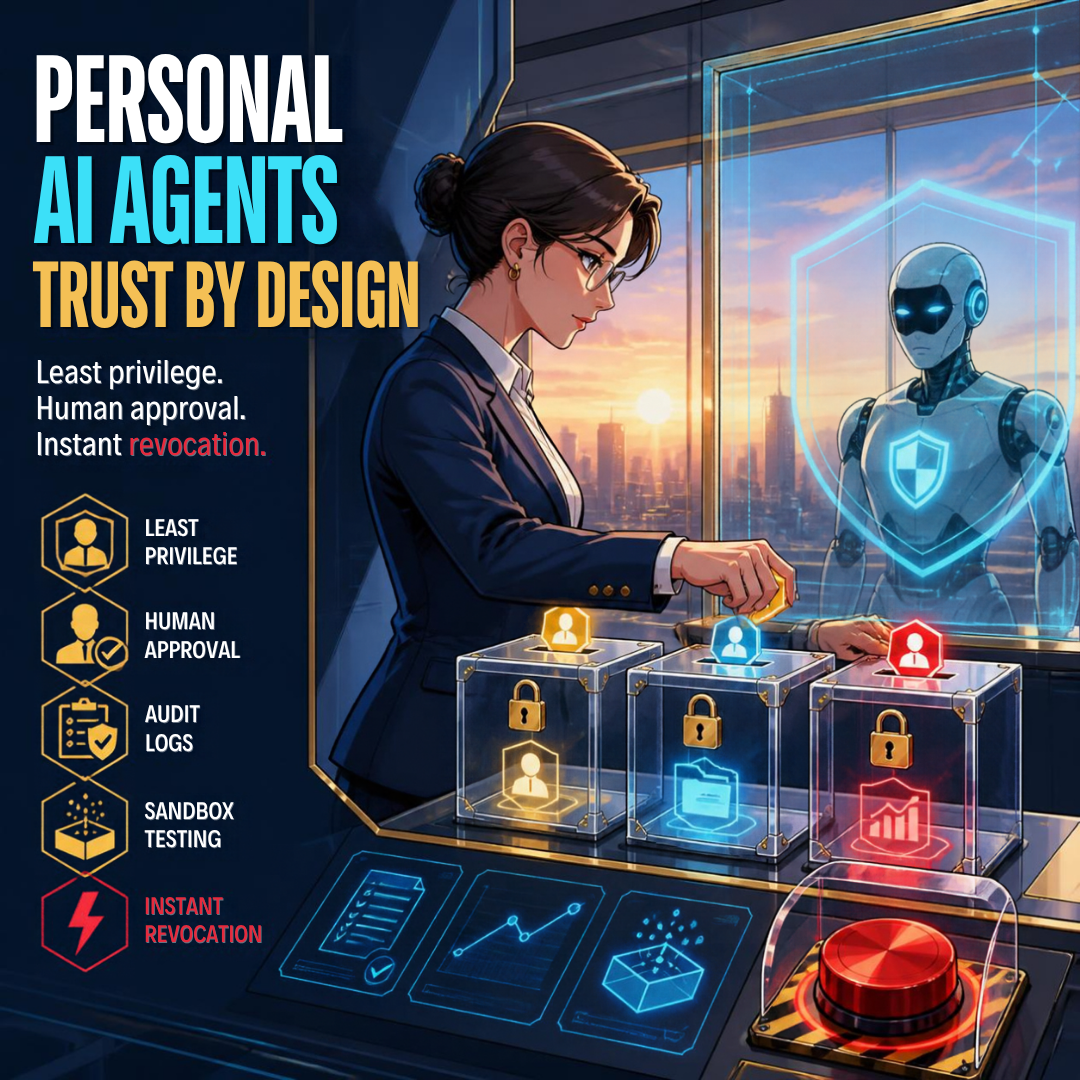
  • Never grant Full Disk Access to a consumer AI agent on the computer that holds client files.

  • Test agents on a separate machine or user account with dummy data first.

  • Grant least-privilege access by app and by folder, not by disk.

  • Require human approval before any email, upload, form submission, or payment.

  • Confirm you can review activity logs and revoke access instantly.

  • Put it in a written AI policy and train your staff on it.

The Bottom Line 🎯

AI Automation Meets Legal Ethics: Supervision, Privacy, and Control!

Apple's warning may be self-interested. It is also correct. Muse, Spark, and Dots are impressive tools, and they will get better. But a lawyer's computer is not an ordinary consumer device. It is a vault of other people's secrets. Before you hand any agent the keys, whether it lives in Meta's cloud, Google's cloud, or a Mac mini under your desk, make sure you can answer three questions. What can it see? What can it do? Who answers for it? Under the ABA Model Rules, the answer to the last question is always you. ⚖️

Happy Lawyering! 😊

MTC!

🚨 BOLO: Chrome Security Update: Law Firms Should Patch Before Browsing Again 🚨

lawyers keep your work secure, update your softwarE - update your google chrome browser now!

Solo practitioners and small firms should make updating Google Chrome a same-day task. Malwarebytes reports that Chrome’s current desktop update includes 327 security fixes, including 10 critical vulnerabilities, and that certain flaws can be triggered simply by visiting a malicious website. For a law practice handling confidential client communications, privileged work product, and sensitive financial data, that is a risk worth addressing immediately.

Chrome’s stable release has been updated to version 152.0.7977.64/.65 for Windows and Mac, and 152.0.7977.64 for Linux. The update addresses, among other issues, a critical flaw in ANGLE, Chrome’s graphics translation component, identified as CVE-2026-79282. Malwarebytes says a remote attacker could exploit that flaw through a crafted web page to execute arbitrary code outside Chrome’s browser sandbox.

That phrase—“outside the sandbox”—matters. Browser sandboxing is designed to contain web content so that a malicious site cannot easily reach the rest of the computer. A flaw that permits code execution beyond that boundary can give an attacker a path from a single web visit to the underlying operating system. That is precisely the sort of exposure lawyers should avoid when working in a browser alongside client portals, email, cloud document systems, court filing platforms, banking tools, and AI services. ⚖️

The update also remediates CVE-2026-78899, a use-after-free vulnerability in Chrome’s V8 JavaScript engine. It has a reported CVSS score of 8.8 out of 10. Even though successful exploitation occurs inside the browser sandbox, it should not be dismissed. Attackers frequently combine vulnerabilities in a chain, using one weakness to gain an initial foothold and another to widen access.

Why this is a legal-ethics issue!

its a team effort - remind your fellow lawyers to update their chrome browser today!

Technology hygiene is no longer separate from professional responsibility. ABA Model Rule 1.1 requires competent representation, and Comment 8 specifically calls on lawyers to keep abreast of “the benefits and risks associated with relevant technology.” A lawyer does not need to become a cybersecurity engineer. But maintaining a reasonably secure browser—the primary doorway to modern legal work—is a basic and manageable safeguard.

Model Rule 1.6(c) is equally relevant. It requires lawyers to make reasonable efforts to prevent unauthorized access to, or inadvertent disclosure of, client information. An unpatched browser can become an avoidable weak point in that effort. A compromised browser session could expose client documents, credentials, confidential messages, cloud-storage access, or data entered into web forms. 🔐

For firms, this update is also a reminder to think beyond the individual lawyer’s device. Rule 5.1 requires partners and managers to make reasonable efforts to ensure that firm-wide practices conform to professional obligations. Rule 5.3 similarly requires appropriate oversight of nonlawyer assistants. In practical terms, that means someone should own the checklist: browser updates, operating-system patches, password-manager deployment, multifactor authentication, and employee awareness.

Update Chrome now

On a Windows or Mac computer:

  1. Open Chrome.

  2. Select the three-dot More menu in the upper-right corner.

  3. Choose Settings.

  4. Select About Chrome.

  5. Allow Chrome to download any available update.

  6. Restart the browser to complete installation. 🔄

Chrome typically updates itself, but automatic updates can lag when the browser remains open for days, a restart is postponed, or an extension interferes with the update process. Malwarebytes specifically notes that manually checking can ensure the update is applied rather than merely downloaded.

This is a two-minute task with a potentially significant payoff. Before opening that unfamiliar link, reviewing a shared file, or logging into a client-facing platform, take a moment to confirm that Chrome is current. Security is not a one-time purchase or a single policy document. It is a set of small, repeatable habits that protect the practice and the people who trust it.

Bottom line: update Chrome, restart it, and encourage everyone in your firm to do the same today. ✅

MTC: When Your Phone's "Self-Destruct" Button Becomes a Federal Crime: Duress Passwords, Spoliation & the Duty to Preserve ⚖️📱

lawyers should know the interplay among Duress Passcodes, Border Searches, and Smartphone Evidence Destruction

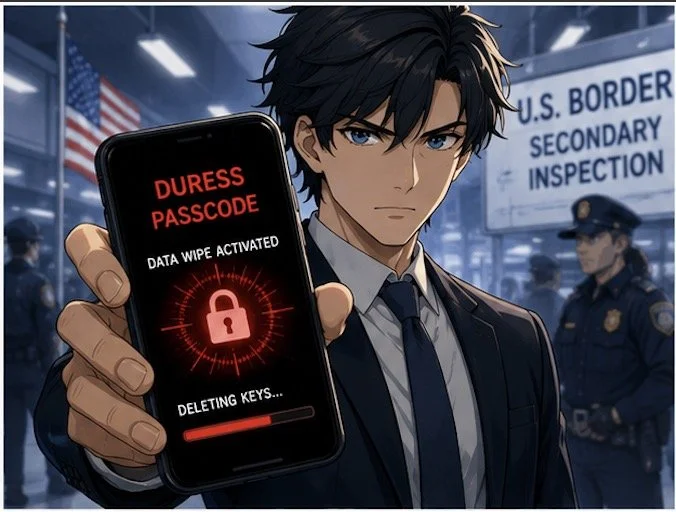
The Justice Department just indicted an Atlanta man for handing border agents a "duress passcode" that wiped his phone during a secondary inspection. It's believed to be the first prosecution of its kind — and it should put every lawyer (and every client with a smartphone) on notice. 🔔

"Duress passwords" — sometimes called "panic codes" or "coercion PINs" — are a real feature in iOS, Android, and third-party privacy apps. Enter one code and the device unlocks normally. Enter the duress code and the phone quietly obliterates its encryption keys, rendering the data unrecoverable. For journalists, activists, and anyone crossing borders with sensitive material, they're a shield. For prosecutors, they look like a loaded gun pointed at the evidence locker. 🔫💾

Here's where the professional-responsibility rubber meets the road. ABA Model Rule 3.4(a) makes it professional misconduct to "unlawfully obstruct another party's access to evidence or unlawfully alter, destroy or conceal a document or other material having potential evidentiary value." Comment 2 to Rule 3.4 clarifies that the duty attaches when a lawyer knows or reasonably should know that litigation is pending or reasonably foreseeable. A border inspection of a device you know contains responsive data? That's reasonably foreseeable. 📋

lawyers need to know the ABA Ethics Rules for Lawyers Protecting Digital Client Data!

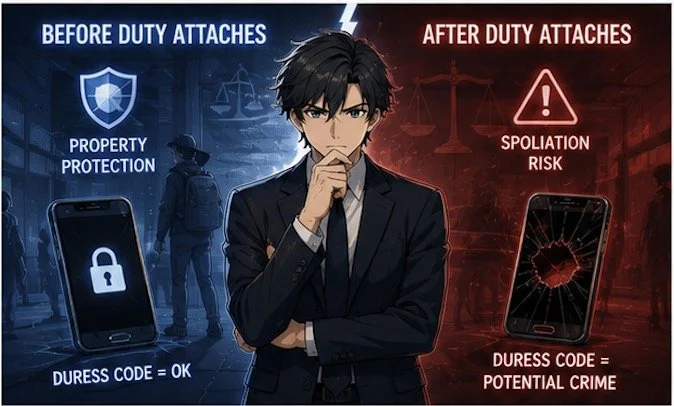
But Rule 1.15 (Safekeeping Property) and Rule 1.6 (Confidentiality) also impose affirmative duties to protect client data. A lawyer who carries privileged communications across a border has a genuine tension: the duty to preserve vs. the duty to safeguard. The duress password sits exactly on that fault line. If you trigger it before a preservation obligation attaches — say, because your phone is stolen — it's property protection. If you trigger it after a subpoena, a litigation hold, or a border detention you knew was coming, it's spoliation. 🧨

The line isn't always bright. Good-faith accident — dropping your phone in coffee, a toddler factory-resetting your iPad — is not a crime. But intent is inferred from circumstances: Did you enable the duress feature after learning of the investigation? Did you select the code specifically for the border crossing? Did you fail to issue a litigation hold to yourself? Courts draw adverse inferences from all three. 📉

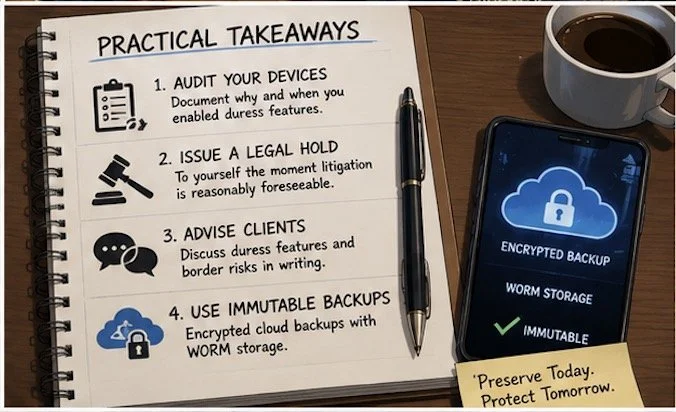
Practical takeaways for your practice:

1.      Audit your own devices now. If you use a duress feature, document why and when you enabled it — before any matter makes it suspect. 📝

2.     Issue written preservation notices to yourself the moment litigation is reasonably foreseeable.

3.     Advise clients in writing about duress features before they travel. A client who wipes a phone at the border because you never mentioned the risk creates a Rule 1.1 (Competence) and Rule 1.4 (Communication) problem for you. ✉️

4.     Use encrypted cloud backups with immutable retention (“WORM” [Write Once, Read Many] storage) so a local wipe doesn't equal total loss. That's preservation and property protection. ☁️🔒

what are the four takeaways lawyers should know when it comes to protecting client data at the boarder!

The Atlanta case will test whether providing a duress code to law enforcement is "destruction" under 18 U.S.C. § 1519 or the Federal Rules' spoliation doctrine. But you don't need the verdict to know your ethical north star: preservation obligations attach when you know — or should know — the data matters. The duress code doesn't suspend that duty; it just makes the violation faster and harder to detect. ⚡

Stay tech-savvy. Stay ethical. And maybe keep a spare phone in the carry-on or use a different phone specifically for travel. 🧳📱

MTC*

* Please remember this is an editorial not legal advice nor create an attorney-client relationship. You should contact an attorney for legal advice about your situation should the need arise.

🎙Bonus Episode: TSL Labs's 🧪 Deep Dive into our July 13, 2026, Editorial, Law School, Laptops, and AI: Why Banning Computers Misses the Point!

Join us for an AI-powered deep dive into the ethical challenges facing legal professionals in the age of generative AI. 🤖 In this episode, we unpack our editorial “Law School, Laptops and AI: Why Banning Computers Misses the Point,” and explore why laptop bans in law schools are less about ethics and more about administrative convenience — and how that choice could leave future lawyers unprepared for a fully digital profession.

In our conversation, we cover the following

00:00:00 — From “no calculators” to “no laptops”: how old tech panics mirror today’s AI fears in legal education 📚🧮

00:01:00 — AI panic hits law schools: blanket bans on generative AI and even laptops in the classroom 🎓⚠️

00:02:00 — Why Michael supports limiting AI in 1L while still opposing laptop bans: building foundational legal judgment 💪⚖️

00:03:00 — ABA Model Rule 1.1 and competence: why early overreliance on AI short-circuits “intellectual muscle” 🧠

00:05:00 — Why banning laptops “misses the point”: the scalpel vs leeches analogy and modern legal training 🩺🖥️

00:06:00 — Accessibility and fairness: Michael’s 2002 law school story and laptops as essential accessibility tools ✍️💻

00:07:00 — Digital-native students and analog exams: how bans unfairly shift the playing field instead of leveling it 🎯

00:08:00 — Law practice is 100% digital: e‑discovery, e‑filing, and why stripping laptops undermines tech competence 🌐📑

00:08:30 — ABA Model Rule 1.1, Comment 8: the ethical duty to understand the benefits and risks of relevant technology 📘

00:09:30 — Lazy enforcement: why laptop bans are about visual policing, not thoughtful AI policy 🧍‍♂️👀

00:10:00 — ABA Model Rule 5.3: supervising AI as a “digital clerk” and why hiding the tech creates ethical gaps 🤖📎

00:11:30 — Guardrails, not prohibitions: network geofencing, offline laptops, and locked‑down software environments 🧱📶

00:12:30 — Clear AI policies in assignments: when AI is permitted, when it is prohibited, and how disclosure builds discipline 📝

00:13:00 — Teaching prompt engineering as a core legal skill: delegation, context, and structured AI use 🧩

00:13:30 — ABA Model Rule 1.6 and confidentiality: the risks of pasting client secrets into public AI tools 🔐

00:14:30 — Cognitive offloading vs cognitive atrophy: why tech can strengthen legal reasoning when used wisely 🧠⚙️

00:16:00 — Verifying AI outputs: hallucinations, fake cases, and training students to check everything against primary law 📚

00:17:00 — Temptation vs discipline: why bans don’t teach judgment, but supervised AI use can 🎯

00:18:00 — The false dichotomy: foundational human judgment vs tech competence and why future lawyers must have both ⚖️💡

00:19:00 — The future horizon: when AI becomes the “senior partner” and the lawyer becomes the supervisor‑in‑chief 🧑‍⚖️🤖

00:20:00 — Final challenge: law schools can’t ban their way out of the future — they have to teach students to wield the tools safely 🔍🚀

RESOURCES

Mentioned in the episode

Software & Cloud Services mentioned in the conversation

If you care about the future of legal education, client protection, and real‑world tech competence, hit play now and then share this episode with a colleague who still thinks “just ban the laptops” is a solution. 🎧💬

MTC: Summer Vacation Cybersecurity for Lawyers: Essential Tech Tips to Protect Client Data on the Go 🌴💻

Lawyers: Never Skip Your VPN — Even on Vacation!

For many lawyers, “summer vacation” now means answering client emails from the beach house, reviewing drafts on the cabin deck, and jumping into Zoom hearings from hotel rooms. 🌞📶 Work rarely stays at the office, and our laptops and phones have become permanent carry‑ons even when we swear we are taking real time off. That always‑on reality turns every summer trip into a rolling cybersecurity and ethics test.

When you travel with devices that touch client matters, you are also traveling with privileged information, trade secrets, and personal data that fall squarely under ABA Model Rules 1.1 and 1.6. Competent representation now includes understanding the benefits and risks of the tech you use, and reasonable efforts to protect client confidentiality do not pause when you turn on your out‑of‑office message. The goal is not to shame lawyers for working on vacation; it is to make sure that when you inevitably do, your tech setup supports both your ethics and your relaxation. 😎

Pack Light: A “Minimum Data” Mindset for Vacation

The safest client data is the data that never leaves your office or your secure cloud in the first place. 1Password’s travel guidance and broader cybersecurity advice emphasize carrying only what you truly need when you hit the road. For summer trips, this translates into a deliberate “minimum data” mindset.

Before you leave, decide which matters genuinely might need your attention while you are away and which can safely wait until you return. Archive or unsync closed files and non‑urgent matters from your travel devices so they are not riding along to the resort, rental home, or national park lodge. For some practices, this may not be feasible when your current work may rely on prior drafts in similar cases.  But when feasible, consider using a “travel profile” or even a separate, cleaner laptop with access only to essential tools and a limited subset of client documents.

This approach directly supports your duty under Model Rule 1.6(c) to make reasonable efforts to prevent unauthorized access to client information by reducing the amount of sensitive material that could be exposed if a device is lost, stolen, or inspected. It also makes vacation feel less like moving your entire office to a different ZIP code, allowing you to focus on what really needs to be done and hopefully enjoy your vacation a little more.

Smart Lawyers Activate Travel Mode Before Every Flight.

Password Managers and Travel Mode: Your “Vacation Vault”

Strong, unique passwords are non‑negotiable for lawyers, and summer vacation does not change that. 1Password and similar tools exist precisely so you do not reuse easy‑to‑type passwords while you juggle boarding passes, sunscreen, and kids at the gate. (Note: I am a paying user of 1Password and have used their product for many years!  Also, I may earn a commission on any link used from this blog.)

Use a reputable password manager to generate and store complex, unique passwords for all your accounts—email, practice management, cloud storage, airlines, hotels, and rental car services. Store digital copies of your ID, bar card, and key travel documents in a secure vault instead of leaving them scattered across your inbox or photo roll. That saves time on the road and keeps sensitive personal and professional information encrypted.

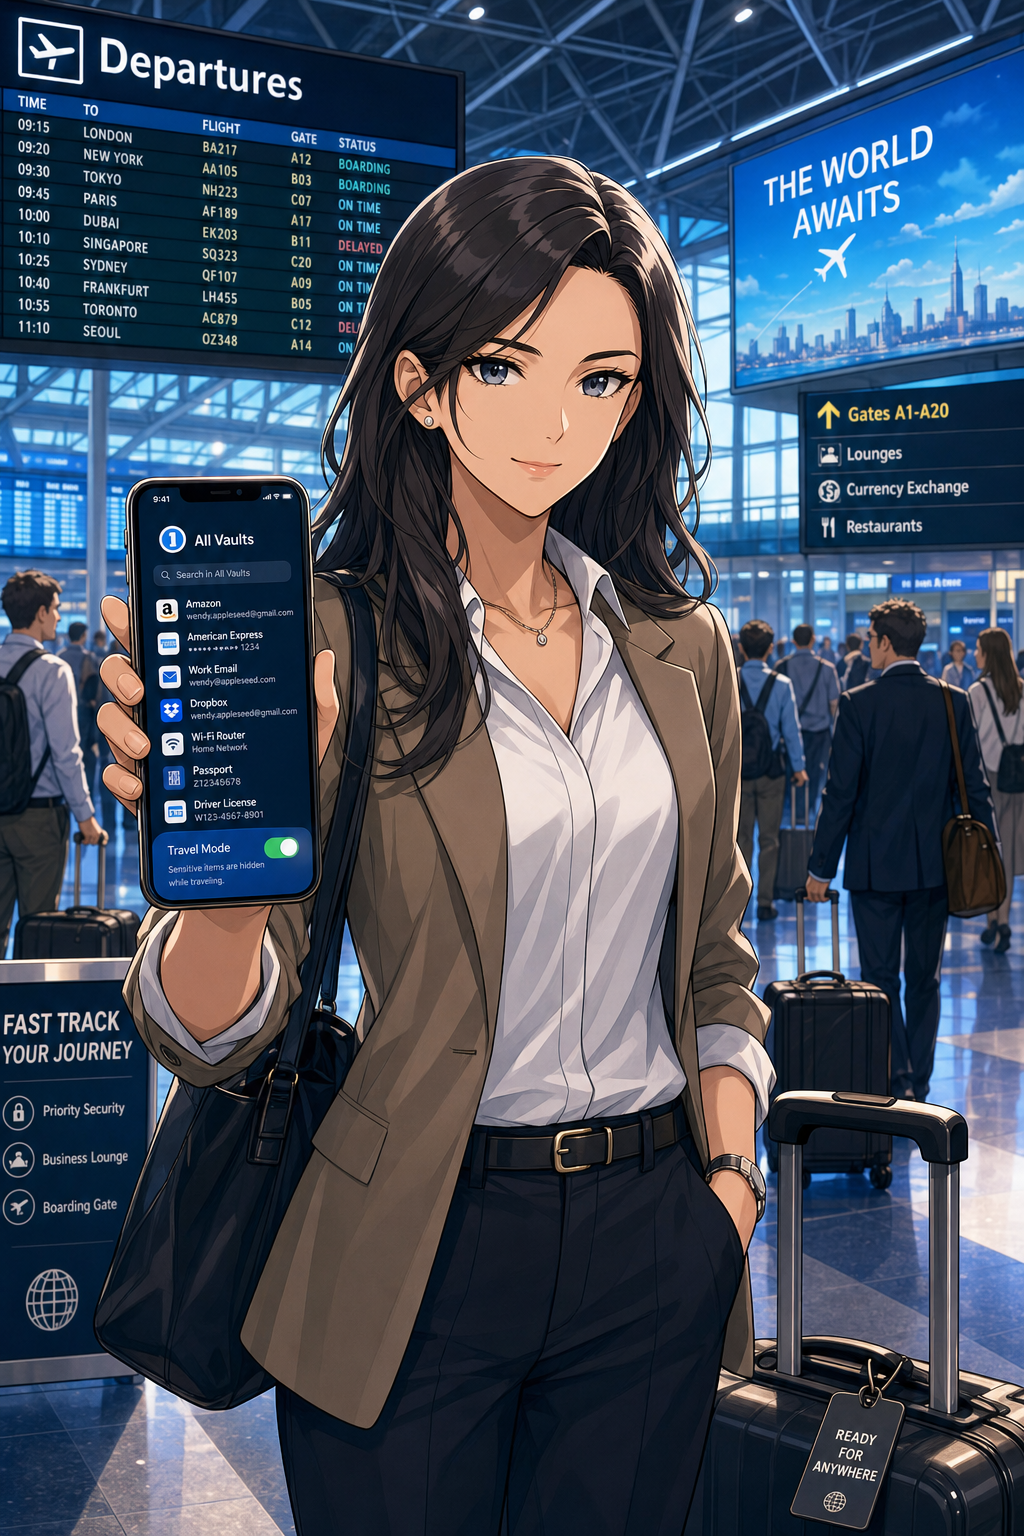
For summer travel, 1Password’s Travel Mode is particularly valuable. You can mark certain vaults as “safe for travel” and remove more sensitive vaults from your devices with a single toggle before you leave. If your phone or laptop is inspected at a border or compromised in a crowded tourist spot, the most sensitive client logins and documents are simply not there. From an ethics perspective, that is a concrete, defensible step toward preserving client confidentiality.

Vacation Wi‑Fi, VPNs, and Hotspots: Don’t Trust the Beach House Network

The Wi‑Fi at your beach rental, resort, or lakeside Airbnb may be convenient, but it is rarely secure. Past guests often know the password, routers may be poorly configured, and attackers sometimes target popular tourist areas with rogue access points. For lawyers who are logging into email, document systems, or court platforms from these networks, that is a serious problem.

Secure Client Data Anywhere — Use Your Phone's Hotspot!

A Virtual Private Network (VPN) should be standard equipment for any lawyer working on vacation. A good VPN encrypts your traffic between your device and the VPN provider, making it much harder for eavesdroppers or compromised networks to capture sensitive information. Legal tech sources and security professionals consistently recommend that lawyers use reputable VPN providers with strong encryption and clear no‑logs policies.

In practice, treat any shared vacation Wi‑Fi as hostile. Turn on your VPN before accessing client email, cloud storage, or remote desktop tools. Better yet, follow The Tech‑Savvy Lawyer’s advice and rely on your smartphone’s hotspot for truly sensitive work; modern cellular networks often provide stronger encryption and a more reliable, if not many times faster, performance than hotel or rental Wi‑Fi. This level of care is rapidly becoming part of what “reasonable efforts” and basic technology competence mean for a traveling lawyer.

Device Hardening for Summer Travel: Encryption, Passcodes, and Biometrics

Summer travel is chaotic. Devices slide between airplane seat cushions, get forgotten in rideshares, or are grabbed from café tables. Full‑disk encryption and strong authentication are your last lines of defense when something goes wrong.

Know Your Rights when crossing international boarders: Encrypted Devices Protect Client Privilege

Make sure full‑disk encryption is enabled on every device you bring—FileVault on macOS, BitLocker on Windows, and built‑in encryption on modern iOS and Android devices. Use a long, alphanumeric passcode rather than a short PIN, and configure automatic locking after a brief period of inactivity so a phone left by the pool does not stay unlocked.

When you are approaching international borders, consider temporarily disabling biometrics so that unlocking your device requires a passcode instead of a fingerprint or facial scan. 1Password’s Travel Mode can again help by ensuring that the most sensitive client vaults are not present on the device at all if a border search occurs. If agents request access, clearly state that the device contains privileged material and that you are an attorney, in line with guidance that privilege should trigger additional care. These steps show you are actively trying to protect client confidentiality, not ignoring the issue.

Two-Factor Authentication and Account Hygiene on Holiday

Account compromise can ruin a vacation as quickly as a lost suitcase. Enable two‑factor authentication (2FA) on your critical accounts—email, practice management, document repositories, and your password manager—before you leave. App‑based authenticators and hardware keys are generally more reliable and secure than SMS codes, especially when you are roaming internationally or in areas with spotty service.

Review account recovery options in advance so that a locked‑out account does not turn into an emergency while you are halfway around the world. Monitor sign‑in alerts from your major accounts during and after the trip so you can quickly respond to any unfamiliar activity. This sort of “account hygiene” supports your duties of competence and confidentiality and gives you practical peace of mind while you try to enjoy some downtime.

A Simple Summer Travel Checklist for Lawyers

For lawyers with limited to moderate tech skills, the key is a repeatable routine rather than a complex security project. A short checklist before each summer trip can go a long way:

Every Traveling Lawyer should use a Pre-Trip Security Checklist!

  • Backup all devices, apply pending updates, and confirm full‑disk encryption is enabled.

  • Clean your devices by removing non‑essential client data and logging out of unused accounts.

  • Configure your password manager, mark travel‑safe vaults, and turn on Travel Mode if available.

  • Install and test your VPN, and verify you know how to enable your phone’s hotspot.

  • Confirm 2FA works from where you will be, especially if traveling abroad.

This checklist supports the ABA’s technology competence expectations and makes your vacations less stressful because you are not improvising security on hotel Wi‑Fi at midnight. It respects the reality that today’s lawyers must often take their work—and their devices—with them, while still honoring their core obligations to clients.

Summer is supposed to be restorative. With a bit of planning, smart use of tools like VPNs and 1Password’s Travel Mode, and an eye on your Model Rule duties, you can protect client data and your own peace of mind at the same time. 🌴🔐

Save Travels!!! 🌴💼✈️

MTC

TSL Labs 🧪 Bonus: Deep Dive on our April 27, 2026, Editorial, MTC: Smart Recording, Client Secrets, and HeyPocket: What Every Lawyer Needs to Know in 2026 📱⚖️

📌 To Busy to Read This Week’s Editorial?

Join us for an AI-powered deep dive into the ethical challenges facing legal professionals in the age of generative AI. 🤖 In this episode, we unpack how AI note takers and “always-listening” devices can quietly route client secrets to third-party vendors, why that matters under the ABA Model Rules, and how a 2026 federal decision out of the Southern District of New York turned one defendant’s AI chats into discoverable evidence. Whether you are a solo practitioner, in-house counsel, or a tech-curious professional in another field, this conversation will help you balance convenience with confidentiality and avoid turning your favorite AI assistant into your biggest evidentiary risk.

👉 Before your next client meeting, listen to this episode, check out our editorial, and run your current AI tools through the checklist we outline—then subscribe and share with a colleague who is still “just trusting the app.” 🎧

In our conversation, we cover the following:

  • 00:00 – The “ambient microphone” problem: phones, smart speakers, wearables, and connected cars as a continuous surveillance layer around client conversations.

  • 01:00 – How technology competence has shifted from locking file cabinets to understanding data custody, cloud routing, and API-driven services.

  • 02:30 – What makes AI note takers like HeyPocket different from passive telemetry and why capturing the spoken “payload” changes the threat model.

  • 04:00 – The invisible “third party in the room”: routing privileged audio through external AI models and the malpractice risk of default “Allow” clicks.

  • 05:30 – Applying ABA Model Rules 1.1 and 1.6 to AI workflows: competence, confidentiality, and “reasonable efforts” in a world of automated transcription.

  • 07:00 – Risk-based analysis from ABA Formal Opinions 477R and 498: weighing sensitivity, likelihood of disclosure, and available safeguards before using AI.

  • 08:30 – Why secretly recording clients or opponents with AI tools can implicate Rule 8.4(c), even in one‑party consent jurisdictions.

  • 10:00 – Inside United States v. Heppner (SDNY 2026): how public generative AI platforms destroyed privilege and work-product protections for a criminal defendant.

  • 12:00 – How AI training and tokenization work, why “military‑grade encryption” does not save privilege if terms of service allow internal data use.

  • 14:00 – Treating every AI note taker like an outsourced e‑discovery vendor: NDAs, retention policies, security audits, and data destruction timelines.

  • 16:00 – Practical minimization strategies: defaulting to no recording, segmenting AI-generated content by matter, and restricting access via role‑based controls.

  • 17:30 – Establishing bright-line “no‑AI” categories (criminal defense, internal investigations, sensitive family/immigration, high‑value trade secrets).

  • 18:30 – Counseling clients not to “prep their case” with public chatbots after Heppner and why this is now part of competent representation.

  • 19:30 – Building a simple vendor-vetting checklist for law firms and professional practices adopting AI note takers.

  • 20:00 – Looking ahead: when failure to use secure, vetted AI may itself become a competence issue due to inefficiency and overbilling.

  • 21:00 – Rethinking privilege in a world where an algorithmic “third party” is always in the room and devices are never truly off

RESOURCES

Mentioned in the episode

📖 Word of the Week: “Cross‑Tenant” Learning in Legal Practice

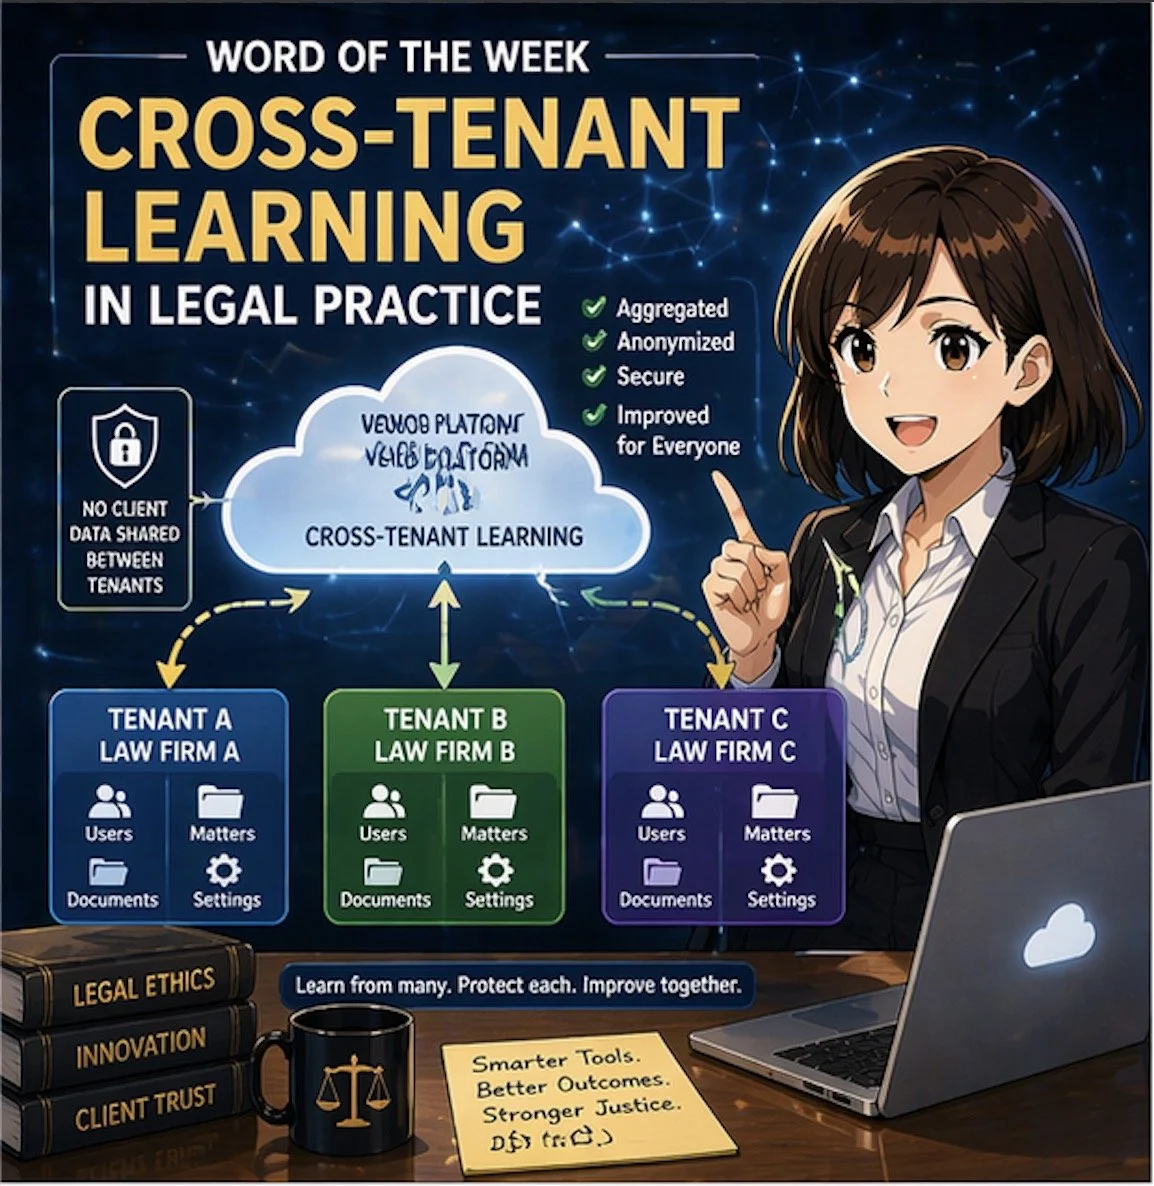
Cross-tenant learning helps law firms improve AI tools without exposing data

If your firm uses cloud‑based tools, you are already living in a multi‑tenant world. In that world, cross‑tenant learning is quickly becoming a key concept that every lawyer and legal operations professional should understand. 🧠⚖️

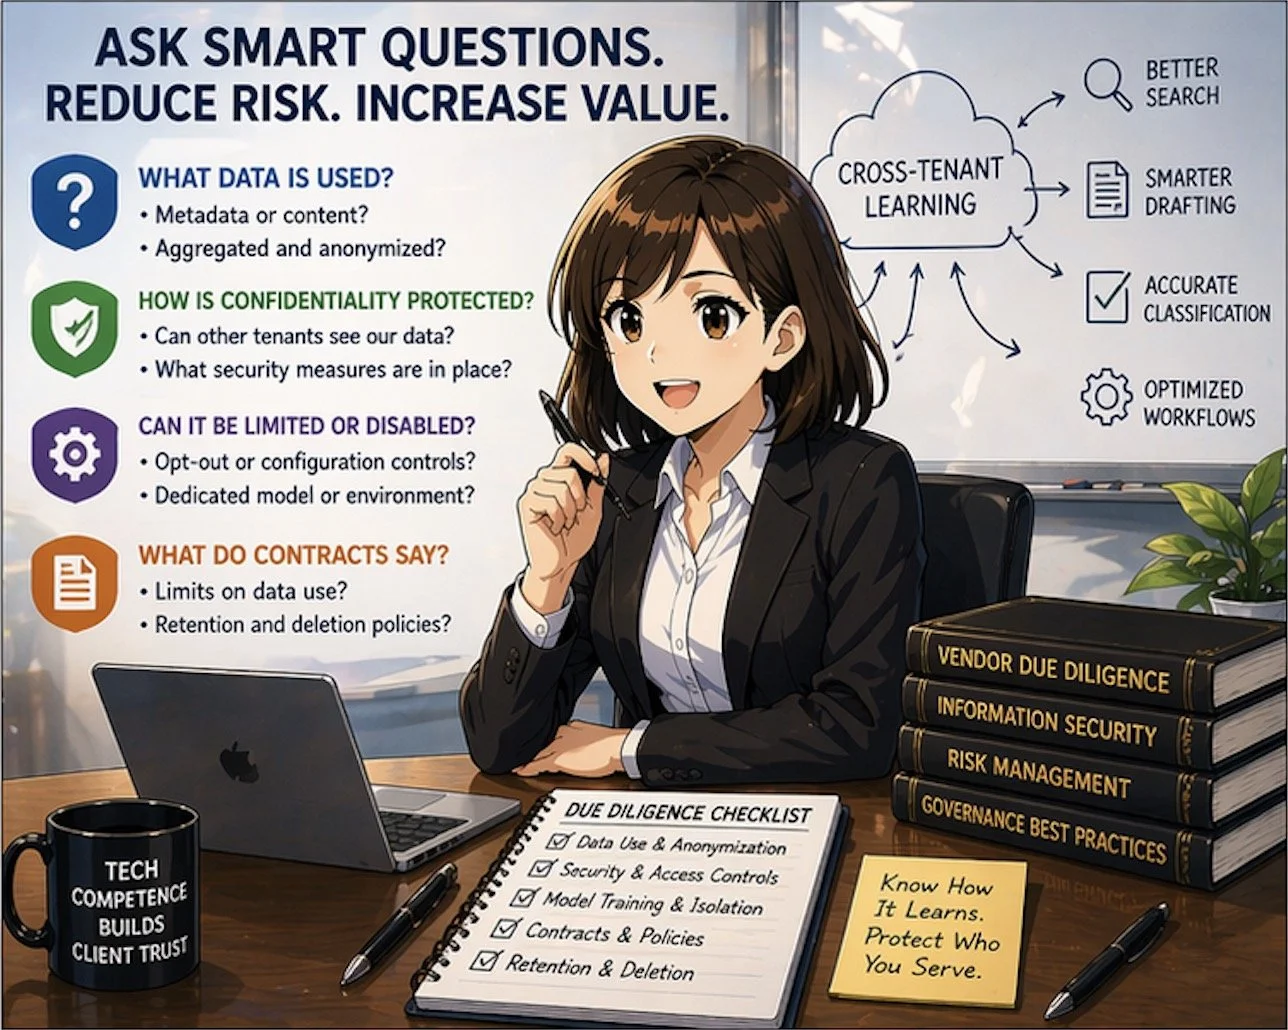
In simple terms, a “tenant” is your firm’s logically separate space inside a cloud platform: your own users, matters, documents, and settings, isolated from everyone else’s. Cross‑tenant learning refers to techniques in which a vendor’s system learns from patterns across multiple tenants (for example, many law firms) to improve its features—such as search, drafting suggestions, or document classification—without exposing any other firm’s confidential data to you or yours to them.

Why cross‑tenant learning matters for law firms

Cross‑tenant learning is especially relevant as generative AI and machine‑learning tools become embedded in e‑discovery platforms, contract review tools, legal research systems, and practice‑management software. Vendors may use aggregated and anonymized usage data to:

  • Improve relevance of search results and recommendations.

  • Enhance clause and issue spotting in contracts and briefs.

  • Reduce false positives in e‑discovery or compliance alerts.

  • Optimize workflows based on how similar firms use the product.

For lawyers, the value proposition is straightforward: your tools can become “smarter” faster, based on lessons learned across many organizations, not just your own firm’s experience. Done properly, cross‑tenant learning can raise the baseline quality and efficiency of technology available to your practice. ⚙️📈

ABA Model Rules: Confidentiality and Competence

Any discussion of cross‑tenant learning for law firms must start with confidentiality and competence.

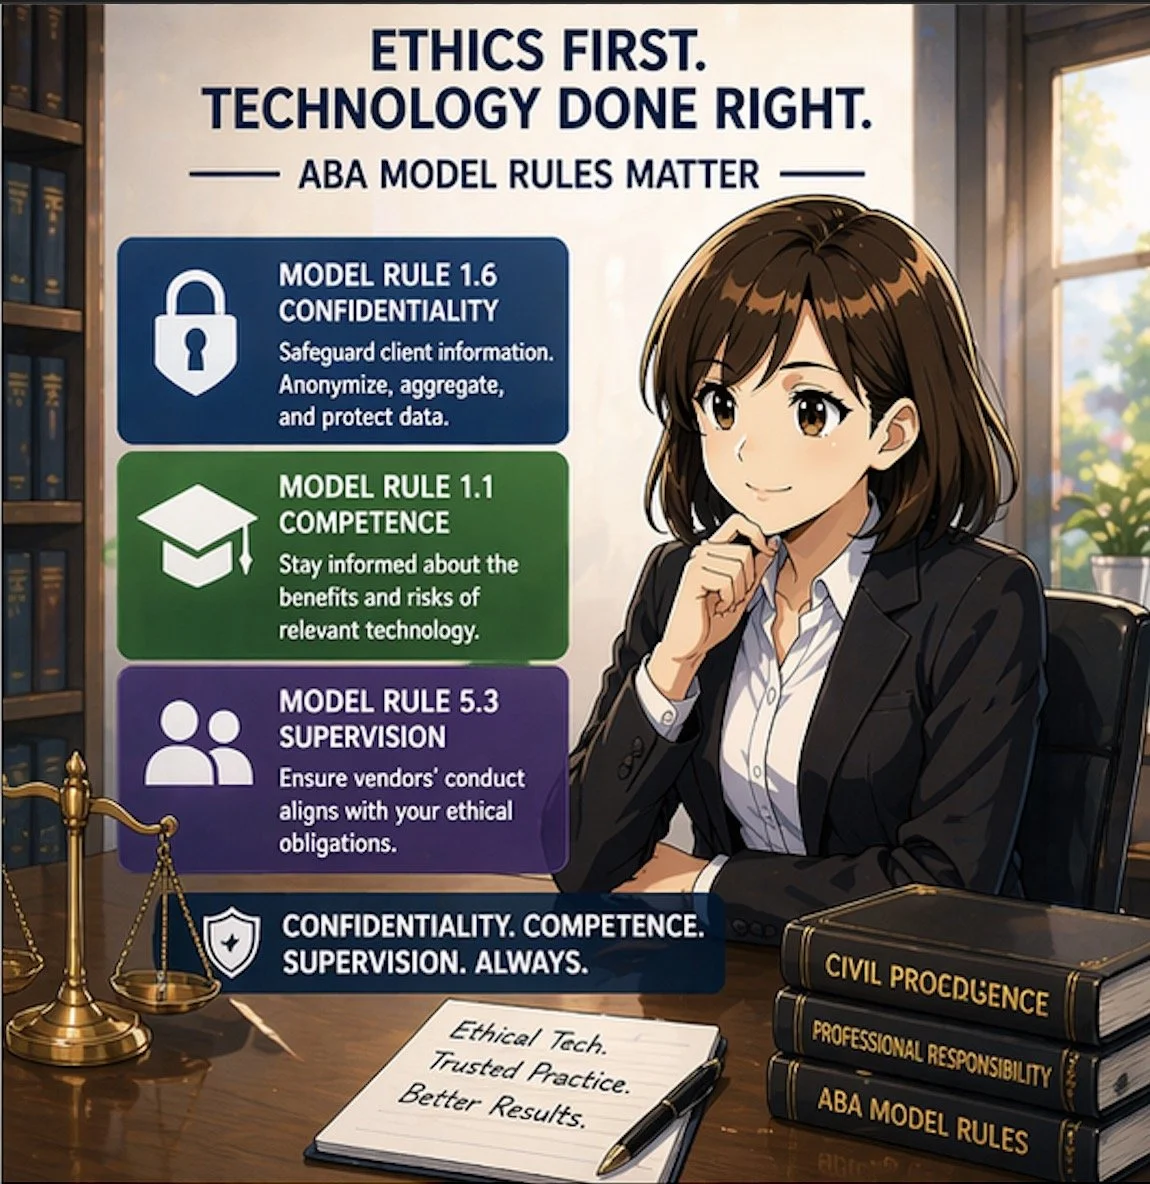
  • Model Rule 1.6 (Confidentiality of Information) requires lawyers to safeguard information relating to the representation of a client. That obligation extends to how your vendors collect, store, and use your data. You must understand whether and how client data may be used for cross‑tenant learning and ensure that any such use preserves confidentiality through anonymization, aggregation, and strong technical and contractual controls. 🔐

  • Model Rule 1.1 (Competence), including Comment 8, emphasizes that lawyers should keep abreast of the benefits and risks associated with relevant technology. Understanding cross‑tenant learning is now part of that duty. You do not need to become a data scientist, but you should be comfortable asking vendors precise questions and recognizing red flags.

  • Model Rule 5.3 (Responsibilities Regarding Nonlawyer Assistance) applies when you rely on vendors as nonlawyer assistants. You must make reasonable efforts to ensure that their conduct is compatible with your professional obligations, including how they use your data for cross‑tenant learning. 🧾

Key questions to ask your vendors

ABA Model Rules guide ethical use of cross-tenant learning technologies

When evaluating a product that relies on cross‑tenant learning, consider asking:

  1. What data is used?

    • Is it only metadata or usage logs, or are actual document contents included?

    • Is the data aggregated and anonymized before it is used to train shared models?

  1. How is confidentiality protected?

    • Can other tenants ever see prompts, documents, or client‑identifying information from our firm?

    • What technical measures (encryption, access controls, tenant isolation) are in place?

  1. Can cross‑tenant learning be limited or disabled?

    • Do we have opt‑out or configuration controls?

    • Is there a dedicated model or environment for our firm if needed?

  1. What do the contract and policies say?

    • Does the MSA or DPA clearly limit use of client data to defined purposes?

    • How long is data retained, and how is it deleted if we leave?

These questions are not merely IT concerns; they go directly to your obligations under the ABA Model Rules and your firm’s risk profile.

Practical examples in law practice

Consider a cloud‑based contract‑analysis platform used by hundreds of firms. Over time, the provider can see which clauses lawyers routinely flag as risky, which edits are typically made, and what becomes the “preferred” language for certain issues. Through cross‑tenant learning, the system can use that aggregated knowledge to highlight problematic clauses and suggest alternatives more accurately for everyone.

Another example is an e‑discovery platform that uses cross‑tenant learning to distinguish between truly relevant documents and common “noise” such as automatically generated emails. The more matters the system processes across different tenants, the better it gets at ranking documents and reducing review burdens. This can be a material efficiency gain for litigation teams. ⚖️💼

In both scenarios, your ethical comfort depends on whether underlying data is appropriately anonymized, compartmentalized, and contractually protected.

Governance steps for your firm

To align cross‑tenant learning with professional obligations, firms can:

  • Update vendor‑due‑diligence checklists to include explicit questions about cross‑tenant learning, training data use, and model isolation.

  • Involve a cross‑functional team—lawyers, IT, information security, and risk management—in vendor selection and review.

  • Document your analysis of vendor practices and how they satisfy confidentiality, competence, and supervision obligations under the ABA Model Rules.

  • Educate lawyers and staff about how AI‑enabled tools work, what kinds of data they send into the system, and how to avoid unnecessary exposure of client‑identifying details.

Takeaway for busy practitioners

Smart vendor questions reduce risk in cross-tenant legal technology adoption

You do not need to reject cross‑tenant learning to protect your clients. Instead, you should approach it as a powerful capability that demands informed oversight. When well‑implemented, cross‑tenant learning can help your firm deliver faster, more consistent, and more cost‑effective legal services, while still honoring confidentiality and ethical duties. When poorly explained or loosely governed, it becomes an unnecessary and avoidable risk.

Understanding how your tools learn—and from whom—is now part of competent, modern legal practice. ⚖️💡

BOLO: Gone (Almost) Phishin’: What a Sophisticated Apple Scam Teaches Lawyers About Cybersecurity, Client Confidentiality, and ABA Ethical Duties 🚨📱

Lawyers Face Sophisticated Apple Phishing Scam Cybersecurity Risks!

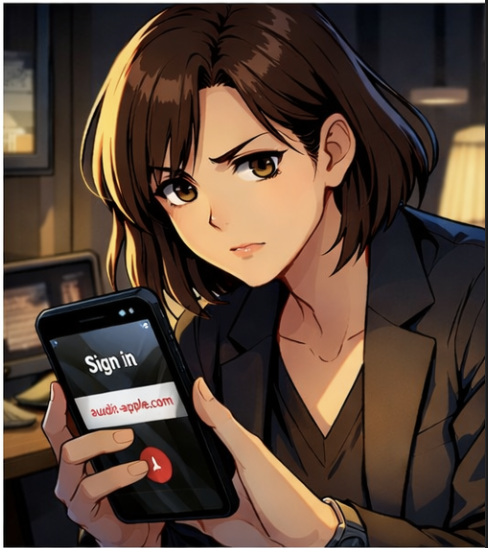
A recent real‑world phishing attempt against a well‑known technology CEO offers an important warning for lawyers and law firms about how modern scams now convincingly mimic “legitimate” security workflows. This attack did not rely on laughable grammar, obvious fake domains, or clumsy social engineering; instead, it weaponized Apple’s genuine password‑reset system, real support case IDs, and realistic phone support to try to compromise the victim’s Apple ID. For lawyers who increasingly rely on mobile devices, cloud services, and multi‑factor authentication for client communications, this kind of scam is not hypothetical—it's a direct threat to client confidentiality and professional responsibility.

In the incident, the victim’s Apple Watch, iPhone, and Mac all began displaying unexpected prompts to reset the Apple ID password, despite the user running Apple’s Lockdown Mode on all devices. The prompts were not generated by malware on the devices, but by an attacker repeatedly triggering Apple’s legitimate password reset flow, thereby flooding the user with authentic-looking notifications. From the perspective of a busy lawyer, such prompts might be dismissed as an annoyance or, worse, acted upon in haste. Either reaction, without careful verification, can create risk. 📲

The scam escalated when the attacker called, posing as “Alexander from Apple Support,” referencing a real Apple support case that they had opened themselves by impersonating the victim. Because Apple’s own systems generated a valid case ID and corresponding emails, the communications appeared fully authentic; no spam filter or “phishing awareness” toolbar would have flagged them as suspicious. The caller began with correct, even prudent, security advice—check your account, verify nothing has changed, consider updating your password—which is precisely the kind of guidance many lawyers expect from legitimate support channels. This blend of real security language with a fraudulent goal is what makes the scam so dangerous. 🧠

Phishing Lessons for Lawyers Using Apple Devices and Cloud Tools!

The critical moment came when “Alexander” sent a text with a link to “audit-apple.com,” a pixel‑perfect imitation of Apple’s site that displayed the real case ID and even a fake transcript of the attackers’ prior “chat” with Apple. At the bottom of the page sat a “Sign in with Apple” button, intended to harvest the victim’s credentials under the guise of closing a fraudulent request. Only after poking at the site and noticing that any case ID produced the same result did the victim confirm it was a scam and confront the attacker. Many lawyers, particularly those with only moderate comfort with technology, might not test the site this way and could be persuaded by the case ID and realistic presentation. 🕵️‍♂️

For legal professionals, the ethical implications are significant. ABA Model Rule 1.1 on competence requires lawyers to understand the benefits and risks associated with relevant technology, including the ability to recognize and respond to sophisticated phishing. The duty of confidentiality under Rule 1.6 requires taking reasonable steps to prevent unauthorized access to client information, which includes protecting accounts and devices that store or access client files, email, and messaging. If a lawyer’s Apple ID or similar account is compromised, attackers may gain access to privileged communications, document repositories, calendar entries, and even secure messaging apps that sync via the device.

Model Rule 5.3 extends these obligations to nonlawyer assistants, including staff and outside vendors who may handle client data or access firm systems. If partners and associates are vulnerable to such scams, staff and contractors are as well; firm leadership must implement policies, training, and incident‑response procedures that recognize the new generation of phishing where everything “looks right” until you inspect the URL or underlying flow. This aligns with recognized best practices: anti‑phishing training, simulated phishing exercises, and clear escalation paths for suspicious security communications.

Key practical lessons for lawyers from this incident include:

  • Do not approve unexpected password‑reset prompts; instead, go directly to your device or account settings via a known‑good path (e.g., Settings → Apple ID on your device).

  • Treat unsolicited “support” calls with extreme skepticism, even when they reference real case IDs or recent activity; major vendors like Apple will not call you out of the blue to fix a security issue.

  • Always verify the URL before entering credentials; for Apple, support should live on apple.com or getsupport.apple.com, not look‑alike domains.

  • Establish a firm‑wide rule: no one—IT, vendors, or support—will ever ask for passwords, one‑time codes, or sign‑in via a link sent in an unsolicited message; any such request must be verified through a separate, trusted channel.

Apple Scam Warning for Lawyers Protecting Client Confidentiality

From an ethical‑risk perspective, a successful attack of this kind could trigger duties to notify clients, insurers, and regulators, depending on your jurisdiction’s breach‑notification regime and professional‑conduct rules. Even an “almost‑breach,” like the one described in this article, is a valuable opportunity for firms to revisit incident‑response plans, document what would happen if a lawyer’s Apple ID or smartphone were compromised, and rehearse the steps for containing damage. Doing so not only supports compliance with Model Rules 1.1 and 1.6 but also demonstrates to clients and courts that the firm takes cybersecurity governance seriously. ✅

The story also underscores that even highly technical users can be momentarily convinced by a well‑crafted scam, which should encourage humility rather than embarrassment among lawyers who worry they are “not technical enough.” The correct response is not shame, but systems: layered security controls, clear verification procedures, and regular training that turn individual vigilance into institutional resilience. Ultimately, as phishing attacks become more sophisticated and exploit real security workflows, lawyers must elevate their cybersecurity awareness to meet their ethical obligations and preserve the trust at the core of the attorney‑client relationship. 💼

📰 ABA TECHSHOW 2026 Recap: From AI Hype to LLM Reality, Google Workspace, and Ethical Lawyering in the Age of Bots ⚖️🤖

The Real Story Behind ABA TECHSHOW 2026

The techshow is the conference to go to keep your pulse on the technology lawyers should be using every day!

Walking into ABA TECHSHOW 2026 this year, I wasn’t thinking about shiny gadgets; I was thinking about competence, client service, and what it will mean to practice law in an era dominated not just by “AI,” but by large language models (LLMs) quietly shaping almost everything we see and share online. During my work on The Tech-Savvy Lawyer.Page blog and podcast, I keep running into the same pattern: lawyers know they should understand legal technology, yet they worry they’ll break something, breach a rule, or look foolish in front of their staff. TECHSHOW 2026 aimed directly at that anxiety — but this year, the conversation needs to go beyond what AI and generative AI can do and toward how LLMs and search bots are already shaping our professional identities online and offline. ⚖️💻

Keynotes: The “AI Dividend” and Your Time

The keynote lineup captured the tension between promise and risk. Legal market analysts highlighted what some called the “AI Dividend”: when machines take over routine drafting and research, lawyers gain time to think, advise, and advocate at a higher level. The real question — one I’ve been hammering on The Tech-Savvy Lawyer.Page for years — is what you will do with the time technology gives back (some of that time should include reviewing your work, e.g., your case citations). Tech-savvy speakers pushed attendees to look past vendor hype and focus on the broader digital environment, where consumer-facing tools, search engines, and recommendation algorithms are setting new expectations for speed, transparency, and availability.

Practical AI in the Sessions

Inside the conference rooms, the “Taming the Machines” and related AI tracks met baseline concerns (some with hands-on workshops) focused on realistic use cases: assisted drafting, pattern spotting in discovery, and summarizing voluminous documents. These sessions were built for lawyers who live in Word, Outlook, Google Workspace, and practice management systems and who simply want to stop retyping the same paragraphs. The faculty hammered home a critical point: generative AI is an assistant, not a decision-maker; you remain the lawyer, responsible for accuracy, judgment, and ethics under the ABA Model Rules. 🤖📄

Google Workspace, Microsoft 365, and Using What You Already Own

Mathew Krebis’ session on Google Workspace drove that message home in very practical terms. He showed how many firms are only scratching the surface of tools they already pay for: shared Drives with well-structured permissions, real-time collaboration in Google Docs, Gmail automation for intake and follow-up, and Google Calendar combined with Tasks to keep matter timelines under control. When you layer in emerging AI features in Workspace — smart replies, document summaries, suggested outlines — you see how even modest use of these tools can dramatically reduce friction in daily practice, and the tools Mathew discussed are not isolated to “law practice management” systems.

The takeaway was powerful: before you chase a new platform, fully exploit the ecosystem you already have. For many firms, “being more tech-savvy” starts with properly configuring their Google Workspace, Microsoft 365, or other SaaS platform, rather than buying yet another service.

Podcasting, Social Media, and LLM-Driven Visibility

Meanwhile, one other yet important frontier — and one that still feels underexplored — is what happens when LLMs and search bots become the primary lens through which clients, colleagues, and even opposing counsel discover you. That’s where my panel, 🎧 Podcasting for Lawyers: The Truth Behind the Mic, came in.

Ruby L. Powers, Gyi Tsakalakis, Stephanie Everett, and I discussed podcasting and social media not just as marketing channels, but as structured signals fed into LLM-driven engines that are constantly indexing, ranking, and inferring who is an authority on a given topic. Whether you talk about appellate practice, family law, or even a hobby outside the law, your content becomes training data for Generative Engine Optimization/LLM bots that decide which voices surface first when someone types a question into an AI chatbox. 🎙️🌐

In other words, your digital footprint is no longer static. It is being interpreted, reassembled, and presented as answers — often without you ever seeing the intermediate steps. That reality raises a new layer of ethical questions under the ABA Model Rules. Model Rule 7.1’s prohibition on false or misleading communications about the lawyer or the lawyer’s services takes on a new twist when LLMs remix snippets of your posts, podcasts, Google Workspace–hosted client alerts, and blog articles into composite “advice.”

You might be scrupulously accurate in your content, but if an LLM mischaracterizes it or presents it out of context, what then? TECHSHOW 2026 addressed traditional risks like hallucinated case citations, but there is room for a deeper, explicit conversation about how LLM-driven discovery intersects with advertising, communication, and competence duties.

EXPO Hall: Tools, Timekeeping, and Vendor Reality Checks

The EXPO Hall, as always, served as a laboratory of possibilities. Practice management platforms, billing tools, document automation, and a wave of AI-enhanced products competed for attention. Timekeeping tools that automatically capture activity across devices and applications and then propose draft time entries have grown dramatically since last year. For lawyers still reconstructing their days from memory and sticky notes, this is more than a marginal upgrade; it directly affects revenue, work-life balance, and accuracy.

But the fair warning comes here: make sure vendors are showing you what their product can do today, not what they hope it will do someday. In the LLM era, marketing decks are often several steps ahead of deployed reality. 🧾⏱️

Remember, you have an obligation under Model Rule 1.1 (competence) and Model Rule 5.3 (responsibilities regarding non-lawyer assistance) to understand the capabilities and limitations of any tech you “delegate” work to. Asking hard questions about current functionality, data handling, and audit trails is not being difficult; it is part of your duty of care.

Cybersecurity, Confidentiality, and LLM Risk

networking oppOrtunities like the taste of tecHshow” is a great way to talk with and learn from other lawyers about using tech in the practice of law.

The sessions on cybersecurity and confidentiality continued to do vital work. Under Model Rule 1.6, our obligation to protect client information extends to cloud storage, email, video conferencing, and the mobile devices we casually use in airport lounges. The “Guardians of the Data” track walked through practical checklists rather than abstract fearmongering: password managers, multi-factor authentication, properly configured backups, and vendor due diligence.

For firms running on Google Workspace, that translated into concrete steps: enforcing two-step verification, tightening Drive sharing settings, using client-specific shared Drives instead of ad hoc personal folders, and monitoring admin logs for suspicious access. The move from generic “AI” to LLM-powered services on any platform increases data risk, because many tools rely on ingesting your content — sometimes including client information — to improve their models. If you don’t understand where your data is going and how it is used, you cannot credibly say you are meeting confidentiality obligations. 🔐☁️

Competence, Human-in-the-Loop, and Everyday Workflows

You have an obligation under Model Rule 1.1 (competence) and Model Rule 5.3 (responsibilities regarding non-lawyer assistance) to understand the capabilities and limitations of any tech you “delegate” work to. Asking hard questions about current functionality, data handling, and audit trails is part of your duty of care.

Balancing this skepticism, though, is an equally important truth: becoming proficient with AI and LLM-based tools is not a spectator sport. You cannot satisfy your duty of technological competence from the sidelines. You have to use the tools first on a small scale, then progressively in more critical workflows, always with appropriate supervision and verification.

That might mean piloting an AI drafting feature in Google Docs and Microsoft Word for internal templates, or testing structured intake forms and automations inside Google Workspace or Microsoft 365 before rolling them out firm-wide. Ignoring AI because it feels uncomfortable is no longer the safer option. In some practices, failing to integrate it intelligently — while peers and opposing counsel do — may itself raise competence concerns as expectations evolve in courts and among clients. 🧩📈

Saturday Sessions: From “Use AI” to “Use AI Responsibly”

On Saturday, the 9 a.m. conversation among ABA President Michelle A. Behnke, Immediate Past President William R. “Bill” Bay, and President-Elect Barbara J. Howard, underscored how all of this ties into the rule of law and access to justice, framing AI as something lawyers now have a responsibility to actually use, not simply watch from the sidelines. The 10 a.m. session with Judge Timothy S. Driscoll then shifted the focus from “use AI or be left behind” to “use AI responsibly,” making it clear that judges, too, are integrating AI into their work and that they are not immune from mistakes when they rely on it.

The message for everyone in the courtroom ecosystem was simple and blunt: “Review, review, and review” any work touched by AI, because AI is a non‑infallible tool that does make errors and can mislead the unwary. Together, these sessions acknowledged the growing digital divide: lawyers and clients who can’t or won’t adopt technology risk falling out of the mainstream of legal services, while those who adopt it recklessly risk eroding confidence in both their own work and the justice system as a whole.

We are not merely debating convenience; we are deciding who gets effective representation and who is left out because the lawyer they might have hired never appeared in their LLM‑driven search results — or appeared with AI‑boosted visibility but poor ethical judgment. Technology, in this sense, is not optional; it is one of the few levers we have to expand meaningful access to legal help, provided we wield it with intent, humility, and rigorous human review. ⚖️🧠

LLM Literacy: The Next Core Competency

That balance — between caution and experimentation — is where TECHSHOW 2026 both excelled and showed its next frontier. Many sessions made AI approachable, breaking down concepts for lawyers with limited to moderate tech skills and providing concrete workflows they could apply on Monday. What I would like to see more explicitly next year is programming that treats LLM literacy as a core competency: understanding how LLMs are built, how they index and surface information, how your content feeds into them, and how that affects everything from client intake to reputation, whether you are working in Microsoft 365, Google Workspace, or a specialized legal platform.

From my vantage point as a legal tech ambassador at The Tech-Savvy Lawyer, the most successful sessions respected that many lawyers are highly capable professionals who simply haven’t had the time or guidance to modernize their workflows. They don’t need to become prompt engineers. They need guardrails, roadmaps, and clear examples of how to align AI, LLM tools, and mainstream platforms like Microsoft 365 and Google Workspace with the ABA Model Rules and local bar guidance. When faculty focused on incremental steps — tightening cybersecurity configurations, adding a layer of AI-assisted drafting under strict human review, building a consistent content strategy that LLMs can reliably recognize — the room should lead in.

A Tough-Love Takeaway for Lawyers

If you are a lawyer who still feels behind, here’s the core message I took away from TECHSHOW 2026, with a bit of tough love: you don’t need to chase every new tool, but you can’t afford to ignore LLM-driven AI and the platforms you already live in, like Microsoft 365 and Google Workspace, any longer. Understand the basics; pilot one or two well-vetted tools to start improving your efficiency without sacrificing the need for a true human-in-the-loop.

SEE YOU IN CHICAGO FOR ABA TECHSHOW 2027!!!

Read your jurisdiction’s ethics opinions on AI and technology. Build habits that protect client data by default. Use your own content — whether blog posts, newsletters, or podcasts — to train the bots to see you as a trusted authority rather than a digital afterthought. Ultimately, your bar license may be at more risk from not engaging with AI than from engaging with it carefully and intelligently.

The future of legal practice will not wait until we are all comfortable; it is here now, embedded in the search boxes, recommendation engines, and tools your clients already use. TECHSHOW 2026 made that clear. The next move is yours. 🚀⚖️

MTC