
MTC: When Your Staff Leaves, Does Their Access Leave Too? 🔐 A SaaS Access Governance Checklist for Lawyers and Law Firms ⚖️
/
Law firms should Approve access deliberately and revoke risky permissions to protect client confidentiality.
Every law firm has a departure story. A paralegal moves on. A contract attorney finishes a document review. An associate shifts from litigation to transactional work. 👋 The farewell lunch happens. The laptop comes back. The email account gets shut off. Most firms call that "offboarding" and move on.
A recent 1Password* article, "SaaS access governance: Does access end when employees leave?," explains why that confidence is often misplaced. The piece is written for corporate IT teams. Its lessons apply with even greater force to lawyers. Our clients' confidential information lives in dozens of cloud tools, and our ethics rules do not accept "we thought IT handled it" as a defense.
The Problem: Access Outlives the Role 🚪
lawyers should Close the door on lingering SaaS access to protect every law-firm client.
The 1Password article makes a simple point. Disabling a person's main account does not remove every path back to your data. Many firms use a central login, often called single sign-on (SSO). Not every application connects to it. A former employee may still hold a working account in your e-signature platform, your file-sharing service, your project tracker, or an AI tool someone signed up for on a free trial.
Then there are the less visible doors. Shared credentials, personal accounts used for work, and OAuth connections can all survive a departure. OAuth is the "Sign in with Google" or "Allow this app to access your files" permission we click without much thought. Those permissions can persist until someone actively revokes them. 🔑
The article cites 1Password's 2025 Access-Trust Gap Report, which found that 38% of employees have successfully accessed a former employer's account. Read that number again. If it holds anywhere near true for law firms, client files may be one forgotten login away from exposure. 😬
Role changes create a quieter version of the same risk. The associate who moves practice groups keeps permissions from the old one. The contract lawyer keeps access to the shared workspace long after the engagement ends. Nobody acted improperly. Nobody looked at the full picture, either.
Why This Is an Ethics Issue, Not Just an IT Issue ⚖️
Track SaaS access activity to support law-firm audits and client-data protection.
The ABA Model Rules turn this operational gap into a professional responsibility question.
Rule 1.1 (Competence) and its Comment 8 require lawyers to keep abreast of the benefits and risks of relevant technology. Understanding who can reach your client data is part of that duty. 🧠
Rule 1.6(c) (Confidentiality) requires reasonable efforts to prevent unauthorized access to, or disclosure of, client information. A former staff member's live account in your document platform is precisely the kind of unauthorized access the rule contemplates. ABA Formal Opinion 477R reinforces that lawyers must understand how client information is transmitted and stored and must apply reasonable safeguards.
Rules 5.1 and 5.3 (Supervision) require firm managers to have measures in place that give reasonable assurance that lawyers and nonlawyers comply with professional obligations. An offboarding process that relies on memory is not a "measure." It is a hope. 📋
These supervisory duties now extend to AI tools. I discussed this in "My Two Cents: Lessons from ABA's Formal Opinion 512 - A Follow-Up!." If a staff member connected an AI application to your matter files, you need to know it exists. You also need to know when that connection ends.
The Five-Step Checklist, Translated for Law Firms ✅
The 1Password article offers five best practices. Here is how each one translates to a solo or small-to-midsize practice.
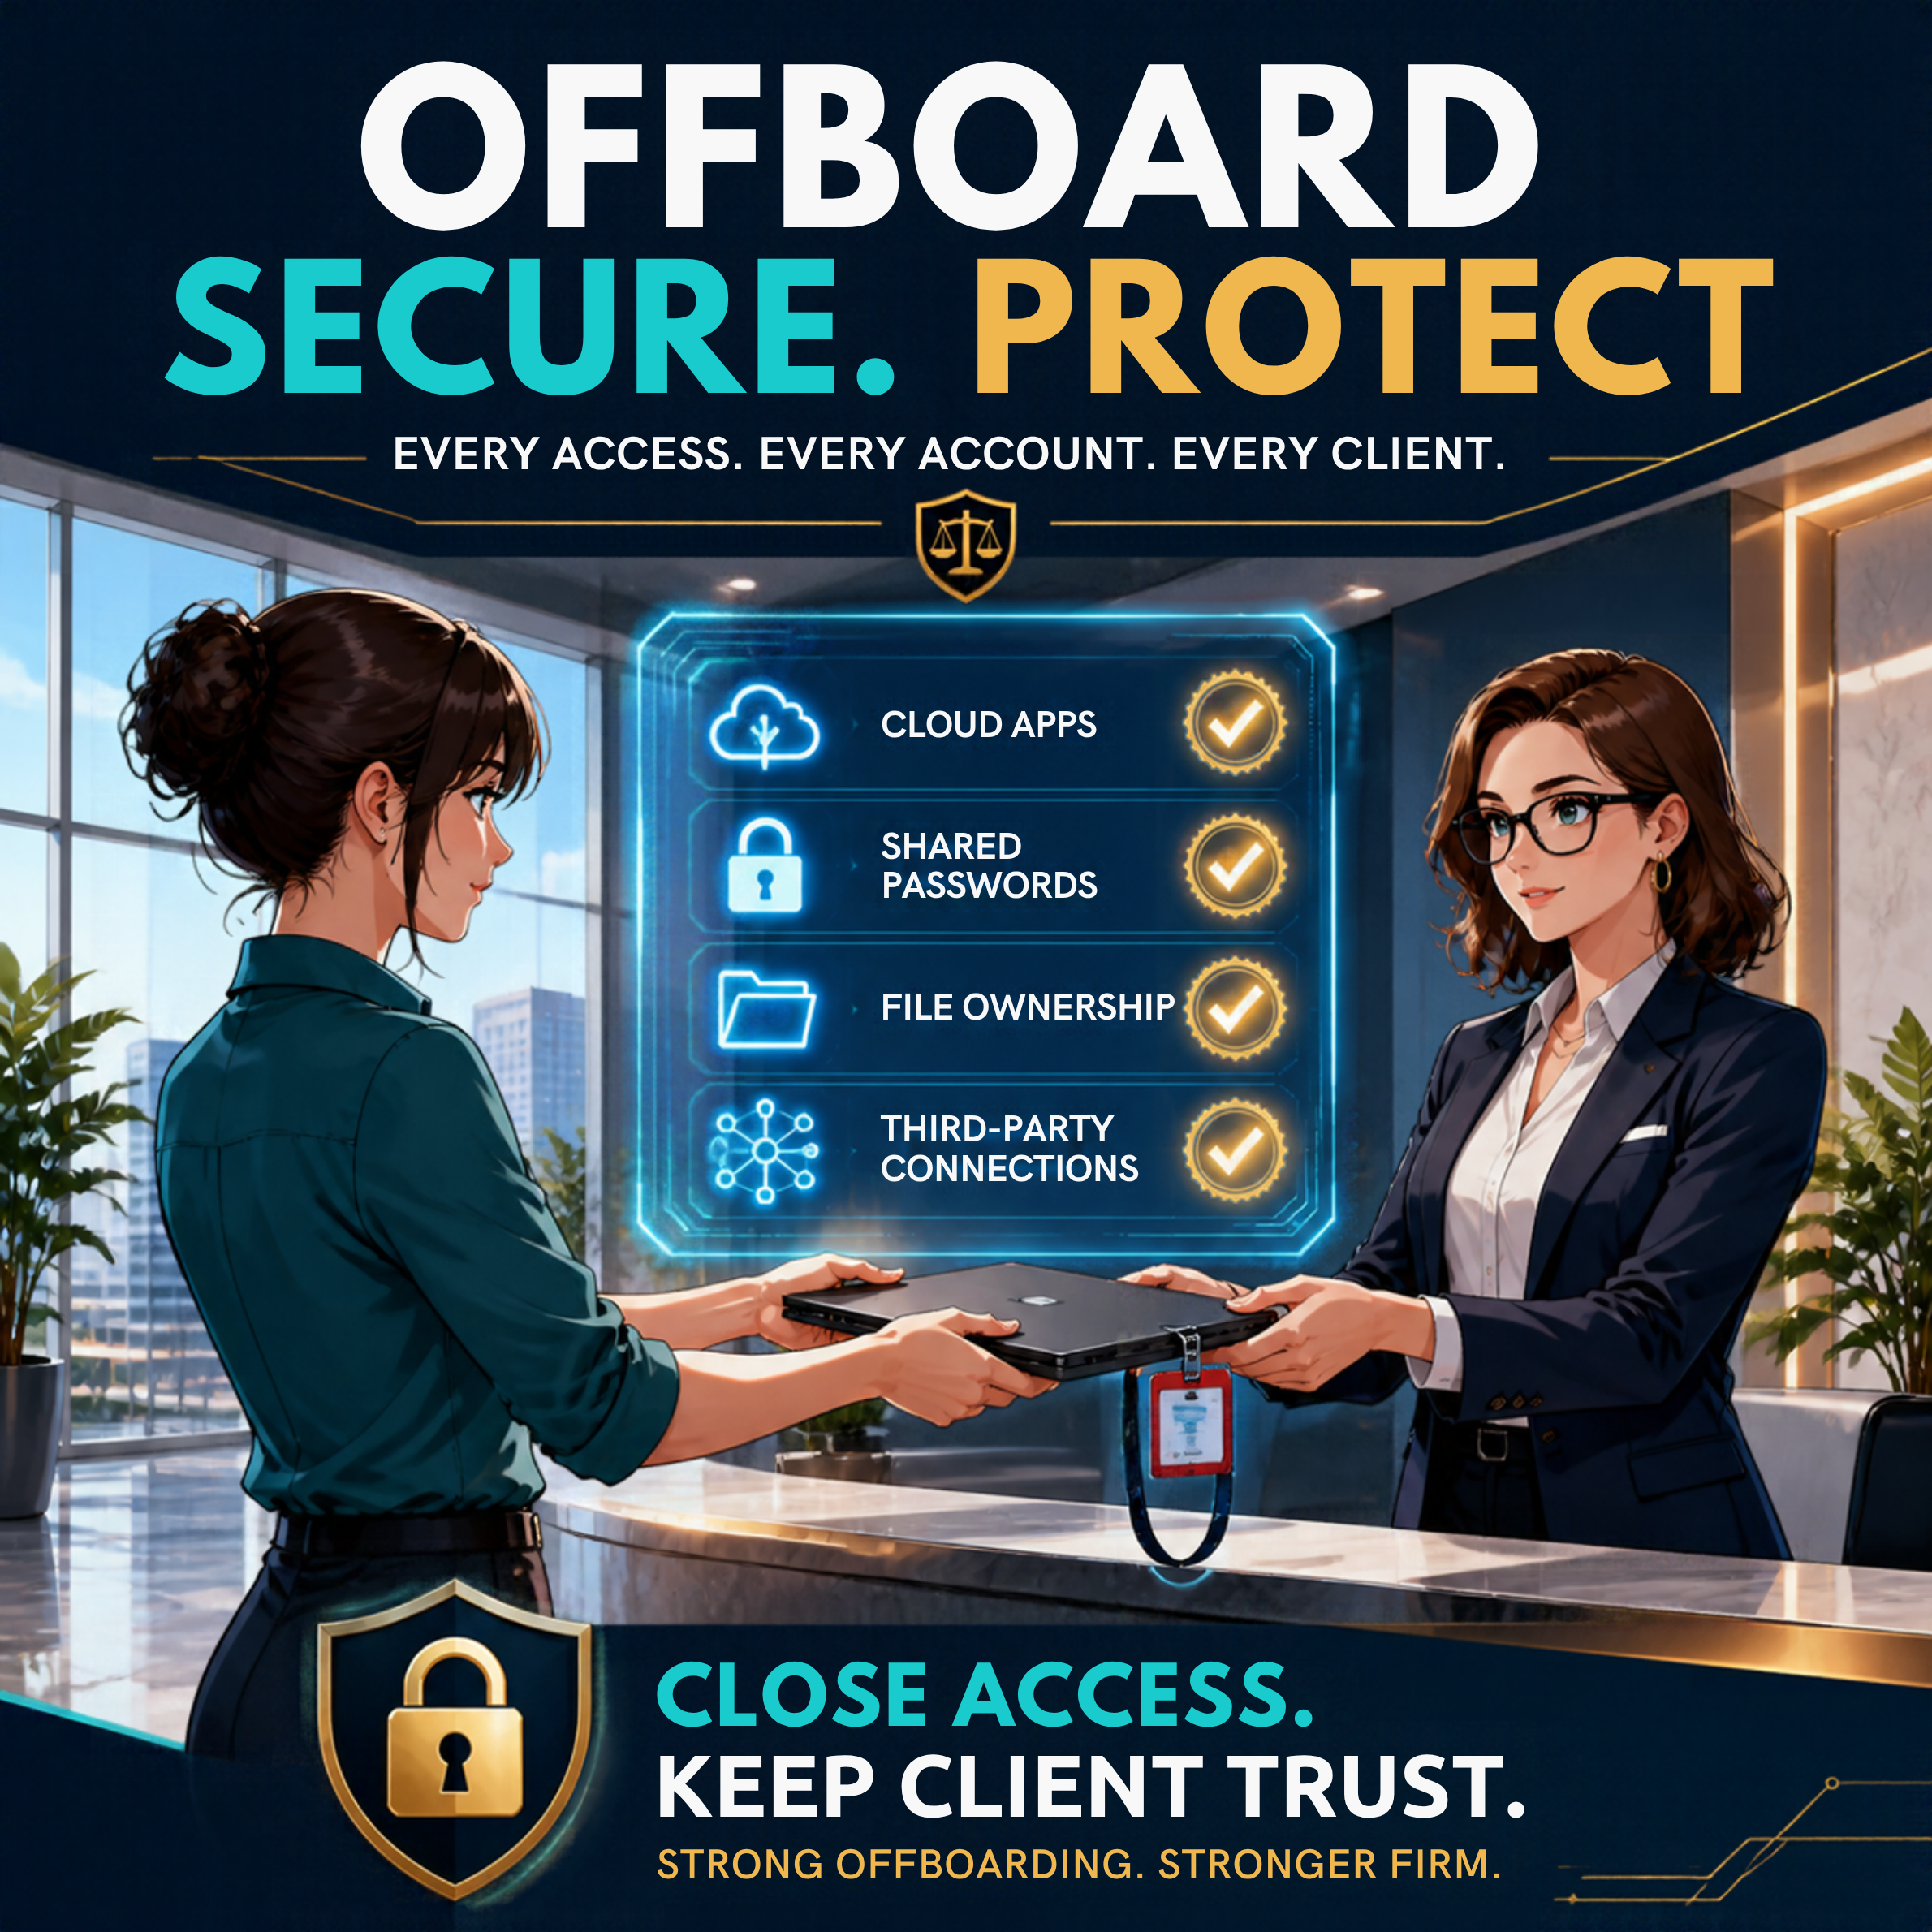
law firms should have A clear offboarding workflow to revoke SaaS access and protect law-firm clients.
1. Discover what your people actually use. 🔍 Build a simple inventory. List every application, shared login, and connected integration your firm relies on. Include tools adopted without formal approval. Ask your team directly. You will likely be surprised.
2. Tie access to lifecycle events. 🔄 Hiring, role changes, contract end dates, and departures should each trigger a written checklist. Assign an owner to every step. In a small firm, that owner may be you. Write it down anyway.
3. Apply least privilege when roles change. 🎯 Access should reflect current duties, not history. When someone moves from one practice area to another, remove the old permissions. I covered this principle in "📖 WORD OF THE WEEK (WoW): Zero Trust Architecture ⚖️🔐." The motto still applies: never trust, always verify.
4. Govern new SaaS and AI tools. 🤖 Create a clear way for staff to request new tools. Review what data each tool can reach before approving it. Assign an owner to every approved application. The 1Password article makes a point I strongly endorse: AI tools belong inside your broader software governance, not in a separate silo.
5. Verify removal and keep proof. 🧾 Offboarding is complete only when you can show access is gone from every relevant system. That means outside-SSO apps, OAuth connections, shared passwords, file ownership, and paid seats. Keep a short record of who closed each item and when. Use a second reviewer for departures involving privileged access. Then test the process periodically before a real departure tests it for you.
Practical Steps You Can Take This Week 🛠️
SaaS access governance helps law firms securely offboard users and protect client confidentiality.
You do not need an enterprise platform to start. A password manager with shared vaults lets you rotate credentials quickly when someone leaves. Most cloud platforms, including Microsoft 365 and Google Workspace, let administrators review and revoke third-party app connections. A one-page offboarding checklist, saved in your firm's policy folder, is a meaningful first step.
Larger firms may benefit from dedicated tools. 1Password promotes its SaaS Manager for discovery, automated provisioning, and OAuth revocation. As with any vendor, evaluate it under Rule 5.3 and your own risk profile. My earlier post, "My Two Cents: Essential Security and Privacy Reminder for Lawyers Using Cloud Software," offers a foundation for that review. 💡
My Two Cents 💭
MTC
* Product used by this blogger! This is not an endorsement per se, nor is this a guarantee of any kind. You still have an independent duty to review software before implementing it into your practice.