
🚨 BOLO: Chrome Security Update: Law Firms Should Patch Before Browsing Again 🚨
/
lawyers keep your work secure, update your softwarE - update your google chrome browser now!
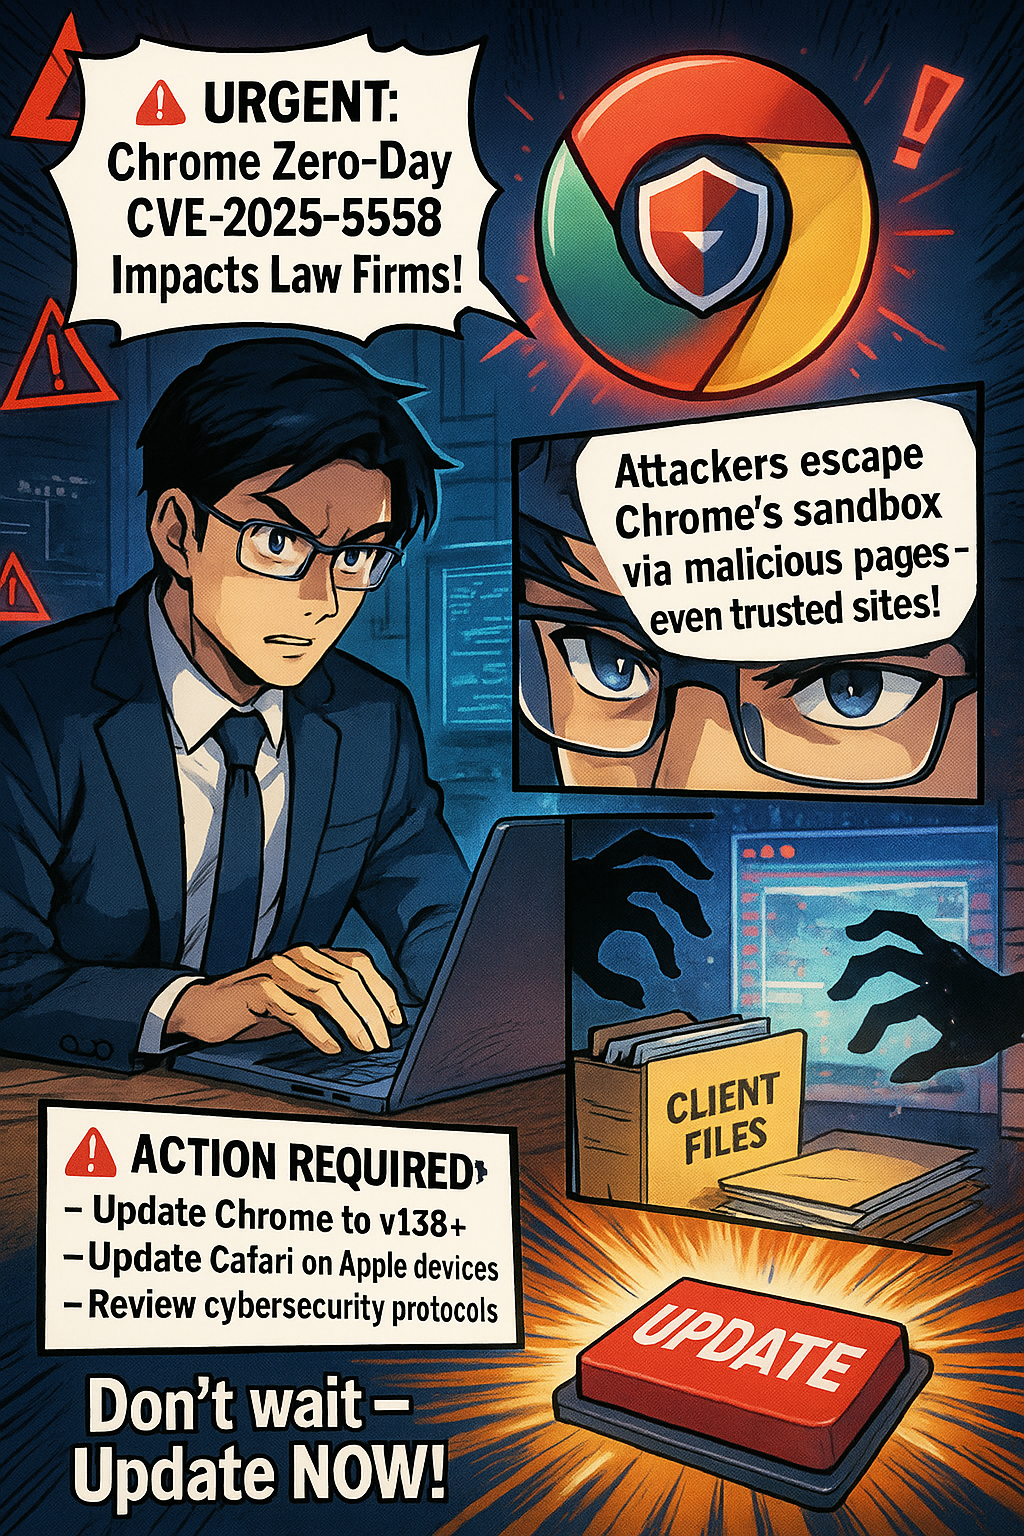
Solo practitioners and small firms should make updating Google Chrome a same-day task. Malwarebytes reports that Chrome’s current desktop update includes 327 security fixes, including 10 critical vulnerabilities, and that certain flaws can be triggered simply by visiting a malicious website. For a law practice handling confidential client communications, privileged work product, and sensitive financial data, that is a risk worth addressing immediately.
Chrome’s stable release has been updated to version 152.0.7977.64/.65 for Windows and Mac, and 152.0.7977.64 for Linux. The update addresses, among other issues, a critical flaw in ANGLE, Chrome’s graphics translation component, identified as CVE-2026-79282. Malwarebytes says a remote attacker could exploit that flaw through a crafted web page to execute arbitrary code outside Chrome’s browser sandbox.
That phrase—“outside the sandbox”—matters. Browser sandboxing is designed to contain web content so that a malicious site cannot easily reach the rest of the computer. A flaw that permits code execution beyond that boundary can give an attacker a path from a single web visit to the underlying operating system. That is precisely the sort of exposure lawyers should avoid when working in a browser alongside client portals, email, cloud document systems, court filing platforms, banking tools, and AI services. ⚖️
The update also remediates CVE-2026-78899, a use-after-free vulnerability in Chrome’s V8 JavaScript engine. It has a reported CVSS score of 8.8 out of 10. Even though successful exploitation occurs inside the browser sandbox, it should not be dismissed. Attackers frequently combine vulnerabilities in a chain, using one weakness to gain an initial foothold and another to widen access.
Why this is a legal-ethics issue!
its a team effort - remind your fellow lawyers to update their chrome browser today!
Technology hygiene is no longer separate from professional responsibility. ABA Model Rule 1.1 requires competent representation, and Comment 8 specifically calls on lawyers to keep abreast of “the benefits and risks associated with relevant technology.” A lawyer does not need to become a cybersecurity engineer. But maintaining a reasonably secure browser—the primary doorway to modern legal work—is a basic and manageable safeguard.
Model Rule 1.6(c) is equally relevant. It requires lawyers to make reasonable efforts to prevent unauthorized access to, or inadvertent disclosure of, client information. An unpatched browser can become an avoidable weak point in that effort. A compromised browser session could expose client documents, credentials, confidential messages, cloud-storage access, or data entered into web forms. 🔐
For firms, this update is also a reminder to think beyond the individual lawyer’s device. Rule 5.1 requires partners and managers to make reasonable efforts to ensure that firm-wide practices conform to professional obligations. Rule 5.3 similarly requires appropriate oversight of nonlawyer assistants. In practical terms, that means someone should own the checklist: browser updates, operating-system patches, password-manager deployment, multifactor authentication, and employee awareness.
Update Chrome now
On a Windows or Mac computer:
Open Chrome.
Select the three-dot More menu in the upper-right corner.
Choose Settings.
Select About Chrome.
Allow Chrome to download any available update.
Restart the browser to complete installation. 🔄
Chrome typically updates itself, but automatic updates can lag when the browser remains open for days, a restart is postponed, or an extension interferes with the update process. Malwarebytes specifically notes that manually checking can ensure the update is applied rather than merely downloaded.
This is a two-minute task with a potentially significant payoff. Before opening that unfamiliar link, reviewing a shared file, or logging into a client-facing platform, take a moment to confirm that Chrome is current. Security is not a one-time purchase or a single policy document. It is a set of small, repeatable habits that protect the practice and the people who trust it.
Bottom line: update Chrome, restart it, and encourage everyone in your firm to do the same today. ✅