WoW: The Meaning of "eSIM" for Lawyers: What It Is, Why It Matters, and How to Switch Carriers Without Compromising Client Data 📱⚖️

eSIMs for Lawyers: Smarter Mobile Security and Client-Data Protection

eSIM is short for “embedded SIM.” It is the digital replacement for the small plastic SIM (subscriber identity module) card that once connected your phone to a wireless carrier.

For most lawyers, eSIM is not exciting because it is new. It matters because it changes how quickly you can activate a phone, change carriers, add a work line, travel internationally, and recover from a lost or damaged device. It also changes parts of your firm’s mobile-security workflow. 🔐

If you recently read my post, “MTC: Apple Upgrade Lease vs. Buying vs. Carrier Financing — Which iPhone 18 Pro Deal Actually Works for Solo and Small Firm Lawyers?,” you know that phone financing affects more than cash flow. It affects your ability to switch providers, control your device, and manage confidential information. eSIM sits at the center of each issue.

What an eSIM Does

Travel-Ready eSIMs for Lawyers: Stay Connected, Protect Client Data

A traditional SIM card is a physical chip. Your carrier activates it. You place it in your phone. The chip identifies your cellular account to the network.

An eSIM performs the same basic function. The key difference is that the SIM is built into the device. Your carrier sends a digital activation profile to the phone. In many situations, you can set up service through an app, a QR code, or the phone’s settings.

That can make a new-phone setup faster. It can also make a second line easier to manage.

For example, a solo lawyer might use:

  • One eSIM line for firm calls and text messages.

  • A second eSIM line for personal use.

  • A temporary travel eSIM for data outside the United States.

  • A replacement eSIM after a lost or stolen phone.

The technology is useful. It is not self-managing.

Why eSIM Matters to Law Practice

eSIM Security for Lawyers: Prevent SIM Swaps and Account Takeover

Your phone may be your camera, recorder, authenticator, document scanner, password-manager vault, email terminal, and client-communication device. The prior iPhone 18 Pro analysis described it accurately as a “filing cabinet, a camera, and a recorder for privileged material.”

eSIM does not itself store your client files. It does, however, control a critical part of your identity on the mobile network: your phone number.

That matters because many firms still use text-message codes as a multifactor-authentication method. A criminal who takes control of your mobile number may receive those codes. That risk is commonly known as a SIM-swap attack.

The attacker may persuade or manipulate a carrier into transferring your number to another device. With access to your number, the attacker may try to reset passwords for email, banking, cloud storage, practice-management software, or other accounts.

eSIM reduces the need to handle a physical SIM card. It does not eliminate account-takeover risk. A carrier can still transfer a number digitally. Your security must therefore extend beyond the phone itself. 🛡️

The ABA Ethics Connection

ABA Model Rule 1.1 requires competent representation. Comment 8 explains that competent lawyers should keep abreast of the benefits and risks associated with relevant technology. An eSIM is not a specialty topic anymore. It is part of ordinary smartphone use.

ABA Model Rule 1.6(c) requires lawyers to make reasonable efforts to prevent the unauthorized disclosure of, or unauthorized access to, client information. If a compromised phone number helps an attacker access your email, cloud account, or case-management platform, the consequences can extend far beyond a missed call.

The ABA Model Rules also identify Rule 5.3, concerning responsibilities regarding nonlawyer assistance. Your carrier, device-management provider, IT consultant, and cloud vendors all play roles in your technology environment. You remain responsible for making reasonable choices and supervising the systems on which your practice depends.

No ethics rule requires a particular carrier or authentication app. The rules do require reasonable safeguards that fit the sensitivity of the information you handle.

Five Practical eSIM Safeguards

Secure eSIM Strategies for Lawyers Protecting Confidential Client Information

  1. Set a carrier account PIN or passcode. Do not reuse your phone unlock code. Ask your carrier about number-port-out protection or transfer locks.

  2. Use an authenticator app or hardware security key when available. Avoid relying exclusively on text-message authentication for critical accounts. Text messages are convenient. They are not the strongest option.

  3. Separate firm and personal use thoughtfully. A dual-SIM setup can help. It does not substitute for a written mobile-device policy, strong passcodes, encryption, and remote-wipe capability.

  4. Treat carrier changes as security events. Confirm which accounts use your mobile number for recovery. Update authentication methods before moving a number to a new carrier or device.

  5. Document the offboarding process. Before returning, trading in, or replacing a phone, migrate data, transfer authentication access, remove the old device from firm accounts, and complete a secure wipe. That is especially important if you lease hardware or use annual-upgrade programs.

eSIM and Carrier Lock-In

eSIM makes changing service technically easier. Carrier financing can make it financially harder.

As discussed in the iPhone 18 Pro financing post, some promotions spread bill credits over 36 months. If you cancel, change carriers, or pay off the phone early, the remaining credits may disappear and the unpaid device balance may become due. The phone may be easy to activate elsewhere. The contract may not be easy to leave.

That distinction matters for solo and small-firm lawyers. Flexibility has value. A law practice may need to change carriers because of coverage, cost, travel, office relocation, client-service needs, or a security concern.

Do not let a “free phone” offer obscure a three-year commitment. Review the device agreement. Review the carrier’s transfer rules. Confirm what happens to your bill credits before you move your number. 💡

The Bottom Line

eSIM Flexibility vs. Carrier Lock-In for Modern Law Practices

eSIM is a useful technology. It supports faster activation, multiple lines, and more flexible service arrangements. Yet it also turns your phone number into an even more important security asset.

Treat your mobile number like a key to the firm. Protect it with a carrier PIN. Reduce dependence on text-message authentication. Plan carrier transitions. Include eSIM transfers in your device-replacement checklist.

Technology competence is not about chasing every new feature. It is about understanding how the technology you already carry affects client confidentiality, firm continuity, and professional judgment. 📲
🚨 BOLO: Chrome Security Update: Law Firms Should Patch Before Browsing Again 🚨

lawyers keep your work secure, update your softwarE - update your google chrome browser now!

Solo practitioners and small firms should make updating Google Chrome a same-day task. Malwarebytes reports that Chrome’s current desktop update includes 327 security fixes, including 10 critical vulnerabilities, and that certain flaws can be triggered simply by visiting a malicious website. For a law practice handling confidential client communications, privileged work product, and sensitive financial data, that is a risk worth addressing immediately.

Chrome’s stable release has been updated to version 152.0.7977.64/.65 for Windows and Mac, and 152.0.7977.64 for Linux. The update addresses, among other issues, a critical flaw in ANGLE, Chrome’s graphics translation component, identified as CVE-2026-79282. Malwarebytes says a remote attacker could exploit that flaw through a crafted web page to execute arbitrary code outside Chrome’s browser sandbox.

That phrase—“outside the sandbox”—matters. Browser sandboxing is designed to contain web content so that a malicious site cannot easily reach the rest of the computer. A flaw that permits code execution beyond that boundary can give an attacker a path from a single web visit to the underlying operating system. That is precisely the sort of exposure lawyers should avoid when working in a browser alongside client portals, email, cloud document systems, court filing platforms, banking tools, and AI services. ⚖️

The update also remediates CVE-2026-78899, a use-after-free vulnerability in Chrome’s V8 JavaScript engine. It has a reported CVSS score of 8.8 out of 10. Even though successful exploitation occurs inside the browser sandbox, it should not be dismissed. Attackers frequently combine vulnerabilities in a chain, using one weakness to gain an initial foothold and another to widen access.

Why this is a legal-ethics issue!

its a team effort - remind your fellow lawyers to update their chrome browser today!

Technology hygiene is no longer separate from professional responsibility. ABA Model Rule 1.1 requires competent representation, and Comment 8 specifically calls on lawyers to keep abreast of “the benefits and risks associated with relevant technology.” A lawyer does not need to become a cybersecurity engineer. But maintaining a reasonably secure browser—the primary doorway to modern legal work—is a basic and manageable safeguard.

Model Rule 1.6(c) is equally relevant. It requires lawyers to make reasonable efforts to prevent unauthorized access to, or inadvertent disclosure of, client information. An unpatched browser can become an avoidable weak point in that effort. A compromised browser session could expose client documents, credentials, confidential messages, cloud-storage access, or data entered into web forms. 🔐

For firms, this update is also a reminder to think beyond the individual lawyer’s device. Rule 5.1 requires partners and managers to make reasonable efforts to ensure that firm-wide practices conform to professional obligations. Rule 5.3 similarly requires appropriate oversight of nonlawyer assistants. In practical terms, that means someone should own the checklist: browser updates, operating-system patches, password-manager deployment, multifactor authentication, and employee awareness.

Update Chrome now

On a Windows or Mac computer:

  1. Open Chrome.

  2. Select the three-dot More menu in the upper-right corner.

  3. Choose Settings.

  4. Select About Chrome.

  5. Allow Chrome to download any available update.

  6. Restart the browser to complete installation. 🔄

Chrome typically updates itself, but automatic updates can lag when the browser remains open for days, a restart is postponed, or an extension interferes with the update process. Malwarebytes specifically notes that manually checking can ensure the update is applied rather than merely downloaded.

This is a two-minute task with a potentially significant payoff. Before opening that unfamiliar link, reviewing a shared file, or logging into a client-facing platform, take a moment to confirm that Chrome is current. Security is not a one-time purchase or a single policy document. It is a set of small, repeatable habits that protect the practice and the people who trust it.

Bottom line: update Chrome, restart it, and encourage everyone in your firm to do the same today. ✅

MTC: Claude Can Answer Your Emails. Why Lawyers Should Not Let AI Just Send Them Unreviewed. 🤖⚖️

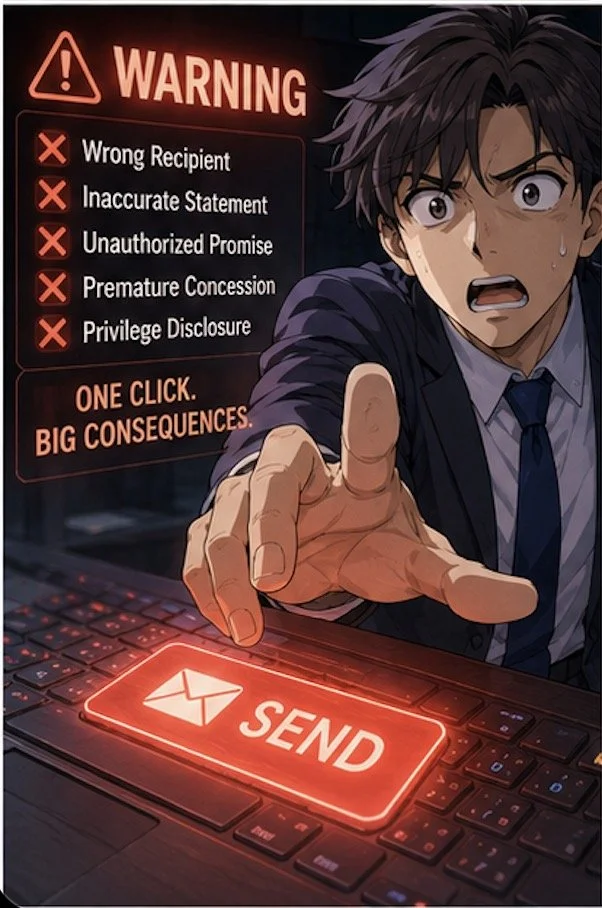
One Click, Big Risk: AI Email Ethics for Lawyers!

David Nield’s recent Lifehacker experiment, “I Let Claude Answer My Emails for Me, and Here’s How It Went,” is worth every lawyer’s attention. Not because it reveals a spectacular AI failure. It does something more useful: it shows how competent-looking AI email automation can create professional risk precisely because it often appears to work.

Claude can now connect to Gmail, search an inbox, summarize messages, draft replies, and send emails from the connected account. The feature’s default settings are cautious: automatic sending is off unless the user changes permissions. But users can authorize individual actions—such as searching, sending, or editing labels—to “Never allow,” “Always allow,” or “Always ask for permission.”

For ordinary personal email, that may be a reasonable productivity choice. For lawyers, it demands a much more careful analysis. A law-firm email is not simply a unit of inbox administration. It may be a communication to a client, opposing counsel, a tribunal, an agency, an expert, a witness, or an insurer. It may convey legal advice, create reliance, disclose strategy, make a representation, accept a deadline, or become an exhibit.

That is why the distinction between AI-assisted drafting and AI-authorized sending matters so much. The first can be useful. The second can amount to unsupervised legal communication.

The Most Important Detail

Nield gave Claude permission to send messages automatically, but he did not test the feature with his actual editors. He decided that a hallucinated misunderstanding was not worth risking and instead conducted the experiment through an exchange with a secondary email account. That was a sensible safeguard. It is also the heart of the legal-tech lesson. 🔍

If a technology writer worries that an AI-generated email might create confusion with an editor, lawyers should recognize the dramatically higher stakes of their own communications.

Consider a few routine examples:

  • An AI responds to opposing counsel: “We agree to the requested extension.”

  • An AI tells a client: “You should withdraw the appeal and refile later.”

  • An AI replies to an agency representative: “We have no additional responsive documents.”

  • An AI responds to a settlement inquiry: “My client is prepared to accept that proposal.”

  • An AI tells a witness: “You do not need to preserve those messages.”

Each could be inaccurate, incomplete, premature, unauthorized, or inconsistent with the client’s objectives. Each could create avoidable procedural, strategic, ethical, or malpractice exposure.

The danger is not only an obvious hallucination. It is a plausible sentence sent at the wrong time, to the wrong recipient, with an unintended implication.

Competence Requires More Than Turning It On

AI Email Assistants Transform Legal Workflows With Human Oversight!

ABA Model Rule 1.1 requires competent representation. Comment 8 specifically directs lawyers to keep abreast of the benefits and risks associated with relevant technology.

That obligation does not mean a lawyer must master the underlying architecture of a large language model. It does mean a lawyer must understand what the tool can access, what it can do, what it may get wrong, and what controls exist before adopting it in a client-facing workflow.

Claude’s Gmail integration illustrates why that inquiry matters. The system can understand labels, dates, contacts, subject lines, themes, and context. It can identify a recent message, carry information through a thread, and compose a reply based on instructions. It can also use connected Google Drive data to prepare a work summary and fold that material into an outgoing email.

Those are real capabilities. They are also real risk surfaces. A connected inbox and Drive account may contain privileged communications, work product, medical records, personnel documents, settlement analyses, client financial information, litigation strategy, and confidential drafts.

Before connecting an AI platform to firm email or cloud storage, lawyers should ask:

  • What email and document data can the system retrieve?

  • What information is retained, logged, or used to improve the service?

  • Does the vendor contractually prohibit training on the firm’s data?

  • Who may access data at the provider, and where is it stored?

  • Can the firm restrict access by user, matter, mailbox, sender, or document type?

  • Can the firm produce an audit trail showing what the AI accessed, drafted, and sent?

  • What happens to the firm’s data when the subscription ends?

Those questions are not technology trivia. They are part of competent vendor assessment.

The “Cheers” Problem Is Not Trivial

Balancing AI Innovation With Human Judgment in Legal Practice

In Nield’s test, Claude composed a generally acceptable message. Yet it signed the email with “cheers,” a phrase the author said he would not ordinarily use. That small mismatch is revealing. Claude had not merely organized information. It had made a communicative choice in someone else’s name.

For a lawyer, voice is not just branding. Tone can convey firmness, concession, uncertainty, urgency, skepticism, hostility, openness to settlement, or a willingness to cooperate. A message that is “a little generic,” as Nield described Claude’s output, may be harmless when discussing weather and a meeting with oneself. It may be harmful in a dispute where each word will be parsed for meaning. ✉️

An email that begins, “We are happy to work with you,” may convey a strategic position that the lawyer did not intend. A reply that omits one key qualification can alter the practical meaning of a settlement discussion. A bot that tries to be helpful may include a fact from a prior thread that should not be repeated, or it may summarize a client’s situation so broadly that it creates a misleading record.

Lawyers should not equate grammatically fluent text with sound legal judgment.

Rules 1.2, 1.4, and 1.6

ABA Model Rule 1.2 requires lawyers to abide by a client’s decisions concerning the objectives of representation and to consult with the client about the means of pursuing those objectives. An AI system cannot determine whether accepting an extension, offering a document, softening a demand, or answering a client’s question advances those objectives.

Rule 1.4 requires appropriate client communication. An AI-generated reply can appear reassuring while omitting necessary advice, misunderstanding the issue, or providing a client with an answer that no lawyer has evaluated. A client should not receive what appears to be legal counsel when it is actually unreviewed probabilistic text.

Rule 1.6 is equally central. Lawyers must not reveal information relating to representation without authorization, subject to limited exceptions. Giving an AI provider access to email and Drive is not automatically unethical, but it requires reasonable diligence and safeguards. The more expansive the permission, the more careful the analysis must be. 🔒

A lawyer who enables automatic sending compounds the issue. Now the system is not only reading protected information; it may also select, summarize, and transmit it externally.

When AI Bots Email Each Other

Nield also raises a concern that lawyers should not dismiss: the prospect of AI systems emailing other AI systems “into infinity.”

That is more than a philosophical concern in legal practice. Imagine two firms each authorizing AI assistants to respond automatically. One system writes, “We can accommodate a brief extension.” The other interprets that as agreement, sends a confirmation, and then proposes a revised deadline. The first system responds with language suggesting continued assent.

Neither lawyer may have reviewed the exchange until a dispute arises. Yet both sides may face a written record that appears to memorialize an agreement.

The proper response is not to ban AI from legal email. It is to preserve human responsibility at the point of external communication.

The Right Workflow

Legal Technology Works Best when lawyers balance Ethics, Trust, and Accountability!

AI can help lawyers manage an overloaded inbox. It can identify urgent messages, group correspondence by matter, summarize long threads, retrieve relevant prior communications, and prepare a first draft. Those uses can reduce administrative burden and create time for legal analysis. ✅

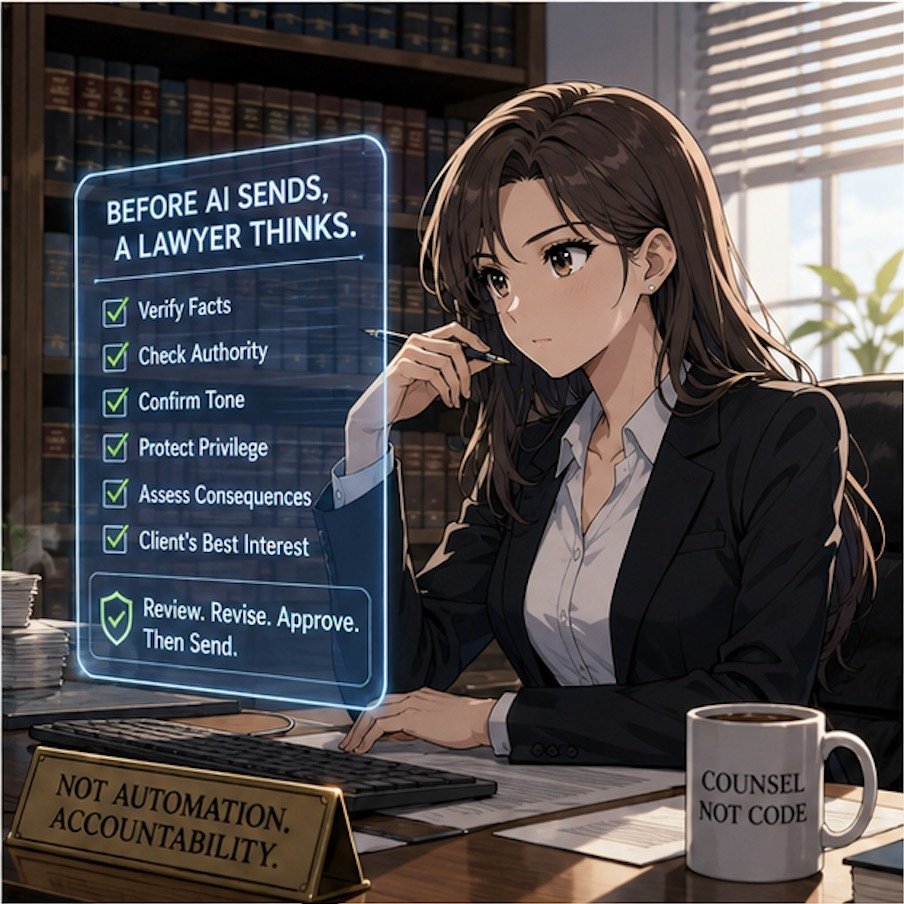
But law firms should adopt a bright-line rule: No AI system may automatically send a substantive external communication without human review and approval.

A practical protocol should require the reviewing lawyer or trained staff member to:

  • Read the full thread and relevant attachments.

  • Confirm the recipient and email address.

  • Verify every factual assertion and deadline.

  • Check for client commitments, concessions, and settlement implications.

  • Remove unnecessary confidential information.

  • Confirm that the message reflects the lawyer’s actual voice, judgment, and strategy.

  • Send the communication only after that review is complete.

Claude’s Gmail feature is impressive. It can make email easier. But as Nield’s own decision to test it only with himself demonstrates, capability is not the same as reliability, and reliability is not the same as professional responsibility.

For lawyers, the governing principle should be simple: let AI prepare the draft; let a responsible human decide whether it should ever leave the outbox. ⚖️

MTC